Article
What To Do When A Hacker Encrypts Your Data
Combating Ransomware
Cyber Threats
RANSOMWARE, RANSOMWARE...
It’s the boogeyman looming in the corners of every digital task we do. Even businesses that don’t operate primarily online have data points that can be exploited, and hackers are always on the lookout for those with poor cyber health.
[This article originally appeared in Risk & Insurance at:
We Talk About Ransomware All the Time. So What Do We Actually Do When a Hacker Has Our Data? : Risk & Insurance (riskandinsurance.com)]
The cost of an attack is growing, too. As Gallagher reported in its 2022 Cyber Insurance Market Conditions Report, during the first six months of 2021, $590 million were paid in ransom payments, as opposed to $416 million paid in all of 2020.
While we talk about best practices to protect ourselves, how often do we flip the conversation and look at the steps we must take when a hack actually occurs? “Unfortunately, no one is safe from ransomware,” said Evgueni Erchov, head of security research & strategy, Arete.
“The most sophisticated groups can focus on larger organizations … but we also see the small companies being targeted all the time.”
Erchov is an experienced hacker negotiator, with more than 20 years in IT security, application development, cybercrime investigations, computer forensics, cryptocurrency blockchain and cyber threat intelligence analysis.
Erchov, alongside John Farley, managing director, cyber practice, at Gallagher, put on a recent webinar on what to do when a hacker strikes, running through a simulated hack to give businesses recovery tips.
The presentation, “What Really Happens When You Negotiate With a Hacker: An Insider’s View,” illuminated several key points, from how to communicate with hackers, where to gather cryptocurrency if a hacker demands it, and what conversations with underwriters should look like when reviewing cyber controls.
Getting in Touch with Your Hacker
Believe it or not, hacking is a business, and hackers treat what they do as such.
Organized criminals work together to suss out vulnerable targets — from a large corporation all the way down to the neighborhood corner store. If the business has the capability to store data — credit card info, health records, trade secrets, you name it — the business is a viable target.
When a hacker infiltrates a system, the language used in their demand can follow a similar pattern. Hackers will note the data they have access to — employee personal records, partner and client data, financial and accountant documents — and how they intend to gain ransom for encrypting these files.
Next steps will focus on how to communicate with the hacker.
“It depends on how sophisticated the group is,” Erchov said. “Sometimes a ransom note will contain an email address that will be used to go back and forth and negotiate a ransom.”
Money and Extortion: How Demands Lives Have Changed
“In the old days, five or six years ago, we had hackers typically freezing our data, we had extortion, but if you didn’t pay, you just didn’t get your data back,” Farley said.
The scare tactics being used by hackers are changing.
In the simulation during the presentation, the fictive hacker threatens to reveal extremely sensitive data from the company CEO if they don’t receive $1 million in bitcoin within five days. To prove how serious they are, the hacker sends an excerpt of that sensitive info.
Extortion and double extortion are commonplace for hackers these days, Erchov said.
“That really happens quite often, on average, close to 70% of cases nowadays will involve data exfiltration along with the encryption,” he said.
It’s a tactic used to encourage payment, because it not only involves the encryption of sensitive data, but it also hangs corporate reputation in the balance. The ransom becomes more than just retrieving data; it becomes about keeping that data out of public hands.
Bitcoin: How the Heck Do I get My Hands on That?
Once the decision to pay the hackers is made, the next issue is figuring out how to follow through. More hackers are demanding bitcoin payments in their ransoms, but not all companies are working in bitcoin.
So then, what do companies do when their data is held for ransom?
As noted by Farley and Erchov, people believe the first place to go for bitcoin is their cyber insurer. But this is not correct.
“The forensic investigator … the company that deals with forensic investigation and interim response, that’s typically the company that will be handling that,” Erchov said.
However, the cyber insurer can be there to guide the process.
“The beauty of the cyber insurance policy is that you have access to these companies [like a forensic investigation company] that have access to bitcoin and can facilitate the payments,” added Farley.
Forensic investigation companies are often operating on a 24/7 basis as well, and the cyber insurance policy acts as a bridge between client and forensics.
Farley noted these payments are also on reimbursement, so the cyber policy is typically designed to reimburse ransoms after the fact.
The Decision to Negotiate
While paying a hacker immediately to get encrypted data back seems like a no brainer, sometimes negotiating down the ransom is the best line of action, especially if a ransom demand is really large or unfeasible.
But what if low-balling a hacker leads to a bigger data leak?
“They almost expect the initial demand is not going to be paid,” said Erchov.
But it’s important to partner with a negotiator, he said, because the negotiation strategist knows what is a reasonable offer versus what could anger the hacker.
The good news: On average, hackers will negotiate down a ransom by 70%, according to Erchov, based on the cases his company Arete has dealt with in the past.
But that depends on several different factors.
“Potentially, the backups might be available. So in that case, if we only have to negotiate for promise of data deletion, it gives us additional leverage because we don’t need a decryption tool,” Erchov gave as an example.
Questions Your Underwriter Will Ask
“We have a very hard cyber insurance marketplace today,” said Farley. “We’re in a place where ransomware and other factors are really getting the underwriting community very nervous.”
Because of the risk landscape and the size of demand, rates are increasing. Some entities with less cyber controls in place are facing nonrenewal.
So, how can a company make itself a good risk for an underwriter?
“They are going to have a lot of questions for you,” said Farley. He noted his list was not all encompassing, but these are key areas to start.
“Multi-factor authentication. If you don’t have that in place, there’s a chance you might not get underwritten at all,” he said.
Underwriters will also want to see patch management — a written and detailed plan to manage any hacker exploitation. Point detection and response, which is technology used to find a hacker in your system and alert you to them, is another control underwriters like to see.
At the end of the day, the key thing to remember is if your company is on the receiving end of a cyber ransomware event, call your cyber partners immediately.
They will know which resources, from bitcoin, negotiators, forensics and more, will aid in appeasing the hacker and getting your data secured.
Back to Blog Posts

Article
AI Agents Used in Campaign Against PaperCut
In late August, a threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG and MF servers. PaperCut is print management software, and researchers determined that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries. The AI agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078 both security flaws affecting PaperCut software and flagged as actively exploited earlier this month. It is currently unclear if the threat actor is solely focused on access development to be handed off to other affiliated actors, or if they will directly leverage their access to achieve follow-on objectives such as data theft or ransomware deployment.
What’s Notable and Unique
Researchers observed three attack paths following the exploitation of vulnerable PaperCut servers. Threat actors would harvest credentials from LSASS memory and registry secrets to perform pass-the-hash attacks, leverage older unpatched Windows vulnerabilities (CVE-2021-42278 and CVE-2021-42287) to escalate privileges in unpatched environments, or, in some cases, directly add newly created accounts to the Domain Admins group when PaperCut was running with domain-level privileges.
Upon achieving remote code execution and credential harvesting within a self-hosted lab environment, the threat actor deployed hundreds of AI-powered agents that leveraged OpenAI Codex, DeepSeek models, and publicly available offensive security tools, including Mimikatz, SharpHound, Certipy, Rubeus, and Impacket, to automate reconnaissance, exploitation, and post-compromise activities. The attackers subsequently used a DCSync attack to obtain a database dump containing domain credentials.
Analyst Comments
The observed activity demonstrates how threat actors are increasingly leveraging AI and large language models (LLMs) to accelerate cyber operations at unprecedented speed and scale. In this campaign, the adversary progressed from exploit development to remote code execution within hours and, in some cases, achieved Domain Administrator privileges in as little as five minutes. The AI-assisted workflow enabled rapid reconnaissance, exploitation, credential theft, privilege escalation, and lateral movement, allowing the compromise of multiple organizations within seconds. This activity highlights the growing threat posed by AI-enabled adversaries capable of conducting large-scale intrusions with greater efficiency and operational velocity. Organizations affected by the PaperCut vulnerabilities are strongly advised to apply the latest security updates and implement the vendor's recommended mitigation measures to reduce the risk of compromise and unauthorized access.
Sources
Agents Gone Wild: An AI-Orchestrated Global Campaign Against PaperCut NG/MF
AI-powered attack exploited PaperCut flaws to hack 395 organizations
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances

Article
Adversarial AI Evolves from Prompting to Autonomous Attack Workflows
Cybercriminals and state-linked threat actors are increasingly incorporating artificial intelligence (AI) into multiple stages of offensive operations. Rather than relying on AI only for content generation or research, threat actors are now consistently using it to support reconnaissance, vulnerability discovery, credential theft, malware development, social engineering, and activities following initial compromise. The growing use of automated and agent-based workflows is allowing adversaries to coordinate offensive malicious activities with less manual involvement, potentially increasing the speed, scale, and efficiency of future campaigns.
What’s Notable and Unique
In one observed campaign, threat actors used AI to plan, build, and conduct an automated credential-harvesting operation within just several hours, demonstrating how compromised infrastructure can be rapidly repurposed to support larger-scale malicious activity.
Arete has observed several threat groups using AI-assisted capabilities to facilitate the analysis of data obtained during exfiltration so far this year, including INC Ransom, FulcrumSec, and Settra.
Attackers are also attempting to reproduce proprietary AI capabilities. Large-scale automated prompting campaigns have been used to extract information about the behavior and capabilities of proprietary AI models. The use of numerous accounts and intermediary infrastructure can make these activities more difficult to identify and attribute.
Analyst Comments
AI is increasingly becoming an operational component in the threat landscape rather than simply a tool that improves attacker productivity. By connecting reconnaissance, development, credential operations, and other activities through automated workflows, threat actors can conduct campaigns more quickly and reduce reliance on continuous human input. This trend also impacts security requirements for organizations deploying AI technologies. AI models, development environments, cloud resources, identities, repositories, and automated workflows should increasingly be considered interconnected elements of the enterprise attack surface, and organizations should maintain visibility across these areas and ensure that security controls account for both conventional threats and AI-enabled attack techniques.
Sources
GTIG AI Threat Tracker: From Prompting to Autonomy – The Evolution of Adversarial AI

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.

Article
Ransomware Trends & Data Insights: August 2026
Although INC Ransom was the most active ransomware threat group observed in August 2026, overall activity remained relatively distributed across the threat landscape, with approximately 30 unique ransomware and extortion groups, including both established and newly emerged actors, observed during the month. Alongside INC Ransom, Storm, DragonForce, Qilin, and The Gentlemen were among the top five most active threat groups, underscoring the continued diversity and competitiveness of the ransomware ecosystem.
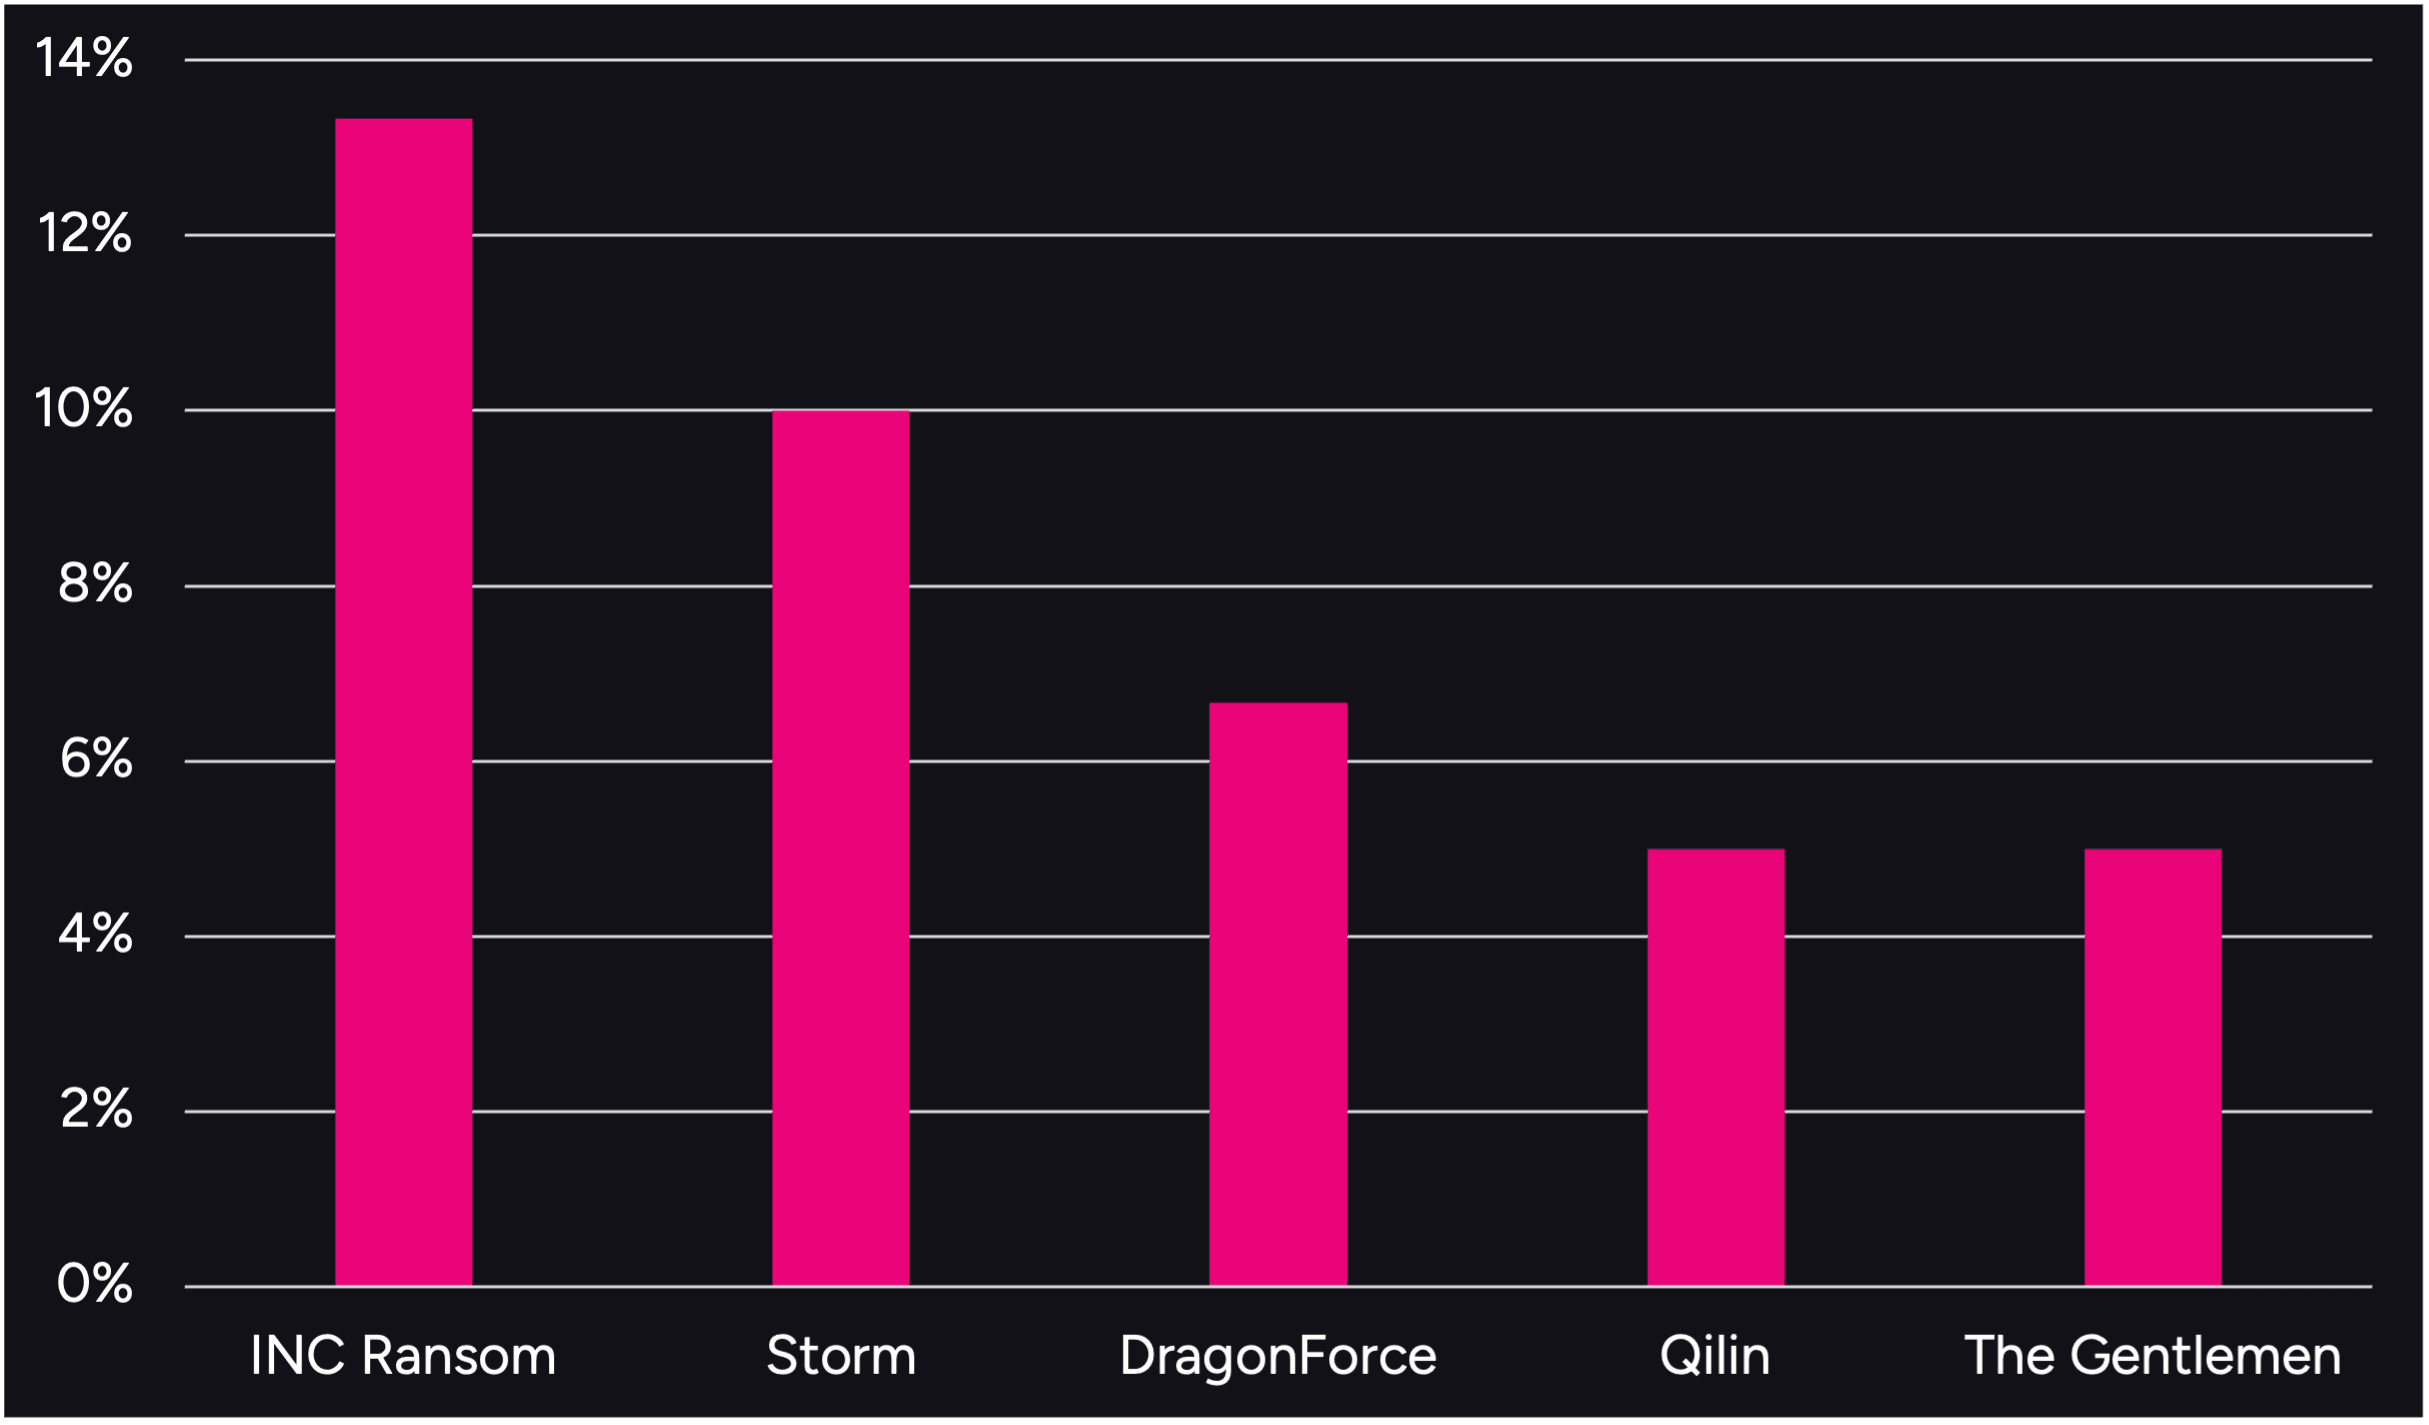
Figure 1. Activity from the top 5 threat groups in August 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
August 2026 was a significant month for the emergence of new threat actors, with Arete identifying several previously untracked ransomware groups, including Storm, Dark Project, DireWolf, Morpheus, Orova, Spirals, Wallstreet Team, and Zawoo Team. This trend underscores the ongoing evolution of the threat landscape and the low barriers to entry for new cybercriminal operations.
Arete observed a continued use of AI-enabled capabilities across the ransomware ecosystem during August. Similar to Fulcrumsec and Setra, the newly emerged Zawoo Team appears to leverage AI-assisted analysis of stolen data, publishing highly structured and detailed victim assessments on its data leak site (DLS). Additionally, both the Aurora and Storm ransomware groups have been observed utilizing AI-driven or AI-assisted chat representatives during victim communications. These developments suggest that threat actors are increasingly incorporating AI to enhance data analysis, automate victim engagement, and improve the effectiveness and scalability of extortion operations.
In August, Arete also observed that despite sustained law enforcement disruption efforts, LockBit continues to demonstrate operational resilience, likely through the expansion of its affiliate ecosystem and the evolution of its tactics. Recent activity indicates an increased reliance on data theft and exfiltration-only operations, with observed victimology suggesting a notable focus on organizations within the financial sector.
Sources
Arete Internal