Article
ALPHV/BlackCat Disruption: Operations Resume
Cyber Threats
Combating Ransomware
Threat Actors
Despite law enforcement’s disruption to ALPHV/BlackCat’s infrastructure in December 2023, the group has since resumed operations. As Arete previously reported, the Federal Bureau of Investigation (FBI) seized the ransomware group’s data leak site (DLS) on December 19, 2023, and obtained victim-specific decryption keys for over 500 ALPHV victims. Before this, the TOR chat sites used to communicate with victims also went offline in early December, causing some affiliates to resort to alternative means of communication, such as Tox chats and email correspondence, to continue efforts to extort money from their victims.
Interestingly, in January 2023 when the FBI infiltrated Hive ransomware’s operations, they gained access to the group’s servers and decryption keys and successfully shut down Hive’s data leak site, negotiation site, and web panels. This ultimately forced the group to cease operating under the Hive brand after the takedown. It remains to be seen whether ALPHV will suffer a similar fate.
What has happened from December 2023 through January 2024?
Unlike the Hive breach, the impact of this recent law enforcement operation against ALPHV seems to have only temporarily disrupted their infrastructure. Arete observed that the group is resuming normal operations.
After the FBI posted a notice on ALPHV’s data leak site stating it had been seized, the ransomware group briefly regained control of the URL and posted that the site had been “unseized.” The group reportedly retained access to the keys used to operate the DLS and used that access to point visitors to a new DLS that appears fully controlled by ALPHV. ALPHV claimed that the FBI only impacted a portion of its operations.
ALPHV began circulating a new URL for their data leak site shortly after the FBI seizure and has posted new victims since December 13, 2023. Although most of the victim content before law enforcement’s action is no longer on their dark web page, the group has continued to add to the new leak site, with over 20 victims posted as of January 16, 2024. The number of victims on the site continues to fluctuate as ALPHV negotiates with victims.
In response to the actions of law enforcement, the group posted new rules, allowing affiliates to target any organization outside of the Commonwealth of Independent States (CIS), including hospitals and critical infrastructure. The new rules also stated that discounts on ransom demands would no longer be given.
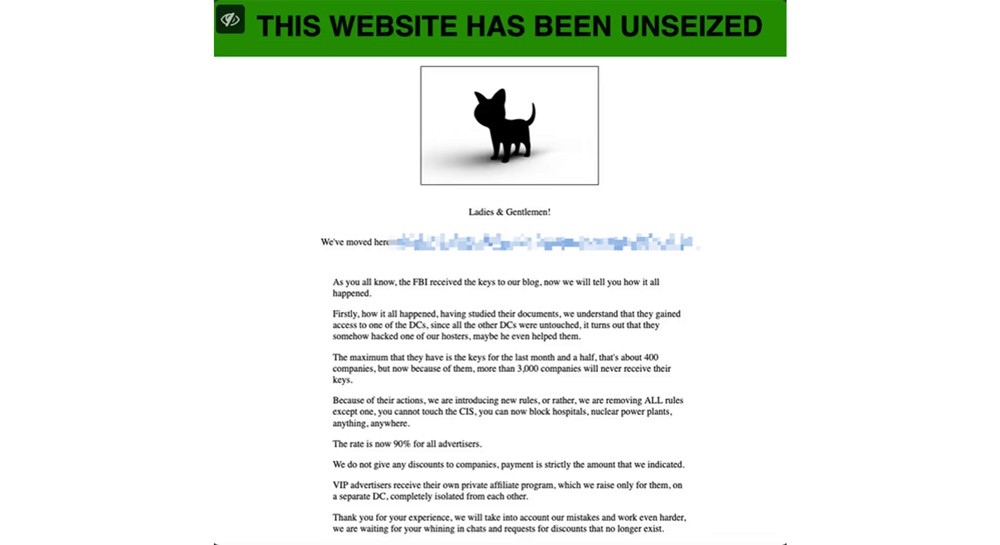
Figure 1 Image of Updated ALPHV rules. Image Source
Since the FBI announcement, Arete observed ALPHV continuing standard ransom communications with its victims contrary to their claims to have changed the rules for affiliates. In late December, the group began using their private TOR chats again to communicate with victims. The new ransom notes include language and naming conventions different from the ones sent to victims before the law enforcement operation. However, the private TOR chats remain the same, displaying a timer and listing a discount price and full price, along with Bitcoin and Monero wallets showing an additional 15% added if payment is in Bitcoin.
Image of ALPHV’s New Data Leak Site
Arete’s Observations
Although the FBI’s operations against ALPHV in December 2023 caused noticeable disruptions to the ransomware group’s ability to operate, law enforcement appeared unable to permanently shut down ALPHV’s infrastructure or operational capabilities, unlike prior law enforcement actions against groups like Hive or REvil. ALPHV appears to be trying to resume its activities in the same manner as before the disruption, reestablishing its data leak site and communicating with new victims on the group’s private TOR sites.
The group’s threats and newly imposed rules appear aimed at projecting strength in the face of the FBI breach rather than representing authentic internal policy changes that affiliates genuinely comply with. Since ALPHV made its public statement in December, Arete observed the group continuing to conduct extortion communications as they did before the disruption, with affiliates still offering discounted prices and showing a willingness to negotiate. While it is too soon to know if there will be a corresponding uptick in attacks against hospitals and critical infrastructure, Arete assesses this would be counterproductive if the group intends to continue operating under the ALPHV/BlackCat brand. The group was already known for attacking the healthcare industry, and future attacks against high-profile targets would lead to even greater attention from law enforcement.
Although ALPHV has been trying to salvage its reputation and resume operations, it is too early to assess whether the group will be able to continue operating as it did prior to law enforcement’s intervention. The knowledge that law enforcement is actively targeting ALPHV will likely deter some affiliates from continuing to work with the group, potentially leading some affiliates to accept active recruitment offers from other Ransomware-as-a-Service (RaaS) groups like LockBit. Even as ALPHV continues to operate, the group may eventually rebrand itself under a different name to complicate further action by law enforcement.
Sources
Back to Blog Posts

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.

Article
Ransomware Trends & Data Insights: August 2026
Although INC Ransom was the most active ransomware threat group observed in August 2026, overall activity remained relatively distributed across the threat landscape, with approximately 30 unique ransomware and extortion groups, including both established and newly emerged actors, observed during the month. Alongside INC Ransom, Storm, DragonForce, Qilin, and The Gentlemen were among the top five most active threat groups, underscoring the continued diversity and competitiveness of the ransomware ecosystem.
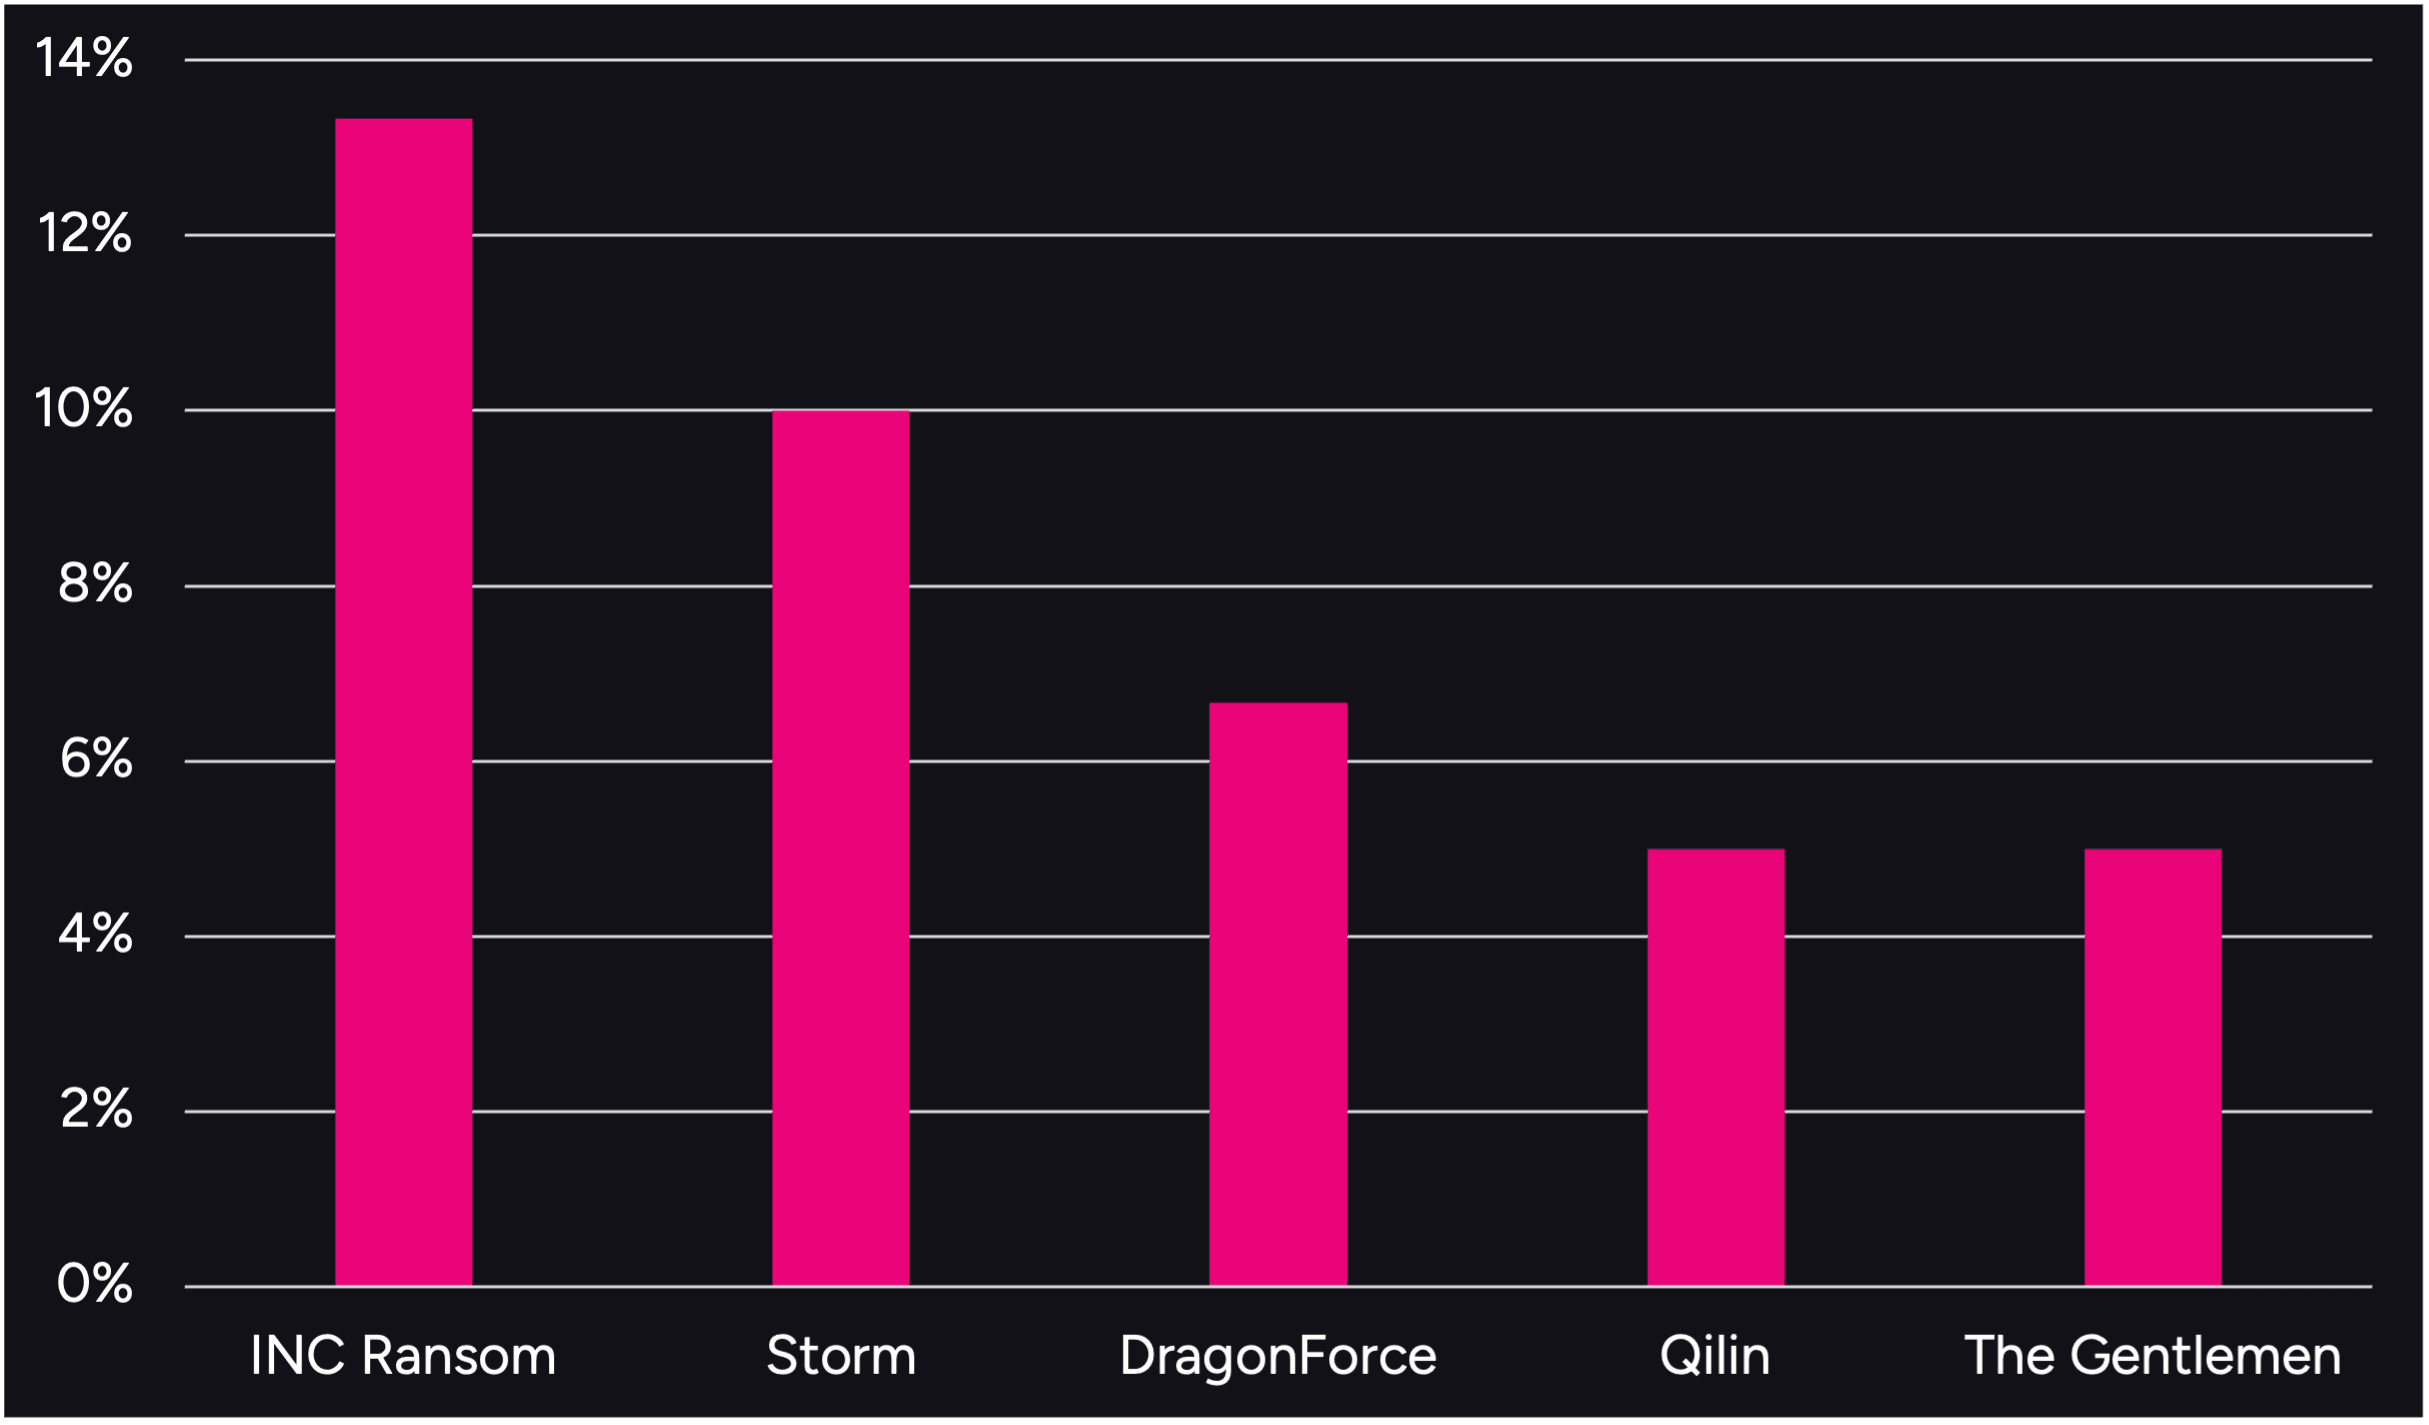
Figure 1. Activity from the top 5 threat groups in August 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
August 2026 was a significant month for the emergence of new threat actors, with Arete identifying several previously untracked ransomware groups, including Storm, Dark Project, DireWolf, Morpheus, Orova, Spirals, Wallstreet Team, and Zawoo Team. This trend underscores the ongoing evolution of the threat landscape and the low barriers to entry for new cybercriminal operations.
Arete observed a continued use of AI-enabled capabilities across the ransomware ecosystem during August. Similar to Fulcrumsec and Setra, the newly emerged Zawoo Team appears to leverage AI-assisted analysis of stolen data, publishing highly structured and detailed victim assessments on its data leak site (DLS). Additionally, both the Aurora and Storm ransomware groups have been observed utilizing AI-driven or AI-assisted chat representatives during victim communications. These developments suggest that threat actors are increasingly incorporating AI to enhance data analysis, automate victim engagement, and improve the effectiveness and scalability of extortion operations.
In August, Arete also observed that despite sustained law enforcement disruption efforts, LockBit continues to demonstrate operational resilience, likely through the expansion of its affiliate ecosystem and the evolution of its tactics. Recent activity indicates an increased reliance on data theft and exfiltration-only operations, with observed victimology suggesting a notable focus on organizations within the financial sector.
Sources
Arete Internal

Report
Arete's H1 2026 Crimeware Report
Explore intelligence and operational data from the frontlines of ransomware and extortion response as we detail the most significant trends and developments in the cyber threat landscape in the first half (H1) of 2026.

Article
WinRAR Path-Traversal Vulnerability Exploited in Ransomware Attacks
CISA has warned that CVE-2025-8088, a path-traversal vulnerability in WinRAR, is being exploited in ransomware attacks. The vulnerability allows attackers to use specially crafted archive files to place malicious executables in locations such as the Windows Startup folder, enabling code execution when the system restarts. WinRAR addressed this vulnerability in version 7.13, but exploitation has continued due to challenges in updating the software. CISA's updated KEV entry now specifically identifies the vulnerability as being used in ransomware attacks.
What’s Notable and Unique
The vulnerability was initially exploited as a zero-day by the Russia-linked RomCom group, enabling malware execution at user logon and supporting credential theft, cyberespionage, and ransomware-related activities.
CVE-2025-8088 continues to be actively exploited by both government-backed and financially motivated threat actors. Observed campaigns have been attributed to Russian- and Chinese-linked groups targeting several organizations.
Phishing campaigns leveraging weaponized RAR attachments exploited CVE-2025-8088 to silently place malicious payloads in autorun locations using directory traversal and Alternate Data Streams (ADS).
The widespread exploitation of CVE-2025-8088 highlights strong demand for effective WinRAR exploits, with multiple underground vendors previously supplying exploit capabilities to a diverse range of threat actors. One such vendor, zeroplayer, advertised a WinRAR exploit in July 2025.
Analyst Comments
Organizations should immediately upgrade WinRAR to version 7.13 or later and conduct an enterprise-wide inventory to identify unmanaged installations. Given that WinRAR lacks automatic updates, Group Policy support, and integration with common enterprise patch management platforms, manual verification and remediation may be required to ensure all vulnerable instances are addressed. Security teams should also enhance defenses against archive-based phishing attacks by blocking or scrutinizing unsolicited compressed files, monitoring for suspicious file creation in Windows Startup directories, and detecting abuse of ADS. With CISA now linking CVE-2025-8088 to ransomware activity, organizations should treat remediation as a high priority and actively monitor for indicators of WinRAR-based exploitation across their environments.
Sources
CISA Adds Three Known Exploited Vulnerabilities to Catalog
WinRAR vulnerability being exploited in ransomware attacks, CISA warns