Article
Avaddon Ransomware Hits AXA
Arete Analysis
Combating Ransomware
Endpoint Detection and Response
Summary
Avaddon ransomware allegedly attacked European insurance provider AXA shortly after the company announced that it will stop paying ransoms for its clients. Our analysis provides an in-depth look at Avaddon’s tactics and recommended mitigations.
_________________________________________________________________________________________________________________________________
From September 2020 to May 2021, Arete responded to nine Avaddon ransomware engagements across varying industry sectors, including professional services, financial services, healthcare, hospitality, public services, and retail.
During the first week of May, Arete received an FBI Liaison Alert System (FLASH) CU-000145-MW from the FBI Cyber Division. The Australian Cyber Security Center (ACSC) also released an alert about an ongoing Avaddon ransomware campaign.
According to reports, at the beginning of May 2021, AXA (one of Europe’s top five insurers) said it will stop reimbursing people in France who pay ransoms after cybercriminals target them with ransomware. It will also stop writing cyber insurance policies that cover customers for extortion payments to ransomware attackers. This decision is said to have come in response to concerns aired by French justice and cybersecurity officials during a recent senate roundtable in Paris about the global ransomware epidemic.
AXA has now found itself a victim of a ransomware breach. Public reports say that the Avaddon ransomware group has impacted AXA Asia Assistance IT operations in Thailand, Malaysia, Hong Kong, and the Philippines. The group claims to have stolen 3 terabytes of data, including ID cards, passport copies, customer claims, reserved agreements, denied reimbursements, payments to customers, contracts and reports, customer IDs, bank account scanned papers, hospital and doctor reserved material (private investigation for fraud), and customer medical reports, including HIV, hepatitis, STD, and other illness reports. According to reports, the ransomware group said AXA had 240 hours to communicate and cooperate or they would start leaking valuable company documents.
While the juxtaposition of the AXA decision to not pay ransoms for French victims or even write ransomware coverage in France could have motivated the attack, Arete has no information or evidence to link these events. In general, and as disclosed in publicly released news reports, attacks against insurance companies are increasing.
In a recent interview, a member of the REvil ransomware gang was asked if they target organizations with cyber insurance. His response:
“Yes, this is one of the tastiest morsels. Especially to hack the insurers first — to get their customer base and work in a targeted way from there. And after you go through the list, then hit the insurer themselves.”
- "Unknown" REvil Ransomware Representative
In its CU-000145-MW FLASH Alert, the FBI notified of activity by cyber actors using Avaddon ransomware-as-a-service (RaaS) to target U.S. and foreign private sector companies, manufacturing organizations, and healthcare agencies. The alert states that the threat actors:
Have compromised victims through remote access login credentials like remote desktop protocol (RDP) and virtual private network (VPN) with single-factor authentication or improperly configured RDP.
Once they gain access to a victim’s network, they map the network and identify backups for deletion and/or encryption. They use malware that escalates privileges, contains anti-analysis protection code, enables persistence on a victim system, and verifies the victim is not located in the Commonwealth of Independent States (CIS). Their ransomware terminates services and processes related to backup and antivirus running in system memory before encrypting victims’ data.
Encrypt and exfiltrate data from the victim network for extortion, threatening its release in their TOR leak site (avaddongun7rngel.onion) if victims don’t pay the ransom.
Will perform a 5% data leak if the ransom is not paid within three to five days and follow with a full leak of the data stolen if the ransom is not paid.
Announced in January 2021 that they would attack victims who do not pay ransoms with distributed denial-of-service (DDoS) attacks.
Have used the following IPs during RDP connections: 185.216.33.0/24, 45.145.67.0/23, 193.27.229.0/23, 217.8.117.63.
The ACSC report includes some of the following tactics, techniques, and procedures (TTPs):
Phishing and malicious email spam (malspam) campaigns to deliver malicious JavaScript files. These are often low in sophistication, containing a threat suggesting the attached file contains a compromising photo of the victim.
Using “double extortion” techniques as coercion and further pressure to pay a ransom, including:
Threatening to publish the victim’s data via the Avaddon Data Leak Site (DLS): avaddongun7rngel.onion.
Threatening the use of DDoS attacks against the victim (first identified in February 2021).
Identify the default geolocation and system language of the user’s device to determine whether the user will be targeted for attack or not.
Use of Windows Scheduled Task to establish persistence.
The report also includes the following information about countries and sectors affected by this threat:
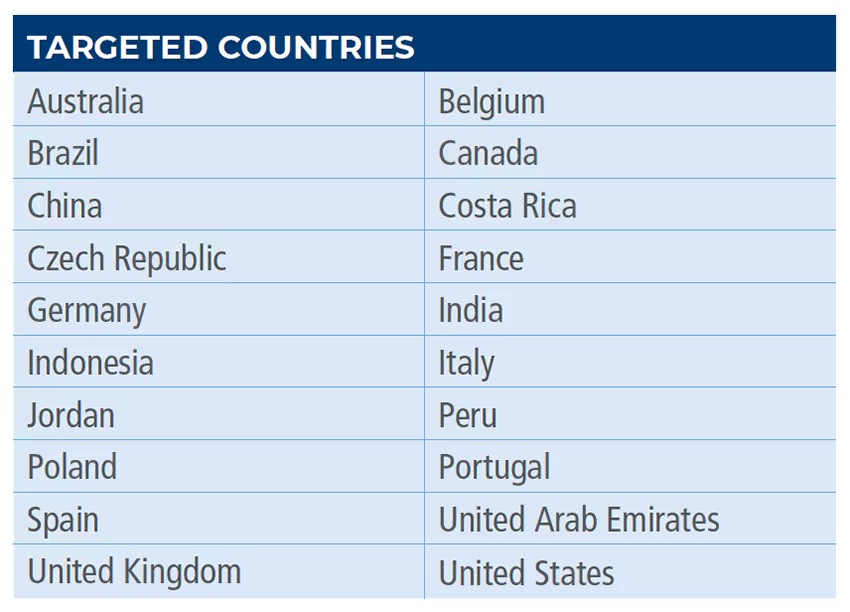
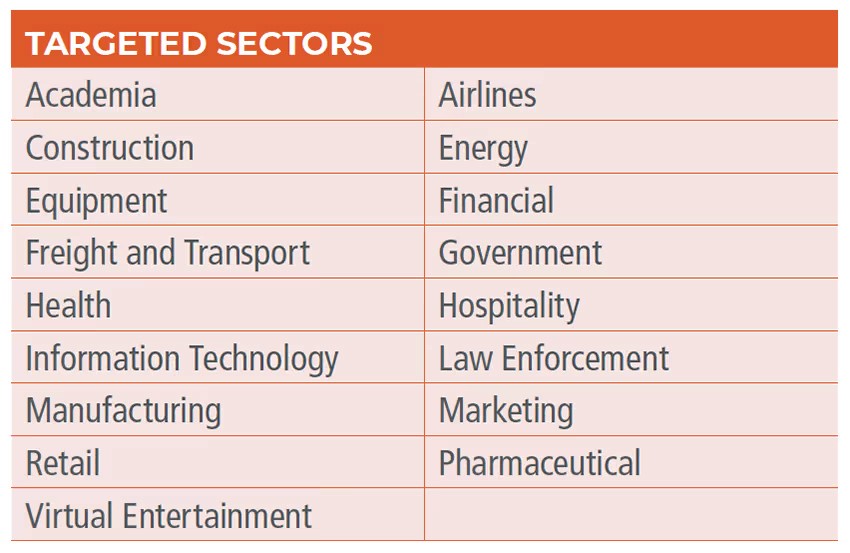
Statistical Data on Avaddon Ransomware From Arete Metrics
The information listed is based on Avaddon cases investigated by Arete IR since September 2020. Our IR and Data Analytics practices work together to track key data points for every ransomware engagement, and our IR practice tracks data points on the ransomware variant and collects statistics based on handled engagements:
Arete has responded to nine Avaddon breach response engagements since September 2020 in the following sectors: Professional Services | Financial Services | Healthcare | Hospitality | Public Services | Retail
At victim/breach coach/carrier request, Arete negotiated and paid the ransom in four of the nine Avaddon cases. In the remaining five cases, we were able to assist the victim in recovering from backups.
Average ransom demand: US$1,089,375.
Maximum ransom demand: US$4,000,000.
Minimum ransom demand: US$15,000.
We observed data exfiltration in 67% of the incidents.
Phishing emails and RDP were the methods of infection 60% of the time.
During investigations, our incident responders have observed threat actors using RDP to remote into the victim environment. We have seen attackers use Mimikatz, Advanced Port Scanner, Advanced IP Scanner, PsExec, Rclone, Gmer, and svhost.exe. We have also seen exe_[victim_org].exe as the ransomware file names.
Mitigation Measures Recommended By The FBI and ACSC
Back up critical data offline.
Ensure copies of critical data are in the cloud or on an external hard drive or storage device.
Secure your backups and ensure data is not accessible for modification or deletion from the system where the data resides.
Use two-factor authentication with strong passwords, including for remote access services.
Monitor cyber threat reporting regarding the publication of compromised VPN login credentials and change passwords/settings, if applicable.
Regularly change passwords to critical systems.
Keep computers, devices, and applications patched and up to date.
Install and regularly update antivirus or antimalware software on all hosts.
Scan emails and attachments to detect and block malware.
Implement a training program and processes to identify phishing and externally sourced emails.
Back to Blog Posts

Article
FortiBleed Campaign Remains Active
The FBI and Secret Service recently warned that the FortiBleed credential-harvesting campaign remains an active threat targeting internet-facing Fortinet FortiGate firewalls and secure socket layer (SSL) virtual private network (VPN) gateways. The agencies report that attackers continue to scan internet-exposed Fortinet firewalls using previously obtained credentials. This has reinforced assessments made by other security researchers, who have stated that “FortiBleed should be treated as an active access operation, not as a one-time credential leak.”
What’s Notable and Unique
FortiBleed, active since February 2026, begins with widespread reconnaissance to identify internet-facing FortiGate firewalls and SSL-VPN services. Once potential targets are identified, operators attempt to gain initial access through credential stuffing, password spraying, and dictionary attacks using previously compromised credentials.
Following successful access, the attackers deploy the Go-based FortigateSniffer tool on compromised appliances. The tool leverages native FortiOS diagnostic functionality to passively intercept authentication traffic across 24 protocols, enabling the collection of cleartext credentials and password hashes passing through the device.
Successfully recovered credentials are reused to expand access, including Active Directory enumeration, Kerberos validation, SMB authentication, and network share discovery, enabling threat actors to move deeper into the victim environment.
Reporting indicates that initial access brokers (IABs) leveraging the FortiBleed attack chain have facilitated access for downstream ransomware operations, including the INC Ransom/Lynx and Payload ransomware groups. This aligns with Arete’s observations of ransomware groups, including INC, Qilin, and DragonForce, targeting Fortinet FortiGate and VPN infrastructure as an initial access vector.
Remediation
Organizations should restrict internet-facing FortiGate management interfaces, rotate administrative and VPN credentials, review local and privileged accounts, and enforce MFA for remote access. If a potential compromise is detected, organizations should isolate affected systems, conduct threat hunting to determine the scope and identify compromised accounts and devices, and preserve relevant logs and artifacts. Organizations should also report the incident to appropriate authorities and implement targeted eviction measures based on identified threat actor activity.
Analyst Comments
FortiBleed represents an ongoing access-enablement threat, rather than a one-time credential exposure. The campaign’s ability to harvest, validate, and reuse credentials can provide sustained access to victim environments and create opportunities for downstream ransomware activity. Organizations with suspected FortiGate exposure should treat the activity as a potential active compromise and investigate for persistent access, compromised accounts, and lateral movement.
Sources
FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts
FBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Device Credentials

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory

Article
Ransomware Trends & Data Insights: September 2026
The Akira ransomware group re-emerged as the most active ransomware threat observed by Arete in September. Overall activity remained relatively distributed among multiple threat groups, with 29 unique groups observed throughout the month. Alongside Akira, INC Ransom and the relatively new Storm group were among the three most active threat actors observed in September. Several new threat groups also emerged during the month, including Hades Team, Shiba, and Vortex (which is suspected to be part of the cluster of threat actors affiliated with the former BlackFile group).

Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
In September 2026, the ShinyHunters threat group escalated its extortion activity by publicly targeting both the Clop ransomware group and the FBI. The group claimed to have breached and defaced Clop’s infrastructure, demanding an eight-figure ransom, while separately alleging the theft of sensitive FBI-related data and demanding the retraction of statements made in a prior public advisory. In both incidents, ShinyHunters employed similar pressure tactics, including website defacements, repeated public postings, and threats of data disclosure.
ClickFix attacks remained prevalent in September 2026, with ransomware groups including Qilin, Helix, and The Gentlemen leveraging ClickFix lures to facilitate PowerShell-based payload execution and initial access. The technique continues to evolve, combining social engineering with legitimate tools and services to enable compromise and evade detection.
September 2026 saw continued activity from the former BlackFile extortion ecosystem. BlackFile, a data theft and extortion operation active since at least October 2025, rebranded as Redact in May 2026, and since appears to have broken off into several affiliated brands, including Pink, Helix, Falcon, Cinder, and potentially Vortex. During September, some affiliates publicly disputed these associations and claimed to operate independently. However, the coordinated timing, messaging, and near-identical nature of these statements support the assessment that these groups remain part of a broader interconnected ecosystem operating under shared objectives or coordination.

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM