Article
Conti Ransomware is the New Ryuk?
Arete Analysis
Summary
Arete’s Threat Intelligence team observed that Conti ransomware could be a rebrand of Ryuk ransomware, as both variants use similar tactics to deploy ransomware executables.
—————————————————————————
Background
Based on analysis of Conti ransomware, which was originally spotted in the wild in February of this year, the Arete Threat Intelligence team believes that this variant is being operated by the same group that conducted Ryuk ransomware attacks in the past. Digital forensics analysis of systems impacted by Conti ransomware revealed that it is generally being deployed by the attackers using the TrickBot banking trojan. Since early 2019, Ryuk ransomware operators exclusively used TrickBot trojan in their operations. In the 1st quarter of 2020, the number of Ryuk ransomware attacks significantly declined while the number of new Conti matters started to rise, which is a secondary indicator of a connection between both variants.
Conti Overview
Conti is a sophisticated ransomware variant that emerged in February 2020. Unlike most of its’ peers, Conti ransomware encrypts files on victims’ machines significantly faster by running 32 concurrent threads and utilizing all computing power that impacted systems have available. As a result of that, devices with multi-core CPUs get encrypted quicker. Conti has the capability to encrypt local hard drives, network shares and other devices on the local network. To encrypt the data, Conti uses the AES-256 encryption key, which is bundled with the RAS-4096 public encryption key (Note: this key is unique for each victim). Since the encryption key is unique for each victim, Conti operators cannot provide a decryption tool, which would work only on specific devices. The Conti decryption tool works on all encrypted systems within a victim’s networks.
Prior to the start of the encryption, Conti leverages Windows Restart Manager to disable security, backups and other applications that may keep files locked on the impacted systems. Then it deletes Shadow Volume copies to make it impossible to use built-in Windows volume backups to restore data after the encryption.
Once encryption completes, the .CONTI extension is added to all encrypted files and the ransom note, CONTI_README.txt, is placed in each folder. Each ransom note contains 2 email addresses to get in touch with the attackers, which are unique for each victim. This method is consistent with what Ryuk operators used in their attacks. Conti operators use a unique set of emails to identify each victim, so it does not matter if a victim responds from a corporate account or from a public email account – attackers still will know which victim they are communicating with. Just like Ryuk, Conti conducts research into information about their victims and sets ransom demands based on what they believe the victim can afford to pay.
Conti Ransom Note
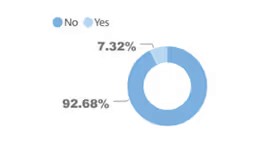
Figure 1 - % of Data Exfiltration in Ryuk matters
It was uncommon for Ryuk to exfiltrate data from victims’ systems. Based on Arete analysis of previous matters, we only observed data exfiltration in 7% of cases. Unlike Ryuk, it appears that Conti ransomware operators decided to join the bandwagon of other 20+ variants that steal data from victims’ environments prior to the encryption. Conti also created a web site where they publish lists of their victims in attempt to improve their chances of getting paid. In the last few weeks, Conti stepped up their extortion attempts and, in some cases, called the owner/managers of companies directly, to inform them that they have been compromised and threaten them to release the stolen data if they don’t pay.
Security Recommendations
Below are a few recommendations that will help to protect your organization from Conti ransomware attacks:
Implement a sophisticated Endpoint Detection & Response (EDR) solution that will rely on behavior analysis, instead of just malware signatures, and have tamper-proof capabilities.
Keep your systems updated and disable SMBv1, to protect against Windows EternalBlue vulnerability, which is actively being used by the TrickBot banking trojan to propagate within a victims’ environment.
Block outbound traffic on your firewall for ports 447, 449 & 8082 (Note: along with 443 those ports are commonly used by TrickBot) and implement geo-blocking for foreign countries that you don’t have any employees in and don’t do business with.
Continuously educate your users on how to identify suspicious phishing emails and attachments.
Implement an off-site backup solution and test it regularly
Figure 2 - Screenshot of the Conti exfil site
Back to Blog Posts

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM

Article
AI Agents Used in Campaign Against PaperCut
In late August, a threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG and MF servers. PaperCut is print management software, and researchers determined that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries. The AI agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078 both security flaws affecting PaperCut software and flagged as actively exploited earlier this month. It is currently unclear if the threat actor is solely focused on access development to be handed off to other affiliated actors, or if they will directly leverage their access to achieve follow-on objectives such as data theft or ransomware deployment.
What’s Notable and Unique
Researchers observed three attack paths following the exploitation of vulnerable PaperCut servers. Threat actors would harvest credentials from LSASS memory and registry secrets to perform pass-the-hash attacks, leverage older unpatched Windows vulnerabilities (CVE-2021-42278 and CVE-2021-42287) to escalate privileges in unpatched environments, or, in some cases, directly add newly created accounts to the Domain Admins group when PaperCut was running with domain-level privileges.
Upon achieving remote code execution and credential harvesting within a self-hosted lab environment, the threat actor deployed hundreds of AI-powered agents that leveraged OpenAI Codex, DeepSeek models, and publicly available offensive security tools, including Mimikatz, SharpHound, Certipy, Rubeus, and Impacket, to automate reconnaissance, exploitation, and post-compromise activities. The attackers subsequently used a DCSync attack to obtain a database dump containing domain credentials.
Analyst Comments
The observed activity demonstrates how threat actors are increasingly leveraging AI and large language models (LLMs) to accelerate cyber operations at unprecedented speed and scale. In this campaign, the adversary progressed from exploit development to remote code execution within hours and, in some cases, achieved Domain Administrator privileges in as little as five minutes. The AI-assisted workflow enabled rapid reconnaissance, exploitation, credential theft, privilege escalation, and lateral movement, allowing the compromise of multiple organizations within seconds. This activity highlights the growing threat posed by AI-enabled adversaries capable of conducting large-scale intrusions with greater efficiency and operational velocity. Organizations affected by the PaperCut vulnerabilities are strongly advised to apply the latest security updates and implement the vendor's recommended mitigation measures to reduce the risk of compromise and unauthorized access.
Sources
Agents Gone Wild: An AI-Orchestrated Global Campaign Against PaperCut NG/MF
AI-powered attack exploited PaperCut flaws to hack 395 organizations
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances

Article
Adversarial AI Evolves from Prompting to Autonomous Attack Workflows
Cybercriminals and state-linked threat actors are increasingly incorporating artificial intelligence (AI) into multiple stages of offensive operations. Rather than relying on AI only for content generation or research, threat actors are now consistently using it to support reconnaissance, vulnerability discovery, credential theft, malware development, social engineering, and activities following initial compromise. The growing use of automated and agent-based workflows is allowing adversaries to coordinate offensive malicious activities with less manual involvement, potentially increasing the speed, scale, and efficiency of future campaigns.
What’s Notable and Unique
In one observed campaign, threat actors used AI to plan, build, and conduct an automated credential-harvesting operation within just several hours, demonstrating how compromised infrastructure can be rapidly repurposed to support larger-scale malicious activity.
Arete has observed several threat groups using AI-assisted capabilities to facilitate the analysis of data obtained during exfiltration so far this year, including INC Ransom, FulcrumSec, and Settra.
Attackers are also attempting to reproduce proprietary AI capabilities. Large-scale automated prompting campaigns have been used to extract information about the behavior and capabilities of proprietary AI models. The use of numerous accounts and intermediary infrastructure can make these activities more difficult to identify and attribute.
Analyst Comments
AI is increasingly becoming an operational component in the threat landscape rather than simply a tool that improves attacker productivity. By connecting reconnaissance, development, credential operations, and other activities through automated workflows, threat actors can conduct campaigns more quickly and reduce reliance on continuous human input. This trend also impacts security requirements for organizations deploying AI technologies. AI models, development environments, cloud resources, identities, repositories, and automated workflows should increasingly be considered interconnected elements of the enterprise attack surface, and organizations should maintain visibility across these areas and ensure that security controls account for both conventional threats and AI-enabled attack techniques.
Sources
GTIG AI Threat Tracker: From Prompting to Autonomy – The Evolution of Adversarial AI

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.