Article
Good Europol Hunting: How Do You Like Them Apples, Emotet?
Combating Ransomware
On January 27, 2021, Europol announced that it had led a coordinated takedown of the Emotet infrastructure in collaboration with law enforcement authorities in the Netherlands, Germany, the United States, the United Kingdom, France, Lithuania, Canada, and Ukraine.
According to Europol, over the course of the operation, it has been able to map out and take control of servers from around the world that Emotet was using as “command-and-control” (C2) nodes. Europol also shared that it would use the seized servers to deactivate Emotet by pushing an update to all infected systems still connecting to the seized C2s. Analysis of the new Emotet updates, which were developed by Europol, shows code that will self-remove the Trojans from infected systems on March 25, 2021, at 12:00 (local time).
“As part of the criminal investigation conducted by the Dutch National Police into EMOTET, a database containing e-mail addresses, usernames and passwords stolen by EMOTET was discovered. You can check if your e-mail address has been compromised. As part of the global remediation strategy, in order to initiate the notification of those affected and the cleaning up of the systems, information was distributed worldwide via the network of so-called Computer Emergency Response Teams (CERTs).”
Source: Europol
The Ukrainian National Police agency also reported making some arrests in connection with this operation.
Mutable currency seized from Emotet
Emotet Overview
Emotet is a sophisticated banking Trojan that security researchers first identified in 2014. Originally, it was designed to steal banking credentials for use in taking over bank accounts and stealing funds from victims. Over the years, its functionality was updated to enable hackers to deploy supplementary malware and steal content from victims’ email systems.
In mid-2018, the Emotet group started to work closely with operators of the TrickBot banking Trojan and Ryuk/Conti ransomware groups. After initial infection, Emotet can stay undetected for weeks, sometimes months, before it eventually deploys the TrickBot Trojan, which can then lead to a subsequent ransomware attack. In the last few months, Emotet has also been seen deploying IcedID and Qbot Trojans, which can also lead to ransomware attacks by the MegaCortex, Prolock, and/or Maze/Egregor variants.
Emotet Risk Assessment
On October 12, 2020, Microsoft announced a similar takedown of the Trickbot infrastructure. In this case, the botnet’s owners were able to rebuild their infrastructure and restart operations in about four weeks. In part, this quick reboot was thanks to the Trickbot banking Trojan having a “fallback” communications module, which uses a blockchain distributed domain name service (DNS) technology called Emercoin DNS (EmerDNS) that law enforcement cannot take over. After the Trickbot operators deployed a new set of C2 servers, they were able to use the fallback channel to update configurations on infected systems.
It’s all about the money. Cold. Hard. Cash.
Unlike Trickbot, Emotet does not have a similar fallback capability and cannot regain access to infected systems to update configurations. Therefore, it will likely take the Emotet group longer to recover and resume operations. Based on the Arete Cyber Threat Intelligence (CTI) team’s assessment, the takedown of the Emotet C2 infrastructure will disrupt this botnet’s operations for at least five to six weeks.
Back to Blog Posts

Article
Adversarial AI Evolves from Prompting to Autonomous Attack Workflows
Cybercriminals and state-linked threat actors are increasingly incorporating artificial intelligence (AI) into multiple stages of offensive operations. Rather than relying on AI only for content generation or research, threat actors are now consistently using it to support reconnaissance, vulnerability discovery, credential theft, malware development, social engineering, and activities following initial compromise. The growing use of automated and agent-based workflows is allowing adversaries to coordinate offensive malicious activities with less manual involvement, potentially increasing the speed, scale, and efficiency of future campaigns.
What’s Notable and Unique
In one observed campaign, threat actors used AI to plan, build, and conduct an automated credential-harvesting operation within just several hours, demonstrating how compromised infrastructure can be rapidly repurposed to support larger-scale malicious activity.
Arete has observed several threat groups using AI-assisted capabilities to facilitate the analysis of data obtained during exfiltration so far this year, including INC Ransom, FulcrumSec, and Settra.
Attackers are also attempting to reproduce proprietary AI capabilities. Large-scale automated prompting campaigns have been used to extract information about the behavior and capabilities of proprietary AI models. The use of numerous accounts and intermediary infrastructure can make these activities more difficult to identify and attribute.
Analyst Comments
AI is increasingly becoming an operational component in the threat landscape rather than simply a tool that improves attacker productivity. By connecting reconnaissance, development, credential operations, and other activities through automated workflows, threat actors can conduct campaigns more quickly and reduce reliance on continuous human input. This trend also impacts security requirements for organizations deploying AI technologies. AI models, development environments, cloud resources, identities, repositories, and automated workflows should increasingly be considered interconnected elements of the enterprise attack surface, and organizations should maintain visibility across these areas and ensure that security controls account for both conventional threats and AI-enabled attack techniques.
Sources
GTIG AI Threat Tracker: From Prompting to Autonomy – The Evolution of Adversarial AI

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.

Article
Ransomware Trends & Data Insights: August 2026
Although INC Ransom was the most active ransomware threat group observed in August 2026, overall activity remained relatively distributed across the threat landscape, with approximately 30 unique ransomware and extortion groups, including both established and newly emerged actors, observed during the month. Alongside INC Ransom, Storm, DragonForce, Qilin, and The Gentlemen were among the top five most active threat groups, underscoring the continued diversity and competitiveness of the ransomware ecosystem.
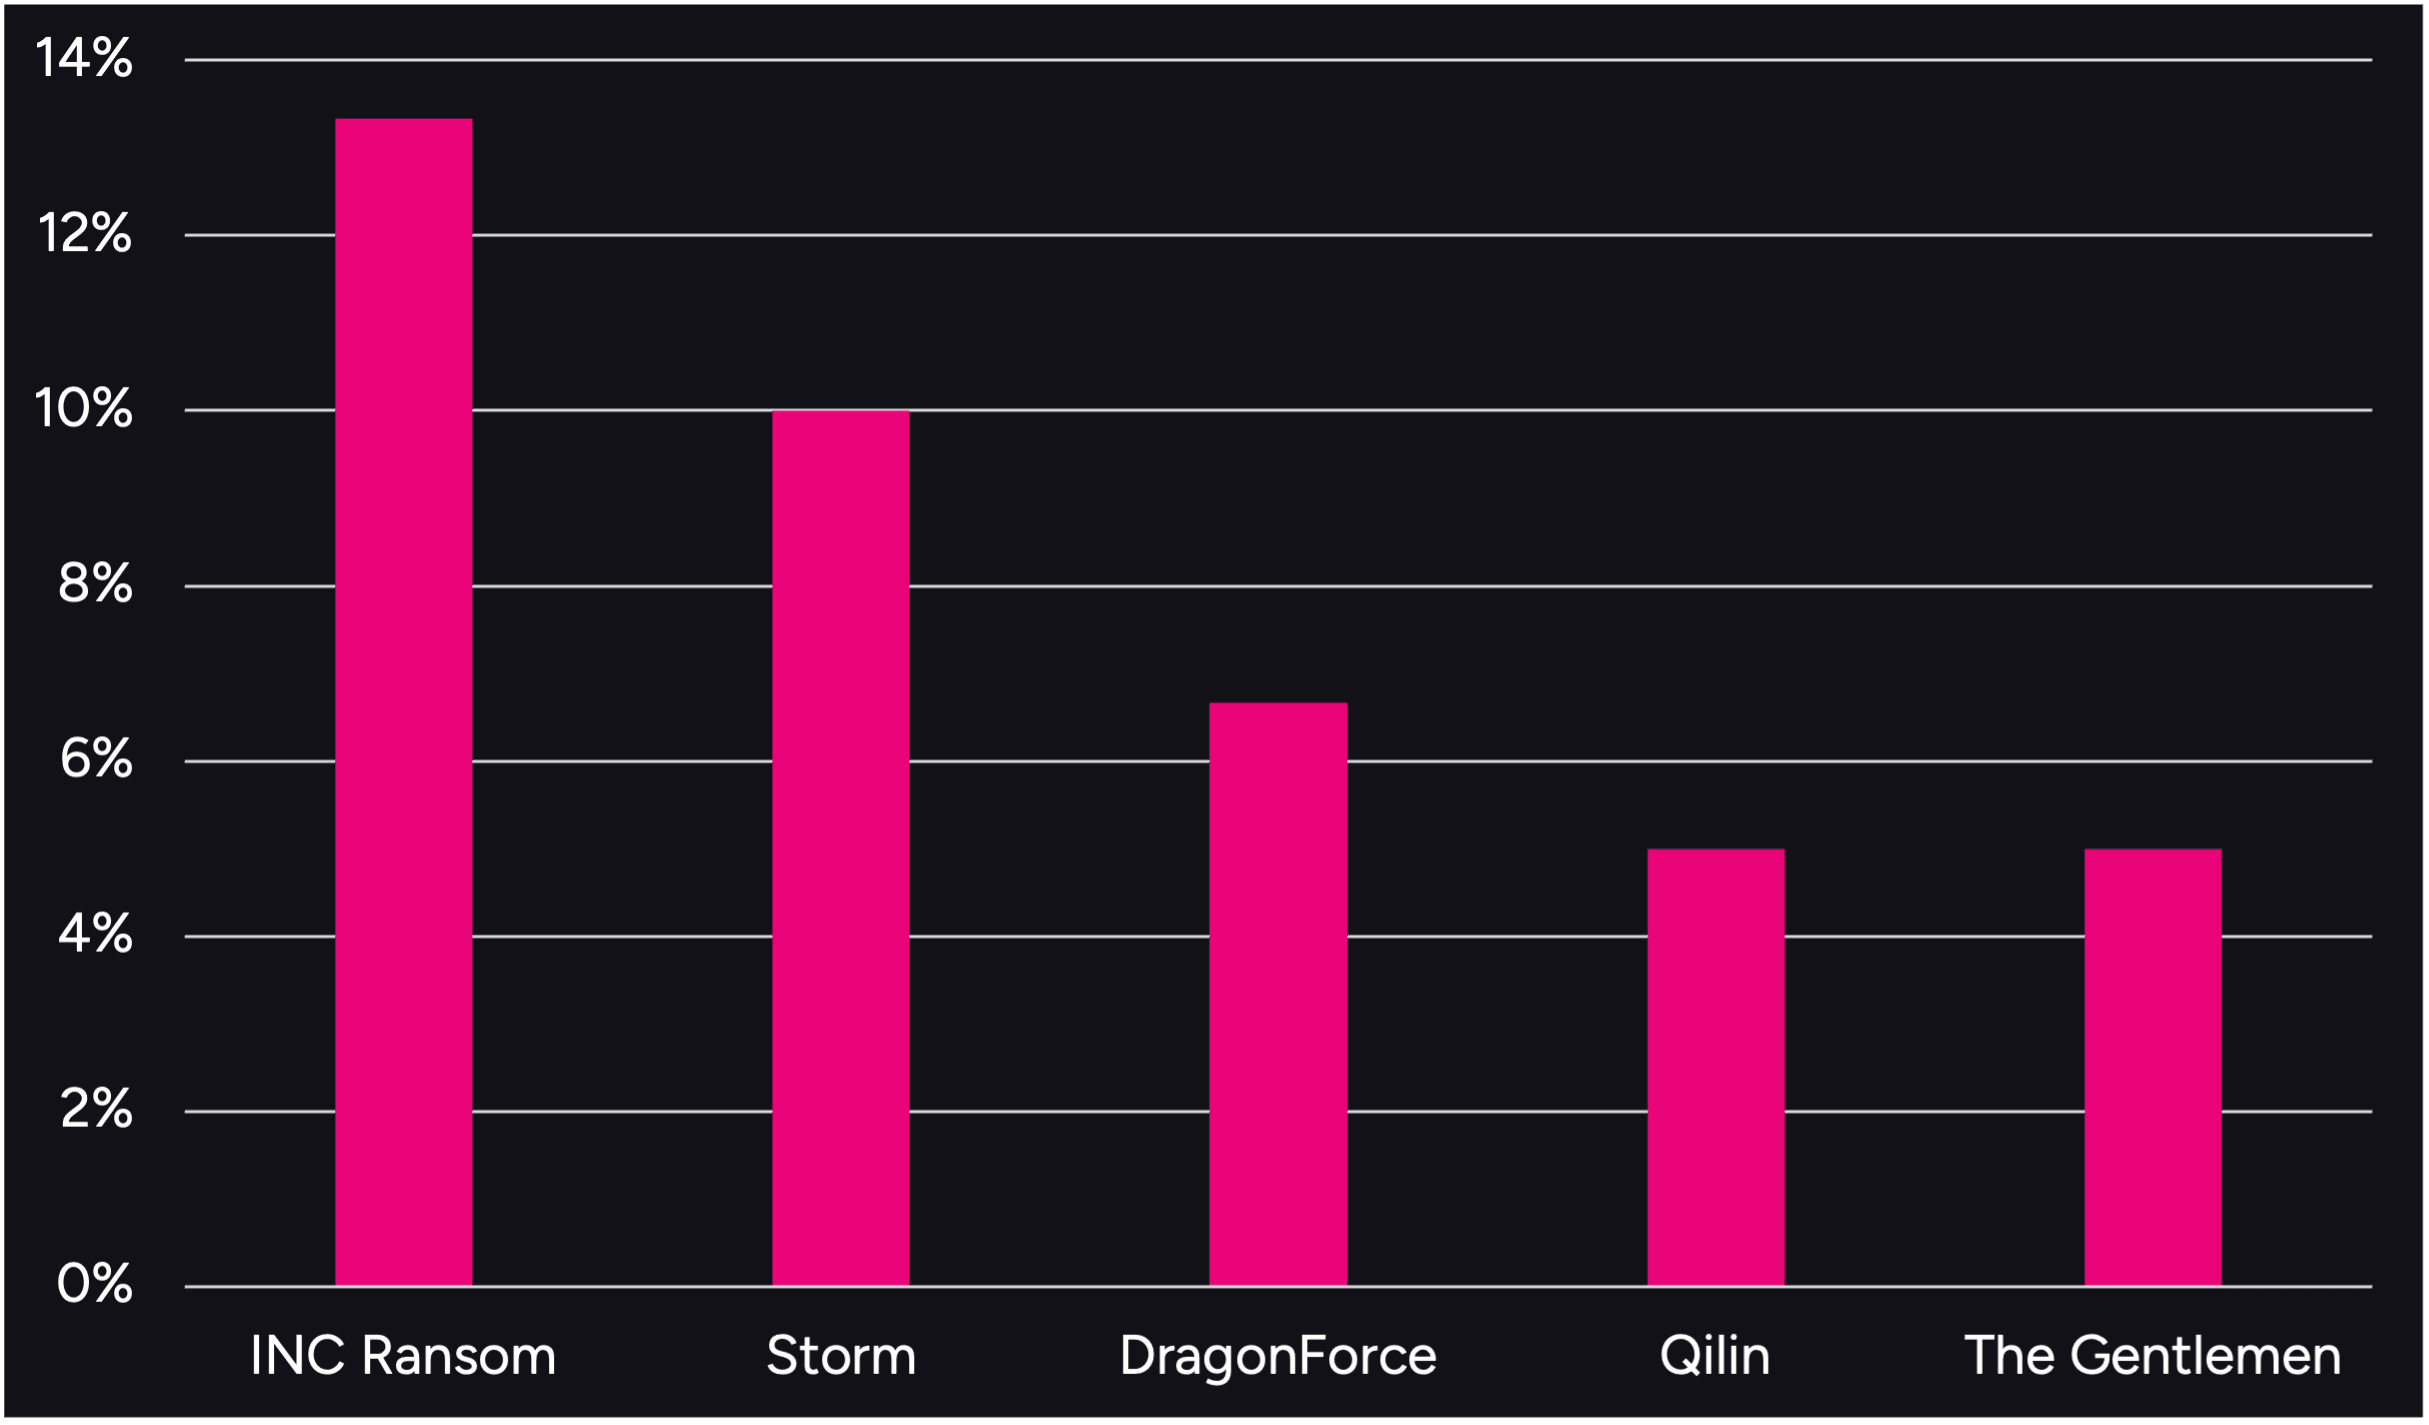
Figure 1. Activity from the top 5 threat groups in August 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
August 2026 was a significant month for the emergence of new threat actors, with Arete identifying several previously untracked ransomware groups, including Storm, Dark Project, DireWolf, Morpheus, Orova, Spirals, Wallstreet Team, and Zawoo Team. This trend underscores the ongoing evolution of the threat landscape and the low barriers to entry for new cybercriminal operations.
Arete observed a continued use of AI-enabled capabilities across the ransomware ecosystem during August. Similar to Fulcrumsec and Setra, the newly emerged Zawoo Team appears to leverage AI-assisted analysis of stolen data, publishing highly structured and detailed victim assessments on its data leak site (DLS). Additionally, both the Aurora and Storm ransomware groups have been observed utilizing AI-driven or AI-assisted chat representatives during victim communications. These developments suggest that threat actors are increasingly incorporating AI to enhance data analysis, automate victim engagement, and improve the effectiveness and scalability of extortion operations.
In August, Arete also observed that despite sustained law enforcement disruption efforts, LockBit continues to demonstrate operational resilience, likely through the expansion of its affiliate ecosystem and the evolution of its tactics. Recent activity indicates an increased reliance on data theft and exfiltration-only operations, with observed victimology suggesting a notable focus on organizations within the financial sector.
Sources
Arete Internal

Report
Arete's H1 2026 Crimeware Report
Explore intelligence and operational data from the frontlines of ransomware and extortion response as we detail the most significant trends and developments in the cyber threat landscape in the first half (H1) of 2026.