Article
Chrome Extensions Used for Credential-Stealing and ClickFix Attacks
Arete Analysis
Recent research reveals two distinct but similar malicious Chrome browser extension campaigns that demonstrate how threat actors are increasingly abusing trusted browser extension ecosystems to gain initial access, steal sessions, and compromise enterprise environments.
What’s Notable and Unique
In mid-January 2026, cybersecurity researchers uncovered a coordinated cluster of five malicious Chrome extensions masquerading as enterprise productivity or access management tools for popular Human Resource and Enterprise Resource Planning platforms such as Workday, NetSuite, and SAP SuccessFactors.
Although published under different names, the extensions shared identical infrastructure, code patterns, and attack logic, indicating a single, well-organized operation. These extensions enabled session hijacking and full account takeover by abusing browser-level access.
In January, researchers also documented a separate campaign, dubbed “CrashFix,” which uses a different but equally effective browser extension-based attack vector. In this case, a malicious Chrome extension named NexShield impersonated the legitimate uBlock Origin Lite ad blocker and was distributed through malicious ads that redirected users to the official Chrome Web Store where they would be prompted to download the malicious version.
The technique mentioned above is yet another evolution of the ClickFix style social engineering that emerged in 2025, in which users are tricked into executing malicious commands themselves. In CrashFix attacks, following the instructions led to the execution of PowerShell commands that downloaded and installed ModeloRAT, a previously undocumented Python based remote access trojan.
Analyst Comments
Browser extensions are being weaponized as highly trusted initial access vectors, with attackers blending technical abuse (cookie theft, resource exhaustion) with social engineering (productivity branding, fake repair prompts). Together, these two recent findings demonstrate that malicious Chrome extensions pose a risk as a primary entry point for enterprise compromise, making browser extension governance, monitoring, and user education a critical defensive priority. Organizations should monitor for hidden PowerShell processes that are accessing browser cache folders and limit the use of PowerShell to privileged administrators. Organizations should also continue to promote and update their security awareness training, educating employees on newer social engineering techniques such as ClickFix.
Sources
Back to Blog Posts

Article
Adversarial AI Evolves from Prompting to Autonomous Attack Workflows
Cybercriminals and state-linked threat actors are increasingly incorporating artificial intelligence (AI) into multiple stages of offensive operations. Rather than relying on AI only for content generation or research, threat actors are now consistently using it to support reconnaissance, vulnerability discovery, credential theft, malware development, social engineering, and activities following initial compromise. The growing use of automated and agent-based workflows is allowing adversaries to coordinate offensive malicious activities with less manual involvement, potentially increasing the speed, scale, and efficiency of future campaigns.
What’s Notable and Unique
In one observed campaign, threat actors used AI to plan, build, and conduct an automated credential-harvesting operation within just several hours, demonstrating how compromised infrastructure can be rapidly repurposed to support larger-scale malicious activity.
Arete has observed several threat groups using AI-assisted capabilities to facilitate the analysis of data obtained during exfiltration so far this year, including INC Ransom, FulcrumSec, and Settra.
Attackers are also attempting to reproduce proprietary AI capabilities. Large-scale automated prompting campaigns have been used to extract information about the behavior and capabilities of proprietary AI models. The use of numerous accounts and intermediary infrastructure can make these activities more difficult to identify and attribute.
Analyst Comments
AI is increasingly becoming an operational component in the threat landscape rather than simply a tool that improves attacker productivity. By connecting reconnaissance, development, credential operations, and other activities through automated workflows, threat actors can conduct campaigns more quickly and reduce reliance on continuous human input. This trend also impacts security requirements for organizations deploying AI technologies. AI models, development environments, cloud resources, identities, repositories, and automated workflows should increasingly be considered interconnected elements of the enterprise attack surface, and organizations should maintain visibility across these areas and ensure that security controls account for both conventional threats and AI-enabled attack techniques.
Sources
GTIG AI Threat Tracker: From Prompting to Autonomy – The Evolution of Adversarial AI

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.

Article
Ransomware Trends & Data Insights: August 2026
Although INC Ransom was the most active ransomware threat group observed in August 2026, overall activity remained relatively distributed across the threat landscape, with approximately 30 unique ransomware and extortion groups, including both established and newly emerged actors, observed during the month. Alongside INC Ransom, Storm, DragonForce, Qilin, and The Gentlemen were among the top five most active threat groups, underscoring the continued diversity and competitiveness of the ransomware ecosystem.
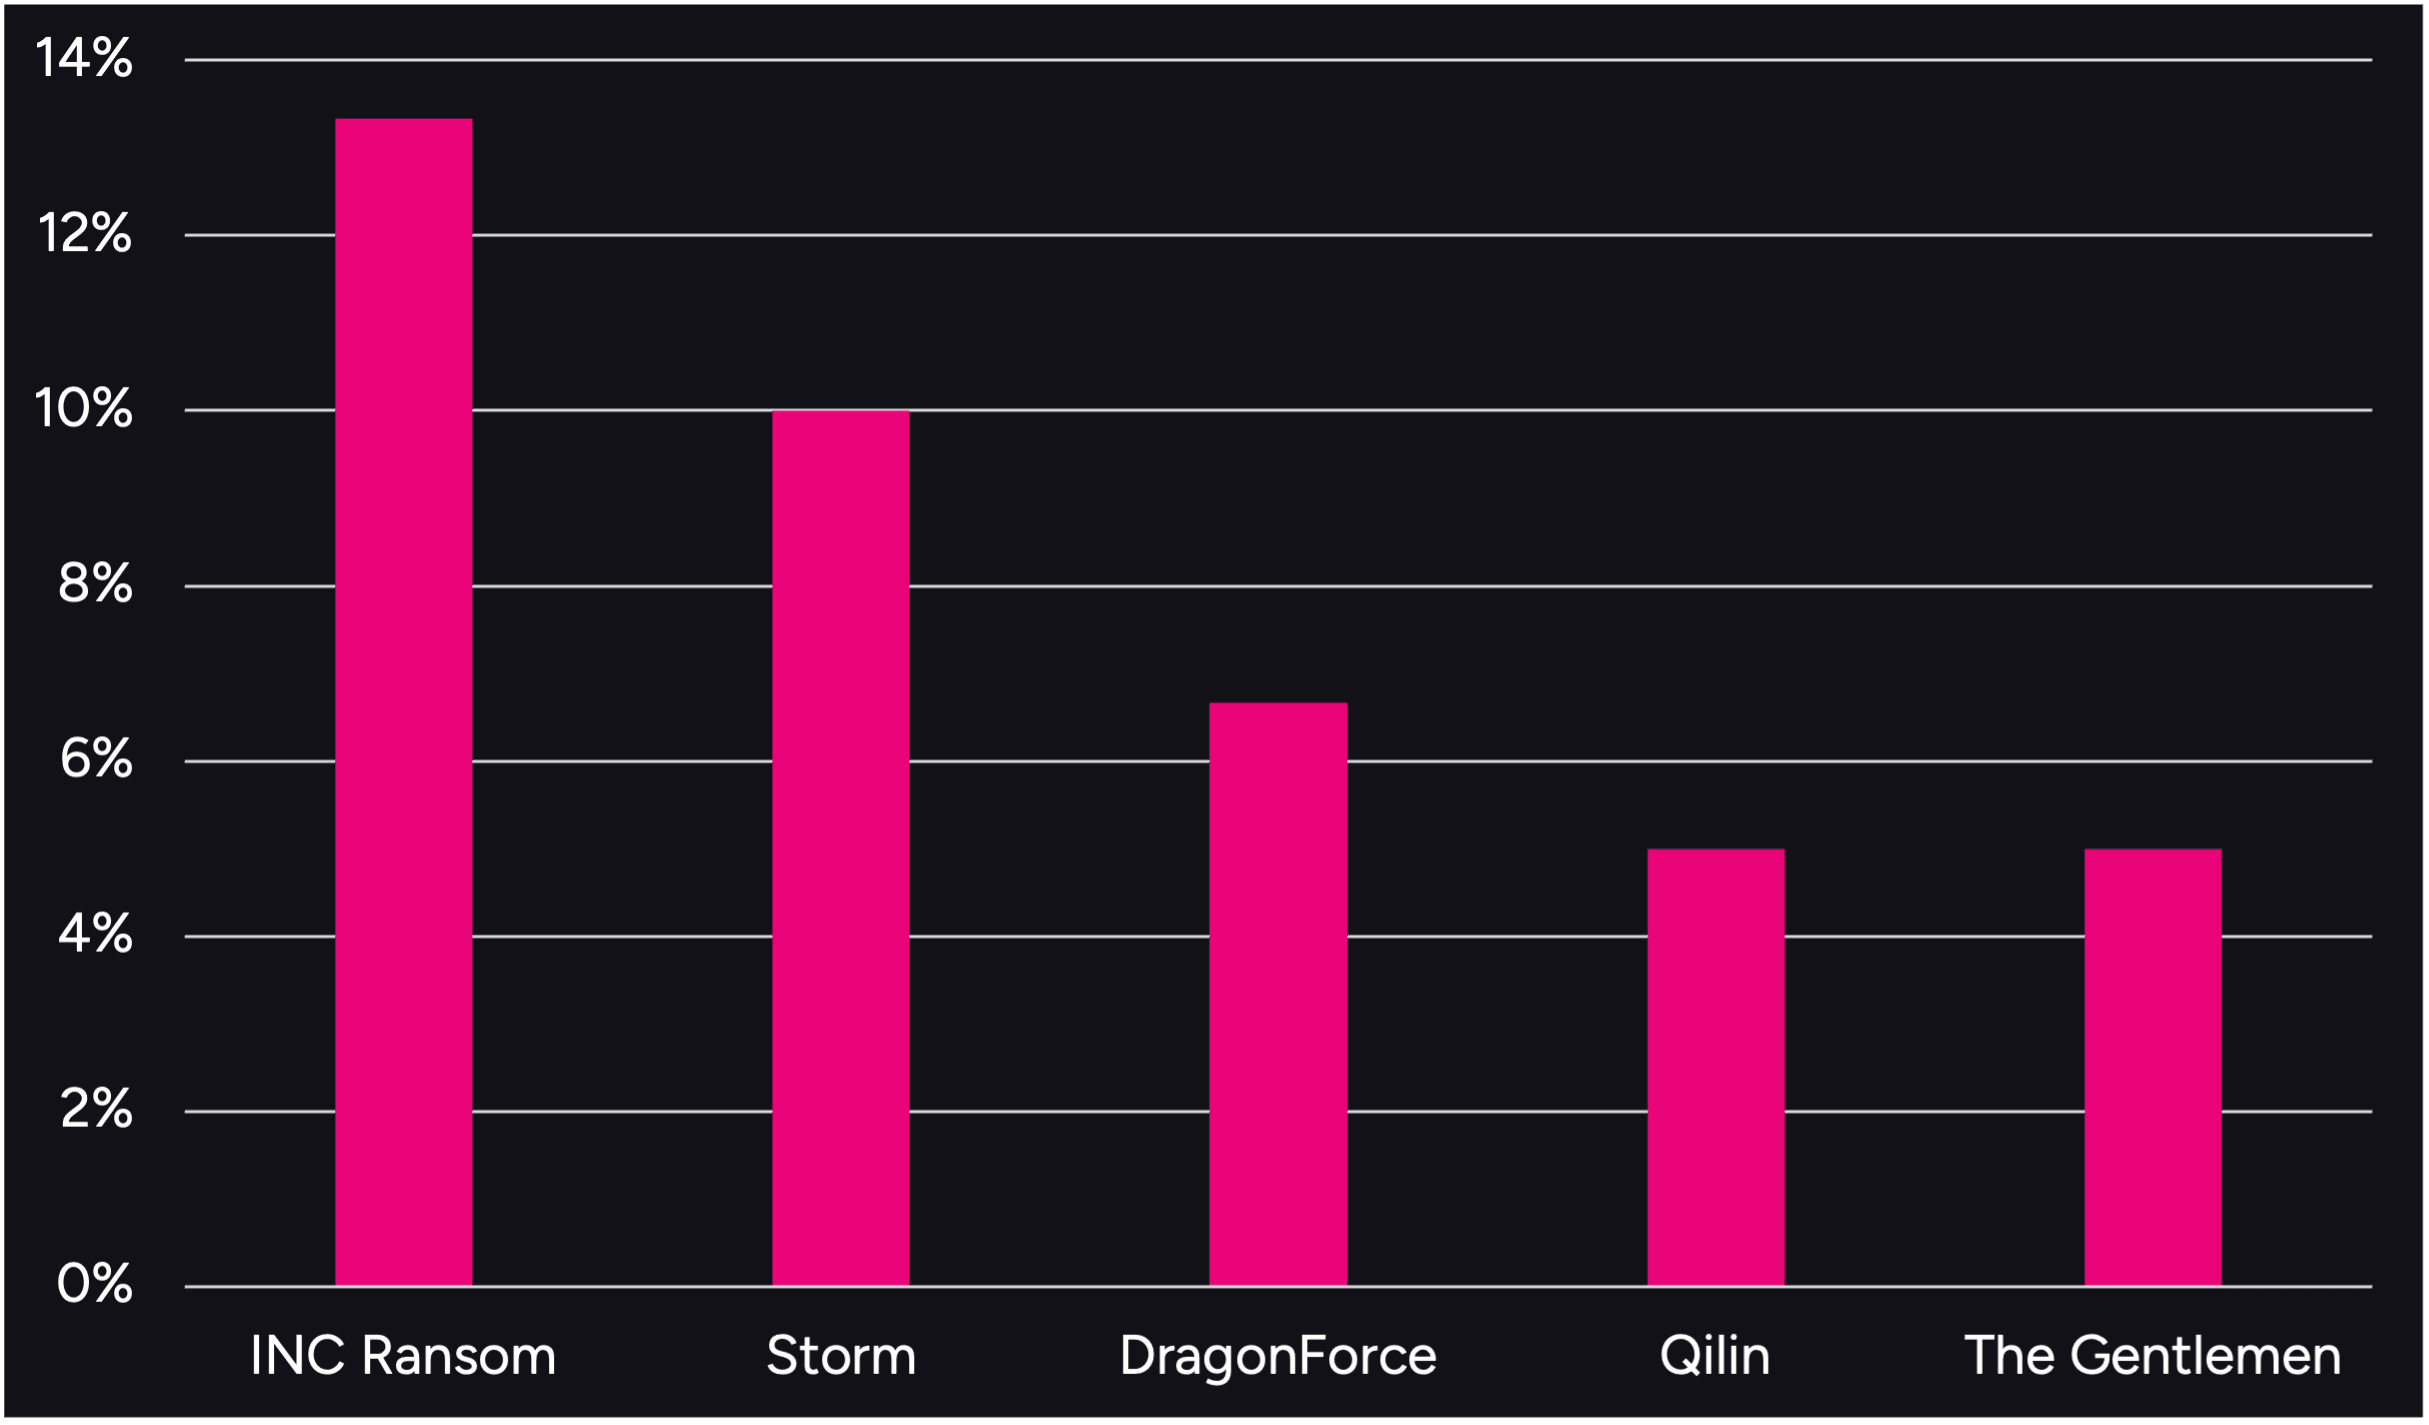
Figure 1. Activity from the top 5 threat groups in August 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
August 2026 was a significant month for the emergence of new threat actors, with Arete identifying several previously untracked ransomware groups, including Storm, Dark Project, DireWolf, Morpheus, Orova, Spirals, Wallstreet Team, and Zawoo Team. This trend underscores the ongoing evolution of the threat landscape and the low barriers to entry for new cybercriminal operations.
Arete observed a continued use of AI-enabled capabilities across the ransomware ecosystem during August. Similar to Fulcrumsec and Setra, the newly emerged Zawoo Team appears to leverage AI-assisted analysis of stolen data, publishing highly structured and detailed victim assessments on its data leak site (DLS). Additionally, both the Aurora and Storm ransomware groups have been observed utilizing AI-driven or AI-assisted chat representatives during victim communications. These developments suggest that threat actors are increasingly incorporating AI to enhance data analysis, automate victim engagement, and improve the effectiveness and scalability of extortion operations.
In August, Arete also observed that despite sustained law enforcement disruption efforts, LockBit continues to demonstrate operational resilience, likely through the expansion of its affiliate ecosystem and the evolution of its tactics. Recent activity indicates an increased reliance on data theft and exfiltration-only operations, with observed victimology suggesting a notable focus on organizations within the financial sector.
Sources
Arete Internal

Report
Arete's H1 2026 Crimeware Report
Explore intelligence and operational data from the frontlines of ransomware and extortion response as we detail the most significant trends and developments in the cyber threat landscape in the first half (H1) of 2026.