Article
PYSA: 2020 to Now
Arete Analysis
Cybersecurity Trends
Cyber Threats
PYSA is the newest variant of the Mespinoza Ransomware as a Service (RaaS) family, which was first observed infecting victims in the wild in December 2019. PYSA is likely a reference to the open-source web application auditing tool PYSA (Protect Your System Amigo) released by security engineers at Facebook.
Like Ryuk, PYSA is dubbed a “big game hunter” for their tendency to target large corporations. Based on their advanced encryption methods, double extortion tactics, and desire to distinguish themselves, this up-and-coming ransomware group is “one to watch.”
Since Q3 2020, Arete has responded to 26 total PYSA cases. With an average ransom payment of $346,603, PYSA ranks third highest in average ransom payouts tracked by Arete through July 2021. Additionally, Arete has observed a steady increase in cases sine Q3 2020 (see Figure 1).
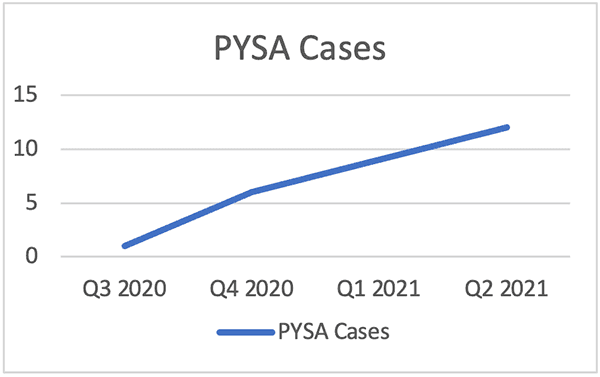
Figure 1: PYSA cases over a one-year period.
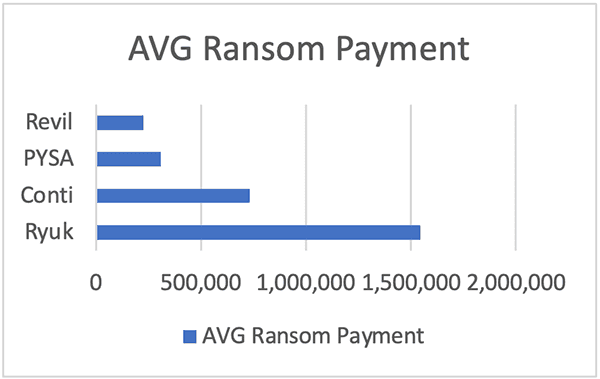
Figure 2: Arete PYSA cases average ransom payment.
Targeting Big Game
PYSA targets large companies or organizations susceptible to extortion, where business downtime would pose a significant impact to operations. By extorting companies with the threat of publishing sensitive data, PYSA increases the chances of ransom payments. The top three sectors targeted by PYSA include K-12 school systems (36%), professional services (20%), and healthcare providers (12%). See Figure 3 for all targeted sectors.
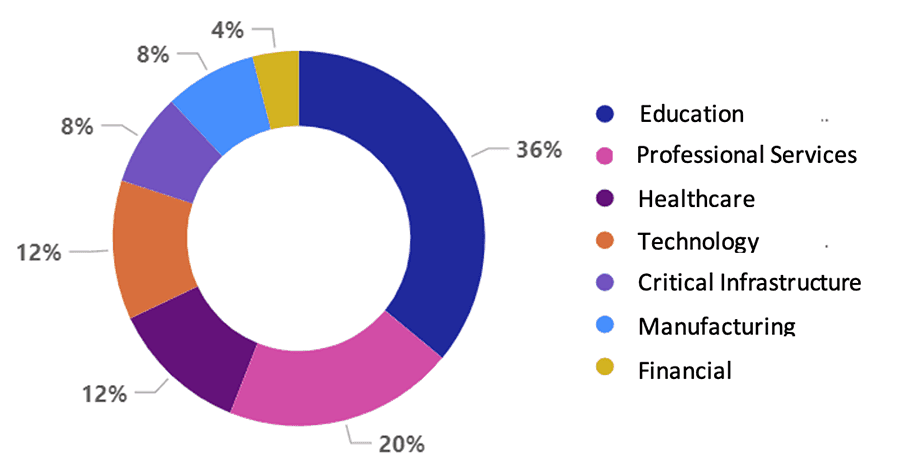
Figure 3: Arete PYSA cases, all targeted sectors.
Sophisticated Criminals
PYSA exhibits discipline by first surveying compromised systems to determine a victim’s potential “extortion value.” Open-source reporting indicates that PYSA searches not only for common keywords (e.g., PII, balance, routing), but also for keywords (e.g., illegal, fraud, criminal) that could be evidence of illegal activities by the victim.
Arete also identified some other key PYSA activity — specifically, that PYSA occasionally publishes data on leak sites after payment, provides decryptors that partially corrupt data, and stops communication for multiple days during negotiations.

Figure 4: Average time of business interruption.
Infection vector and persistence: Human-operated ransomware
Arete identified the following PYSA tactics, techniques, and procedures (TTPs) as being consistent with manually operated ransomware during the initial access phase:
Uses brute force remote desktop protocol (RDP) attacks against central management consoles, domain controllers, and Active Directory accounts.
Exfiltrates password databases prior to exploitation.
Leverages Mimikatz in victim environments, likely to gain access to credentials.
Additionally, Arete observed the following persistence toolset as part of PYSA campaigns:
Gasket. A backdoor written in the Go programming language, Gasket is designed as a backup to RDP to maintain access to the network. Gasket has many capabilities (e.g., “MagicSocks”) that allow PYSA to tunnel traffic to an externally controlled server.
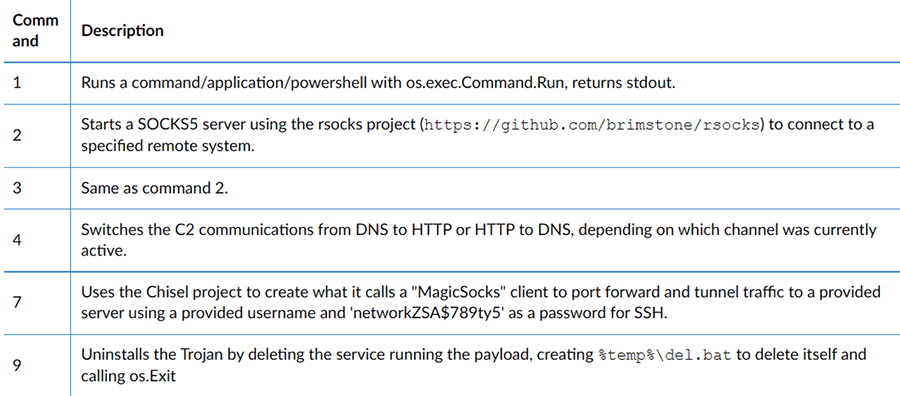
Figure 5: Gasket functionality.
MagicSocks. Leverages code from the Chisel project to tunnel traffic from the local system to an external, actor-controlled server. Next, uses Chisel code to tunnel traffic out of the local system to a landing page (“creatordampfe[.]xyz”) before routing the traffic to an unknown actor-controlled server.
Advanced encryption techniques
According to open-source data, PYSA uses Crypto++ to encrypt victim files with both RSA-4096 and AES-256-CFB. The group appends the encrypted files with the “.pysa” extension and leverages an allowlist and denylist to determine which files to encrypt.
The denylist contains all files to be encrypted.
The allowlist includes vital directories, such as Windows and Boot, which, if encrypted, would make recovery via the decryptor impossible. After, PYSA drops the ransom note (Figure 6) in every directory listed in the denylist.
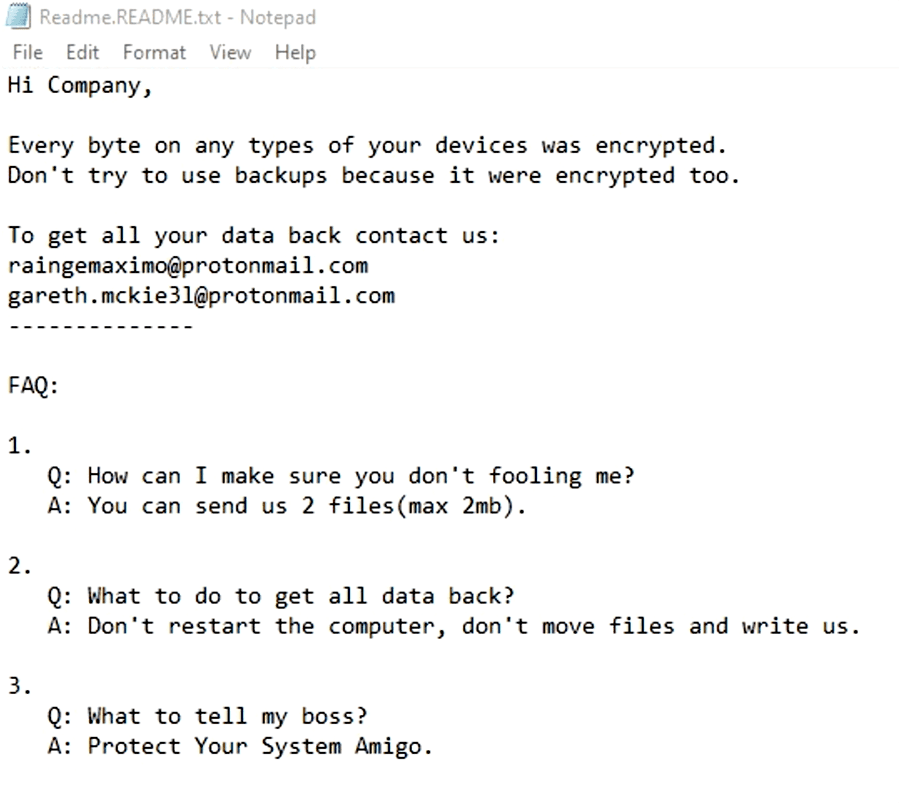
Figure 6: PYSA ransom note.
PYSA threat likely to remain steady
PYSA utilized the rapid shift of corporations to remote work during COVID-19 for opportunistic targeting against RDP and remote admin infrastructure. Arete asserts that the threat posed by PYSA campaigns will likely remain steady, with PYSA targeting larger corporations across sectors to demand higher ransom payments. PYSA’s discipline, target selection, and advanced encryption techniques make them a credible threat on the ransomware scene.
How Arete can help you “Protect Your Systems Amigo”
Arete has a complete suite of managed security services, including managed detection and response (MDR), SentinelOne Endpoint Detection and Response (EDR) software deployment, and Arsinal threat hunting services for defending against ransomware attacks.
The following rulesets would detect PYSA activity on a client endpoint:
PowerShell used to disable Windows Defender Protection.
Lsass dump.
Firewall Exception for Remote Desktop.
MS Windows Defender stopped.
Security Tool Services stopped.
Volume Shadow Copy deletion.
Process Masquerading in Registry – Svchost.
Advanced Port Scanner Tool download.
Advanced Port Scanner Process Masquerading.
Advanced Port Scanner Process.
Advanced Port Scanner File detected.
Mimikatz Process Execution.
Advanced IP Scanner Network Mapping Tool download.
Advanced IP Scanner Network Mapping Tool Process.
Advanced IP Scanner Network Mapping File detected.
Advanced IP Scanner Process Masquerading.
Indicators
Ransom Note Emails
johnfitzgerald@onionmail.org
cristianpalmerss@protonmail.com
wcraijones@protonmail.com
dec_restore1@outlook.com
zljanczplaizr@onionmail.org
EfreTavernia@protonmail.com
lizawilkinson@onionmail.org
Makailahuff@protonmail.com
Davionfinley@protonmail.com
joedansereau@onionmail.org
m0arc7bdhsohar@onionmail.org
david_ansty@protonmail.com
t.trstram@protonmail.com
Resources
https://unit42.paloaltonetworks.com/gasket-and-magicsocks-tools-install-mespinoza-ransomware/
https://blog.emsisoft.com/en/38840/ransomware-profile-mespinoza-pysa/
https://www.databreaches.net/k-12-school-districts-fall-prey-to-pysa-ransomware/
https://www.cert.ssi.gouv.fr/uploads/CERTFR-2020-CTI-003.pdf
https://www.documentcloud.org/documents/20514564-pysa-ransomware-bc
Back to Blog Posts

Article
Ransomware Trends & Data Insights: October 2026
Although Akira once again emerged as the most active ransomware group in October, overall ransomware and extortion activity was not dominated by any single threat group and instead remained widely distributed among a variety of threat actors, continuing the trend that began around August. Arete identified 31 unique named threat groups in October, the most observed in a single month so far in 2026. In addition to Akira, Settra, and The Gentlemen were among the three most active groups. Several new threat actors also emerged, including BYOD, Kubera Team, QWCrypt, AoQin, Emperador, Osiris Team, and Cinder, with Cinder assessed as possibly part of a threat actor cluster affiliated with the former BlackFile group.

Figure 1. Activity from the top 10 threat groups in October 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
PHP2Shell emerged as one of the most significant threats in October, with increasing exploitation of the critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. Other notable vulnerabilities included CVE-2026-104286 affecting FortiMail, and CVE-2026-102255, a critical pre-authentication Server-Side Request Forgery (SSRF) vulnerability affecting SonicWall SMA1000 appliances, highlighting continued threat actor interest in internet-facing enterprise infrastructure.
International law enforcement operations against cybercriminal groups continued to make headlines in October. German authorities announced the arrest of 28-year-old Russian national Vladimir K., suspected of being a senior operator within the Qilin Ransomware-as-a-Service (RaaS) group. Separately, the FBI arrested an individual with suspected links to ShinyHunters, adding to recent law enforcement activity targeting ransomware and extortion groups, including the disruption of KillSec. While Vladimir K.’s arrest has not yet had a notable impact on Qilin’s operational activity, it could provide law enforcement with greater insight into the group’s infrastructure and affiliate network, potentially supporting further disruption efforts.
In early October, “The Luna Moth Files” exposed several files containing alleged internal communications associated with Luna Moth, also known as Silent Ransom Group, revealing insights into the group’s social engineering, data extortion, and victim negotiation operations. However, several claims remain unverified, and the exposure has not notably disrupted the group’s activity thus far, as it was among the top threat actors Arete observed throughout the month.
Sources
Arete Internal

Article
PHP2Shell Exploitation Update
PHP2Shell exploitation activity continues to increase globally, with threat actors targeting the critical PHP remote code execution (RCE) vulnerabilities CVE-2026-109618 and CVE-2026-109619. Researchers recently identified low-volume scanning targeting unpatched or partially mitigated hosts across multiple countries and sectors, and the activity is assessed with moderate confidence as linked to a Korean-speaking operator associated with the Lazarus Group ecosystem. While PHP2Shell (CVE-2026-109618 and CVE-2026-109619) has been patched in PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35, the separately identified CVE-2026-115560 remains unpatched.
What’s Notable and Unique
PHP2Shell vulnerabilities can cause memory corruption due to improper error handling, potentially allowing threat actors to achieve remote code execution on vulnerable PHP servers.
Observed activity includes mass scanning, PHP environment fingerprinting, exploitation attempts, credential and secret theft attempts, and attempts to deliver second-stage payloads and malware.
Successful in-the-wild exploitation has also been reported against honeypots, resulting in shell command execution and the retrieval of additional payloads, demonstrating the potential for follow-on malicious activity.
Mitigations
Organizations should prioritize upgrading internet-facing PHP deployments to patched versions, migrating unsupported PHP versions, updating embedded and containerized PHP runtimes, and implementing available Web Application Firewall (WAF) protections as a temporary defense-in-depth measure.
Analyst Comments
PHP2Shell poses a significant security concern due to its potential to enable unauthenticated remote code execution on vulnerable PHP servers. The progression from mass scanning and exploitation attempts to reports of successful command execution demonstrates the potential for these vulnerabilities to support initial access and subsequent malicious activity. Arete has been closely monitoring PHP2Shell exploitation activity and regularly reviewing and updating related indicators to support detection and blocking efforts. Given the potential for remote exploitation and follow-on activity, PHP2Shell represents a high-priority initial-access risk, emphasizing the importance of timely patching and remediation of affected PHP environments.
Sources
PHP shares mitigation for new RCE vulnerability with no patch
PHP2Shell Exploitation Attempts Continue Amid Suspected N. Korea Global Scanning Activity
PHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai Malware
Advisory: PHP2Shell Vulnerabilities (CVE-2026-109618, CVE-2026-109619)

Article
LiteLLM Supply-Chain Compromise
A software supply-chain attack compromised the release pipeline of LiteLLM, a widely used open-source Python SDK and AI gateway. Attackers leveraged the compromised pipeline on October 21st to publish a malicious LiteLLM version through PyPI and associated Docker registries. The affected release, LiteLLM 1.107.0, contained malware designed to steal credentials, sensitive configuration data, private keys, browser information, and other secrets from compromised systems.
What’s Notable and Unique
The incident is particularly significant because LiteLLM provides a common API for applications to interact with AI models from multiple providers. It is reported that the project had approximately 61,800 GitHub stars and 92 million monthly PyPI downloads.
Rather than modifying the core LiteLLM application source code, the threat actors reportedly tampered with the installation package itself. The malware was designed for broad credential and information theft and encrypted the collected data before uploading it to the attacker's endpoint.
The compromise went beyond one-time credential theft. A malicious Python component launched a detached loader that checked a GitHub-hosted pointer every hour and could download Python code from an external server for execution on the compromised machine. This provided threat actors with a mechanism for subsequent remote code execution.
Analyst Comments
Although the malicious packages were subsequently removed, simply uninstalling or deleting the affected LiteLLM package may not be sufficient, because malicious Python startup files or the detached loader could remain on the host. All exposed information should be rotated immediately, and infected systems should be isolated and rebuilt from clean backups. The most recent clean release prior to the attack, LiteLLM 1.106.2, is currently the suggested recovery version.
Sources
LiteLLM release pipeline hacked to distribute info-stealer malware
LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials
The Collector Reaches Beyond Provider API Keys

Article
French Supermarket Cyberattack Highlights Risks in Exposed Refrigeration Controllers
Hundreds of French supermarkets were reportedly affected by a cyberattack in which threat actors compromised internet-connected refrigeration controllers and manipulated temperature and defrost settings, which caused refrigeration units to overheat, resulting in widespread food spoilage and significant financial loss. Impacted refrigeration systems were associated with Danfoss, Copeland, and Dixell, and demonstrated how vulnerabilities in industrial control systems (ICS) can disrupt physical operations without relying on conventional data theft or encryption. The attack also raised concerns about the wider exposure of similar devices, as thousands of refrigeration management interfaces remain accessible from the public internet. The incident highlights the growing risk posed by insecure operational technology (OT), particularly where legacy equipment and remote-management interfaces lack adequate security controls.
What’s Notable and Unique
Researchers identified approximately 2,765 internet-accessible Danfoss AK-SM 800A interfaces during assessment. This figure reflects the scope of that research and should not be interpreted as a current count of exposed devices. Publicly accessible management interfaces increase the opportunity for unauthorized access to industrial equipment.
Research also identified several security flaws in the Danfoss AK-SM 800A platform, including an authentication bypass command injection that could enable remote code execution and a weakness involving web-server configuration changes. Danfoss addressed these findings through firmware updates.
Authorities reported compromised Danfoss AK-SM and AK-SC systems, alongside Copeland XWEB and Dixell XWEB monitoring platforms.
Analyst Comments
The incident demonstrates the business consequences of insufficiently secured industrial infrastructure and reinforces the need to integrate OT security into enterprise risk management. Organizations operating connected facility systems should establish clear ownership of industrial assets, enforce secure remote-access policies, and prioritize remediation based on exposure and operational criticality. The findings also highlight the importance of coordinating security teams with facilities and engineering personnel to ensure that protective measures do not compromise essential operations. A risk-based approach to OT security can help organizations reduce exposure while maintaining the availability and reliability of critical equipment.
Sources
France Supermarket Hacks Expose Risks of Internet-Facing Refrigeration Systems
Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers