Article
Ransomware Trends & Data Insights: January 2026
Arete Analysis
Although Akira was once again the most active ransomware group in January, the threat landscape was more evenly distributed than it was throughout most of 2025. In December 2025, the three most active threat groups accounted for 57% of all ransomware and extortion activity; in January, the top three accounted for just 34%. Akira’s dominance also decreased to levels more consistent with early 2025, as the group was responsible for almost a third of all attacks in December but just 17% in January.
The number of unique ransomware and extortion groups observed in January increased slightly, to 17, up from 14 in December. It is too early to assess whether this trend will be the new normal for 2026. It is also worth noting that overall activity in January was lower than in previous months, consistent with what Arete typically observes at the beginning of a new year.
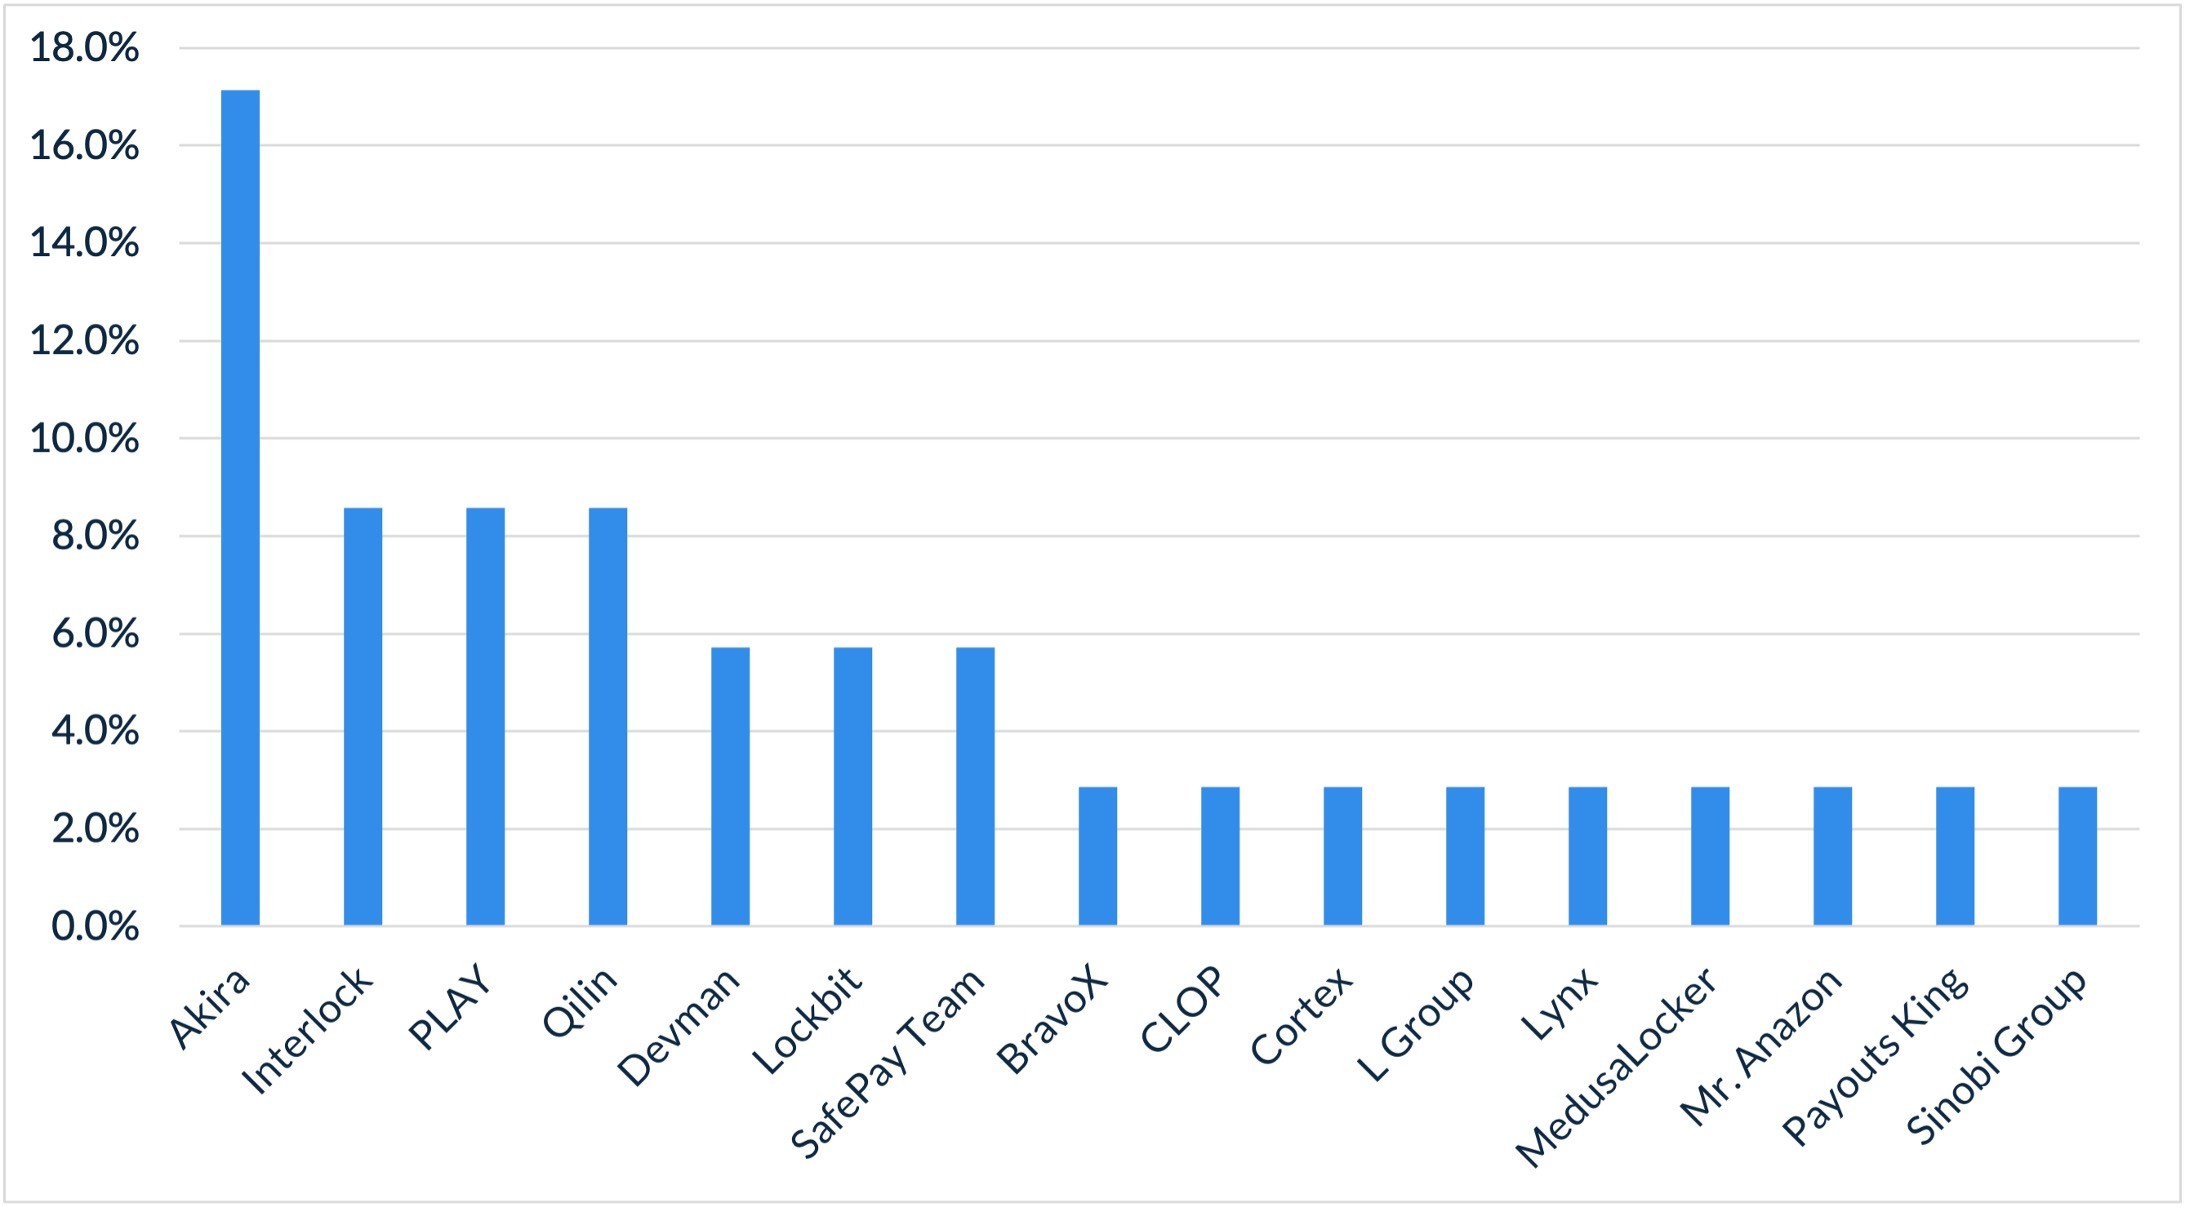
Figure 1. Activity from all threat groups in January 2026
Throughout the month of January, analysts at Arete identified several distinct trends behind the threat actors perpetrating cybercrime activities:
In January, Arete observed the reemergence of the LockBit Ransomware-as-a-Service (RaaS) group, which deployed an updated “LockBit 5.0” variant of its ransomware. LockBit first announced the 5.0 version on the RAMP dark web forum in early September 2025, coinciding with the group’s six-year anniversary. The latest LockBit 5.0 variant has both Windows and Linux versions, with notable improvements, including anti-analysis features and unique 16-character extensions added to each encrypted file. However, it remains to be seen whether LockBit will return to consistent activity levels in 2026.
The ClickFix social engineering technique, which leverages fake error dialog boxes to deceive users into manually executing malicious PowerShell commands, continued to evolve in unique ways in January. One campaign reported in January involved fake Blue Screen of Death (BSOD) messages manipulating users into pasting attacker-controlled code. During the month, researchers also documented a separate campaign, dubbed “CrashFix,” that uses a malicious Chrome browser extension-based attack vector. It crashes the web browser, displays a message stating the browser had "stopped abnormally," and then prompts the victim to click a button that executes malicious commands.
Also in January, Fortinet confirmed that a new critical authentication vulnerability affecting its FortiGate devices is being actively exploited. The vulnerability, tracked as CVE-2026-24858, allows attackers with a FortiCloud account to log in to devices registered to other account owners due to an authentication bypass flaw in devices using FortiCloud single sign-on (SSO). This recent activity follows the exploitation of two other Fortinet SSO authentication flaws, CVE-2025-59718 and CVE-2025-59719, which were disclosed in December 2025.
Source
Back to Blog Posts

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory

Article
Ransomware Trends & Data Insights: September 2026
The Akira ransomware group re-emerged as the most active ransomware threat observed by Arete in September. Overall activity remained relatively distributed among multiple threat groups, with 29 unique groups observed throughout the month. Alongside Akira, INC Ransom and the relatively new Storm group were among the three most active threat actors observed in September. Several new threat groups also emerged during the month, including Hades Team, Shiba, and Vortex (which is suspected to be part of the cluster of threat actors affiliated with the former BlackFile group).

Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
In September 2026, the ShinyHunters threat group escalated its extortion activity by publicly targeting both the Clop ransomware group and the FBI. The group claimed to have breached and defaced Clop’s infrastructure, demanding an eight-figure ransom, while separately alleging the theft of sensitive FBI-related data and demanding the retraction of statements made in a prior public advisory. In both incidents, ShinyHunters employed similar pressure tactics, including website defacements, repeated public postings, and threats of data disclosure.
ClickFix attacks remained prevalent in September 2026, with ransomware groups including Qilin, Helix, and The Gentlemen leveraging ClickFix lures to facilitate PowerShell-based payload execution and initial access. The technique continues to evolve, combining social engineering with legitimate tools and services to enable compromise and evade detection.
September 2026 saw continued activity from the former BlackFile extortion ecosystem. BlackFile, a data theft and extortion operation active since at least October 2025, rebranded as Redact in May 2026, and since appears to have broken off into several affiliated brands, including Pink, Helix, Falcon, Cinder, and potentially Vortex. During September, some affiliates publicly disputed these associations and claimed to operate independently. However, the coordinated timing, messaging, and near-identical nature of these statements support the assessment that these groups remain part of a broader interconnected ecosystem operating under shared objectives or coordination.

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM

Article
AI Agents Used in Campaign Against PaperCut
In late August, a threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG and MF servers. PaperCut is print management software, and researchers determined that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries. The AI agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078 both security flaws affecting PaperCut software and flagged as actively exploited earlier this month. It is currently unclear if the threat actor is solely focused on access development to be handed off to other affiliated actors, or if they will directly leverage their access to achieve follow-on objectives such as data theft or ransomware deployment.
What’s Notable and Unique
Researchers observed three attack paths following the exploitation of vulnerable PaperCut servers. Threat actors would harvest credentials from LSASS memory and registry secrets to perform pass-the-hash attacks, leverage older unpatched Windows vulnerabilities (CVE-2021-42278 and CVE-2021-42287) to escalate privileges in unpatched environments, or, in some cases, directly add newly created accounts to the Domain Admins group when PaperCut was running with domain-level privileges.
Upon achieving remote code execution and credential harvesting within a self-hosted lab environment, the threat actor deployed hundreds of AI-powered agents that leveraged OpenAI Codex, DeepSeek models, and publicly available offensive security tools, including Mimikatz, SharpHound, Certipy, Rubeus, and Impacket, to automate reconnaissance, exploitation, and post-compromise activities. The attackers subsequently used a DCSync attack to obtain a database dump containing domain credentials.
Analyst Comments
The observed activity demonstrates how threat actors are increasingly leveraging AI and large language models (LLMs) to accelerate cyber operations at unprecedented speed and scale. In this campaign, the adversary progressed from exploit development to remote code execution within hours and, in some cases, achieved Domain Administrator privileges in as little as five minutes. The AI-assisted workflow enabled rapid reconnaissance, exploitation, credential theft, privilege escalation, and lateral movement, allowing the compromise of multiple organizations within seconds. This activity highlights the growing threat posed by AI-enabled adversaries capable of conducting large-scale intrusions with greater efficiency and operational velocity. Organizations affected by the PaperCut vulnerabilities are strongly advised to apply the latest security updates and implement the vendor's recommended mitigation measures to reduce the risk of compromise and unauthorized access.
Sources
Agents Gone Wild: An AI-Orchestrated Global Campaign Against PaperCut NG/MF
AI-powered attack exploited PaperCut flaws to hack 395 organizations
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances