Report
Threat Actor Spotlight: BlackSuit Ransomware
Arete Analysis
Tips
Download The Report
Executive Summary
Since May 2023, Arete’s Incident Response (IR) team has responded to multiple BlackSuit ransomware engagements against organizations in the healthcare, financial services, manufacturing, professional services, public service, entertainment, and retail sectors. This spotlight explores the ransomware behavior observed, statistics from IR engagements, and background information on the threat actor. Finally, we discuss security recommendations to better defend against this evolving cyber threat and mitigate the risk of financial and reputational losses arising from these incidents.
Incident Response Data on BlackSuit Ransomware
The information below is based on BlackSuit incidents investigated by Arete since May 2023. Our IR and teams work together to analyze key data points during every ransomware engagement and form real-time threat actor (TA) insights.
Arete has investigated dozens of engagements involving BlackSuit.
We have been extremely successful in negotiating discounted ransoms with this TA.
The highest observed ransom demand is around $18 million.
The average initial demand is around $2.5 million.
The average ransom payment facilitated is around $500,000.
Commonly observed methods of intrusions include remote desktop protocol (RDP), virtual private network (VPN), and firewall vulnerabilities.
Tools observed during the investigations include CobaltStrike, WinRAR, PUTTY, Rclone, Advanced IP Scanner, Network Scanner, Mimikatz, and GMER.
A commonly observed ransom note filename is readme.blacksuit.txt.
In some instances, backups were encrypted or deleted, while in others, backups were used for restoration.
Background
The information about the BlackSuit threat actor group in this section was shared in Arete’s 2024 Q1 Crimeware Report.
The most notable newcomer in Q1 was BlackSuit, the third most active group of Q1. Although Arete first observed BlackSuit ransomware operating in May 2023, it only accounted for less than a half percent of the total engagements in 2023. The group significantly increased its activity in Q1 2024, and there were more BlackSuit engagements in February 2024 alone than in all of 2023. BlackSuit operates as a private group without affiliates, targeting both Windows and Linux users and utilizing a double extortion method of stealing and encrypting sensitive data on a victim’s network.
BlackSuit: A Continuation of Royal Ransomware?
The BlackSuit ransomware payload has significant code overlap with Royal ransomware, and the Cybersecurity and Infrastructure Security Agency (CISA) and the FBI believe BlackSuit to likely be a rebranding or spinoff variant of Royal. While BlackSuit could be using the same developer or code with slight modifications, Arete also observed language used by BlackSuit in ransom negotiations identical to previous engagements with Royal, which lends to the assessment that the group might be a rebrand or offshoot. Regardless, BlackSuit’s emergence demonstrates that although names may change, threat actors will find ways to adapt and evolve their operations.
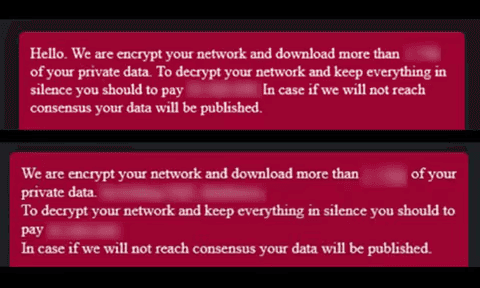
Figure 1. Language from two separate BlackSuit TOR chats (Source: Arete)
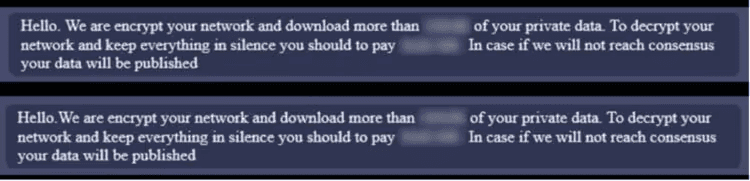
Figure 2. Identical language from two separate Royal TOR chats (Source: Arete)
Technical Analysis
Malware analysis revealed that BlackSuit ransomware:
Supports multiple command-line arguments.
Encrypts files on the system and mounted shares.
Adds the following extension to encrypted files: .blacksuit (e.g., file.docx.blacksuit).
Creates a ransom note with the following filename: readme.blacksuit.txt.
Self-identifies the group as BlackSuit in the ransom note.
References a data leak site in the ransom note that, when accessed, self-identifies the group as BlackSuit.
Kills a list of processes and services.
Maintains a list of whitelisted files and directories to make sure it will not render the system unusable, preventing recovery when running a decryptor.
Attempts to prevent system recovery by deleting the system’s volume shadow copies.
Creates the following mutex during execution: WLm87eV1oNRx6P3E4Cy9.
Execution Pattern/Arguments
BlackSuit ransomware needs command line arguments to execute and encrypt files in the system. Command line arguments supported:
Command line argument | Description |
|---|---|
-id [32-byte characters] | Ransomware ID |
-size | Invoked with drag and drop |
-ep | Number that represents the percentage of the file that will be encrypted |
-path [target_directory_path] | Used to specify a target directory to encrypt |
-localonly | Encrypt only the local system |
-networkonly | Encrypt only shared volumes/directory |
-aavm | Encrypt all files |
The ransomware will not execute in the system without the “–id” argument followed by a 32-character value that is unique in each engagement and present in the ransom note TOR URL. Portion of the data in the ransom note that contains the ID:
All your files will be decrypted, your data will be reset, your systems will stay in safe. Contact us through TOR browser using the link: http://c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion/?id=[32-characters] | ||
|---|---|---|
Execution of ransomware to encrypt files:
blacksuit.exe -id [32-characters] | ||
|---|---|---|
The ransomware developer coded the logic to allow configuration of the 32-character value in the command line during execution. This same victim-specific 32-character string value is then added to the ransom note URL used for negotiations. Due to this implementation in the ransomware code, threat researchers can execute the ransomware without knowing the 32-character string value, as any value of this type can be used to execute the malicious code. In analyzing Royal ransomware samples, Arete found a similarity in that any 32-character value can be supplied to execute the ransomware, and the value is also added to the ransom note TOR chat URL.
Example of how the ransom note content looks with a randomly supplied string (e.g., blacksuit.exe -id 7777777777777777777777777777777):
All your files will be decrypted, your data will be reset, your systems will stay in safe. Contact us through TOR browser using the link: http://c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion/?id=77777777777777777777777777777777777777 | ||
|---|---|---|
Obfuscated Files or Information: Software Packing
Most of the strings in the ransomware are encoded. The encoded strings are hardcoded and decoded at runtime. Every encoded string has its own decoding loop:
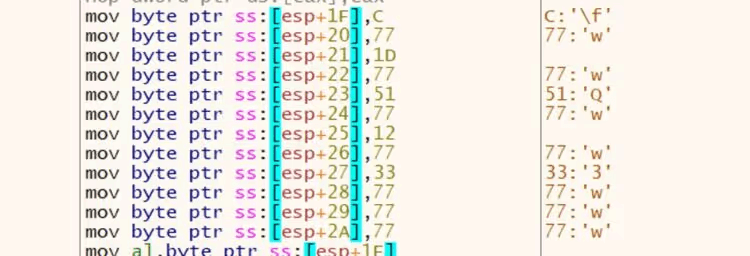
Figure 3. Encoded strings hardcoded
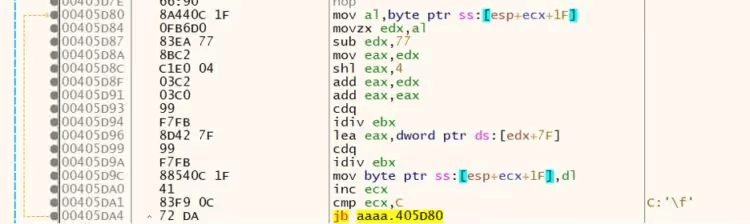
Figure 4. String decoding loop
Some relevant strings decoded in memory:
Global\\\WLm87eV1oNRx6P3E4Cy9 | -ep |
Obfuscated Files or Information: Dynamic API Resolution
To avoid static or other defensive analysis, the ransomware uses dynamic API resolution to conceal malware characteristics and functionality. The ransomware initially decrypts DLL names, then loads the APIs. Hardcoded encoded DLL names are shown below:
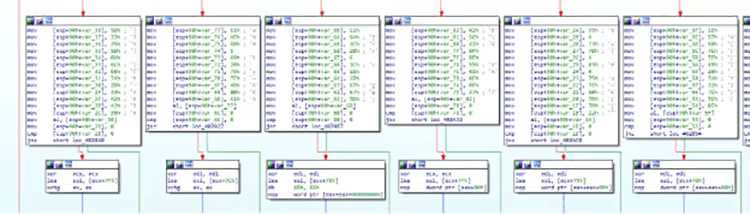
Figure 5. Encoded DLL names
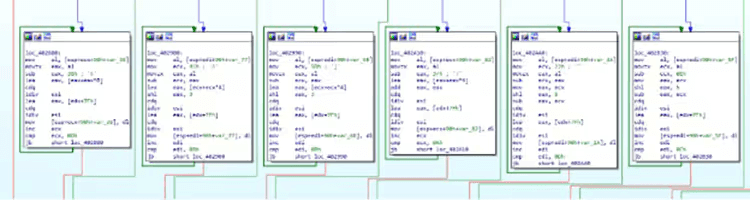
Figure 6. DLL name decoding loop
DLL names decoded at runtime:
shell32.dll | rstrtmgr.dll |
Stop Services and Processes
Before file encryption, the ransomware terminates a list of known running processes and services to encrypt as many files as possible. BlackSuit ransomware utilizes the Windows Restart Manager to terminate any process using files other than explorer.exe or a critical process.
Sequence of Windows Restart Manager APIs used by the ransomware:
RmStartSession | Starts the Restart Manager session. |
RmRegisterResources | Registers resources, in this case the targeted filename |
RmGetList | Determine which processes or services are using the registered resource (file) |
RmShutdown | Shuts down any identified process or service using the registered resource |
RmEndSession | Closes the Restart Manager session. |
The ransomware also uses Windows native CreateToolhelp32Snapshot, Process32FirstW, and Process32NextW APIs to enumerate processes in the system.
File and Directory Exclusions
The ransomware excludes system-related files and folders, ransomware-related files, and whitelisted extensions during encryption.
Excluded file extensions:
.com .ani .scr .drv .hta .rom .bin .msc .ps1 .shs .adv .msu .prf .bat .idx .mpa .cmd .msi .mod .ocx .ics .386 .sys .rtp .wpx .msp .cab .ldf .lnk .cur .nls .hlp .key .ico .exe .icns .lock .theme .diagpkg .diagcab .nomedia .diagcfg .msstyles .themepack .blacksuit .deskthemepack | ||
|---|---|---|
Excluded files and directories:
“msocache”, “intel”, “$recycle.bin”, “windows”, “windows.old”, “mozilla firefox”, “$WinREAgent”, “boot”, “google”, “perflogs”, “system volume information”, “appdata”, “tor browser”, “$windows.~ws”, “application data”, “$windows.~bt”, “mozilla”, “readme.blacksuit.txt” | ||
|---|---|---|
Inhibit System Recovery
Windows operating systems contain features that can help fix corrupted system files, including shadow copies, which are backups of files created by the Volume Shadow Copy Service (VSS). By deleting shadow copies, the ransomware can prevent victims from restoring files from backups, making it more difficult for them to recover their data without paying the ransom.
With the CreateProcessW function, the ransomware deletes volume shadow copies before file encryption by executing the following command:
cmd.exe /c vssadmin delete shadows /all /quiet | ||
|---|---|---|
Code in the ransomware showing this operation (the EAX register contains the kernel32.CreateProcessW address):
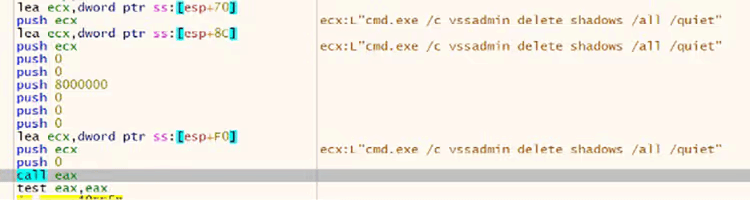
Figure 7. Create process call to delete volume shadow copies
System Network Connections Discovery
BlackSuit ransomware can enumerate network-mounted shares by scanning the network interfaces.
Data Encrypted for Impact
The ransomware initially finds available drives and loads the files one by one using the Windows API FindFirstFileW and FindNextFileW. It then uses OpenSSL AES keys to encrypt the files and adds the extension .blacksuit to the encrypted file name.
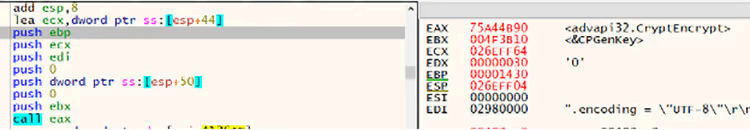
Figure 8. Windows native CryptEncrypt API call to encrypt the data
Public key:
—–BEGIN RSA PUBLIC KEY—– MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEA+O9FGkh466oxay/9u//rycLpGqFwcUSQIy0d27cnpRqq1W4De/boeoJC/HJqkr3WaEqr2JHgjSQcMimTxy8d3NLJT7M3uTVaxXD3Bck83ns5S/WhiF5tQGHtAGetGv8gXYSq/bm6HAlWBMBaOvv4of7ov7/cTAl1pwwgnaYzws4q6C9Q5zwmcU7DFcOohyVqBu/2svUlvtfMJGzYVeUJSUF6E2NMhClxddDLr32wCuoZ567uMBLQB2e5DUTkplR1OdVeyWyxhAXJSjQ5T9LpwuUHNm89nuo25slwlUx2m5a2k6wn2husXhXj+NRN/c2F3zh2qkcgs318XY8es1r3UgIBdCYMMGKsZ0DxKJZ1fq4nU93c+aP0qFBawmYhgIZq6MBYrG23LGbJPZvcC8pkyJrT51ygthCVPtpThqlthdqzqnV+7gPaf/XRwHeLkqawPhe1omd9m7gSuFwIREUe2MW1qZ7p3Nzhf8ZF4/YN7PSN1m6Ve5HS1MgnR9cbj655Jt3lqgW6rillrP+DbdrnjYo7yz2CsxSL3vKVtzcDzsbEFPkAFDyfSrYVxMYCEUJ8jHlctrNo+UiuZTT0O9dbwoGfCSrg8w+V0h8pYaiGnVwwGGkQbLgBAvz+iOOyElbZDLEPJxZ1+ipYzADufQSh8RHh/nXpWirlzQNH7oqrA0fUCAwEAAQ== —–END RSA PUBLIC KEY—– | ||
|---|---|---|
The ransomware encrypts files, adds the .blacksuit extension at the end of the encrypted files, and adds the following bytes at the end of the file (“??” represents variable bytes):
00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 ?? 00 00 00 ?? 00 00 00 | ||
|---|---|---|
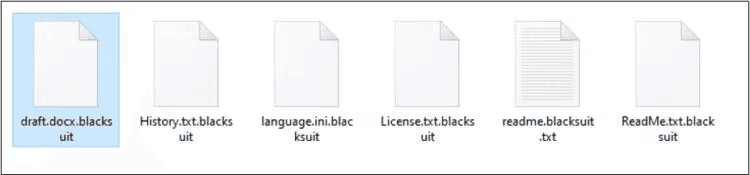
Figure 9. “.blacksuit” extension added to the encrypted files
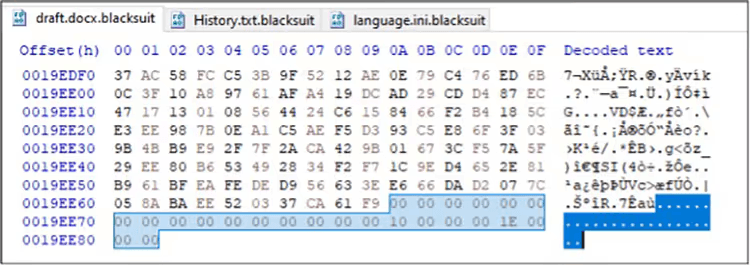
Figure 10. Padding bytes in encrypted files
Upon successful execution, the ransomware creates ransom notes with the file name readme.blacksuit.txt.
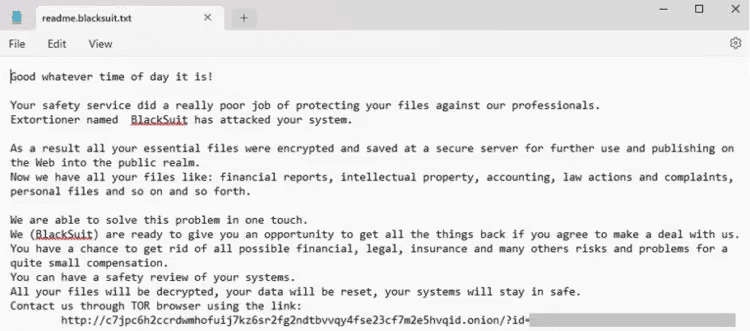
Figure 11. Screenshot of BlackSuit ransom note
Modify Registry
The ransomware did not perform any registry key modification.
Mutex
The mutex is the fundamental tool for managing shared resources between multiple threads or processes. Typically, ransomware uses a mutex to avoid reinfecting the victim system and causing multiple layers of encryption. The ransomware creates the following mutex value: “WLm87eV1oNRx6P3E4Cy9”.
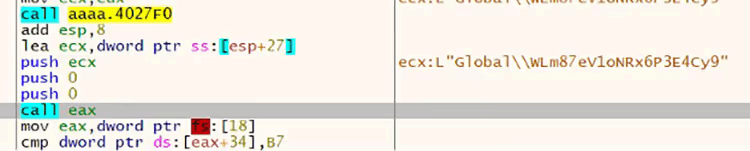
Figure 12. Screenshot of the mutex value created while debugging the ransomware
Network Activity
The ransomware did not try to communicate with a remote server other than encrypting data from mounted shares.
Indicators of Compromise
Indicator | Type | Context |
|---|---|---|
f1684fb118d4d8fc56653fcc49e12a659b64c4459ba037fa94f21783235cc6ba | SHA256 hash | BlackSuit ransomware |
C:\readme.blacksuit.txt | File path | BlackSuit ransom note |
.blacksuit | Extension | Encrypted files extension |
vssadmin delete shadows /all /quiet | Process | Volume Shadow Copy deletion |
WLm87eV1oNRx6P3E4Cy9 | Mutex | Mutex value object created by the BlackSuit ransomware |
Any 32-character string | Password | Command line argument needed to properly execute the ransomware. The ransomware developer doesn’t validate it |
c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid [.]onion | URL | TA data leak site (DLS) |
Data Leak Site
The ransom note contains a data leak site (DLS) that displayed the following page, self-identifying the group as BlackSuit:
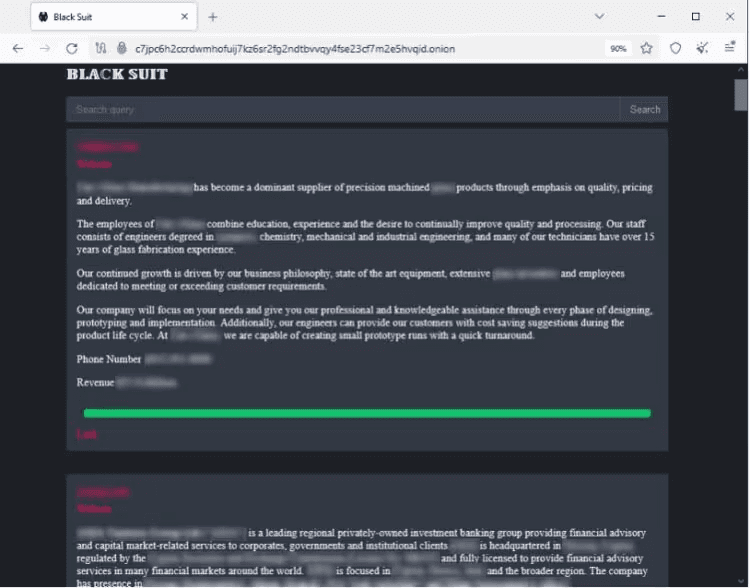
Figure 13. TOR DLS: c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion
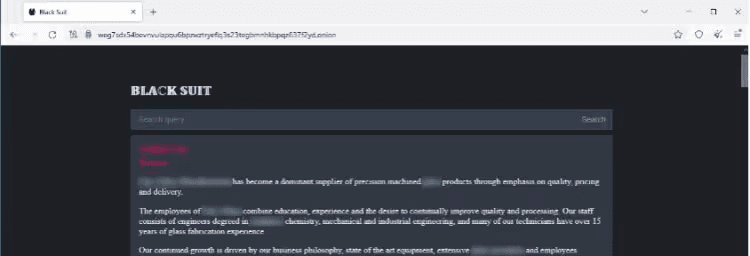
Figure 14. TOR DLS: weg7sdx54bevnvulapqu6bpzwztryeflq3s23tegbmnhkbpqz637f2yd[.]onion
Detection Mechanisms
Custom Detections and Blocking with Arete’s Arete Bloktd℠
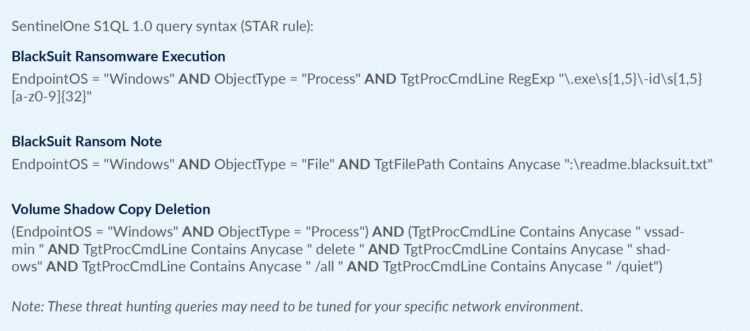
Yara
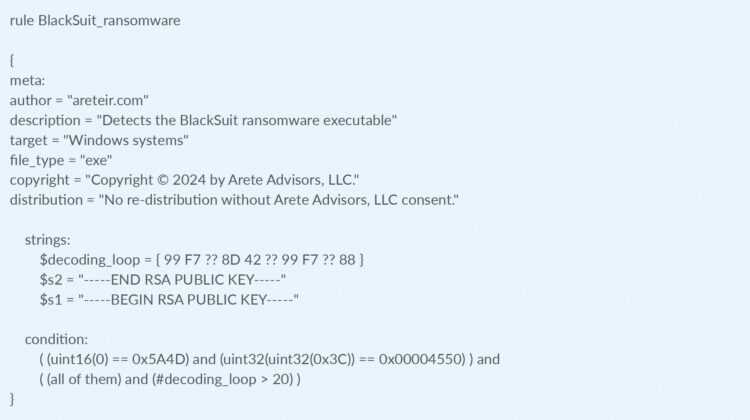
Recommended Mitigations
Utilize an endpoint detection and response (EDR) solution with the capability to halt detected processes and isolate systems on the network based on identified conditions.
Block any known attacker C2s in the firewall.
Implement multi-factor authentication on RDP and VPN to restrict access to critical network resources.
Eliminate unnecessary RDP ports exposed to the internet.
Block a high number of SMB connection attempts from one system to others in the network over a short period of time.
Perform periodic dark web monitoring to verify if data is available for sale on the black market.
Perform penetration tests.
Periodically patch systems and update tools.
Monitor connections to the network from suspicious locations.
Monitor downloads and uploads of files to file-sharing services outside standard work hours.
Monitor file uploads from domain controllers to the internet.
Monitor network scans from uncommon servers (e.g., RDP server).
Organizations can find the full list of US government recommended ransomware prevention and mitigation guidance here: https://www.cisa.gov/stopransomware/ransomware-guide.
Arete provides data-driven cybersecurity solutions to transform your response to emerging cyber threats. Learn more.
References
Back to Blog Posts

Article
Top 9 Security Controls for SMBs
In today’s complex cyber threat landscape, small and medium-sized businesses (SMBs) should implement a layered, multi-pronged approach to security. Here are some proven, effective controls to consider:
1. Implement MFA for All Users
Multi-factor authentication (MFA) is an effective and accessible way to protect sensitive data, comply with regulatory standards, and prevent unauthorized access to critical systems. By ensuring that users not only use a password but also a secure token, an organization can significantly reduce phishing attempts, credential stuffing attacks, and ransomware incidents. MFA should be enabled for email, VPN, and critical system access.
2. Update Patch Management Programs
A modern patching program should include policies and mechanisms to manage software updates in a timely manner. Patching efforts should address not just operating system updates, but also commonly utilized software within the environment. An active patching plan aims to reduce the mean time to patch and provide metrics on existing patch efforts. In the event of a high-severity vulnerability, a mature patching program should also be able to identify the risks and exposure for a given set of systems based on the average time to patch. This helps stakeholders make informed decisions when a new exploit is released.
3. Leverage a Properly Managed Endpoint Detection and Response (EDR) Tool
With real-time threat detection and advanced visibility, endpoint detection and response (EDR) solutions can enhance an organization’s ability to detect and investigate potential malicious activity, including ransomware, lateral movement, fileless attacks, and more. Effective management of EDR should include proper configuration, regular agent updates, and established procedures for responding to alerts.
4. Enhance EDR with Frontline Incident Intelligence
While EDR solutions are an important component of a security program, threat actors are continually adapting their techniques to evade detection, and as a result, standard detection methods may not always identify emerging threats or novel attack behaviors. To strengthen protection, organizations can supplement EDR tools with custom detection rules informed by incident response data. These rules can help identify indicators of compromise observed during cyber incidents, providing an additional layer of visibility beyond traditional detections.
Arete Bloktd℠ illustrates this approach by transforming threat intelligence and malware analysis into curated detection rules for EDR tools. Applying frontline intelligence to security tools can result in earlier detection, less investigative burden, and a more confident response.
5. Create and Continuously Test an Incident Response (IR) Plan
An incident response plan can help an organization effectively identify, respond to, and recover from a cybersecurity incident while minimizing disruption and downtime. An IR plan defines clear roles, escalation paths, communication strategies, and decision frameworks for both internal and external teams. To be effective, these plans should be regularly tested with post-incident reviews or tabletop exercises involving key stakeholders.
6. Maintain Encrypted and Tested Data Backups
In the case of a cyberattack, backups can help organizations maintain business continuity, support ransom negotiations with threat actors, and contribute to a timely and successful recovery. Encrypting backups makes it more difficult for threat actors to access or alter them, and regular testing ensures they remain accessible during a security incident.
7. Conduct Employee Security Awareness Training
Human error is a leading cause of cybersecurity incidents, and an organization’s employees are its first line of defense against cyber threats. Security awareness training reinforces the importance of data confidentiality, supports regulatory compliance, and helps employees recognize and understand red flags such as suspicious emails, malicious links, and social engineering attempts.
8. Assess and Address Existing Risk and Vulnerabilities
To maintain a proactive approach to risk management and improve resilience, organizations should regularly assess existing vulnerabilities through expert-led Vulnerability Assessments, Penetration Testing, and Threat Hunting Assessments. These exercises can help identify security gaps, support regulatory compliance, and prevent potential incidents. During remediation, prioritize high-impact vulnerabilities and make a plan for periodic assessments.
9. Apply Least-Privilege Access Controls
Employees should have access only to the systems, applications, and data necessary to perform their jobs. By removing unnecessary administrative privileges and regularly reviewing user permissions, organizations can reduce the risk of unauthorized access and limit the damage caused by compromised accounts or insider threats.
Organizations should regularly review their cybersecurity programs, stay informed about emerging threats, and evaluate whether their security controls are adapting to the evolving threat landscape.

Article
Ransomware Trends & Data Insights: August 2026
Although INC Ransom was the most active ransomware threat group observed in August 2026, overall activity remained relatively distributed across the threat landscape, with approximately 30 unique ransomware and extortion groups, including both established and newly emerged actors, observed during the month. Alongside INC Ransom, Storm, DragonForce, Qilin, and The Gentlemen were among the top five most active threat groups, underscoring the continued diversity and competitiveness of the ransomware ecosystem.
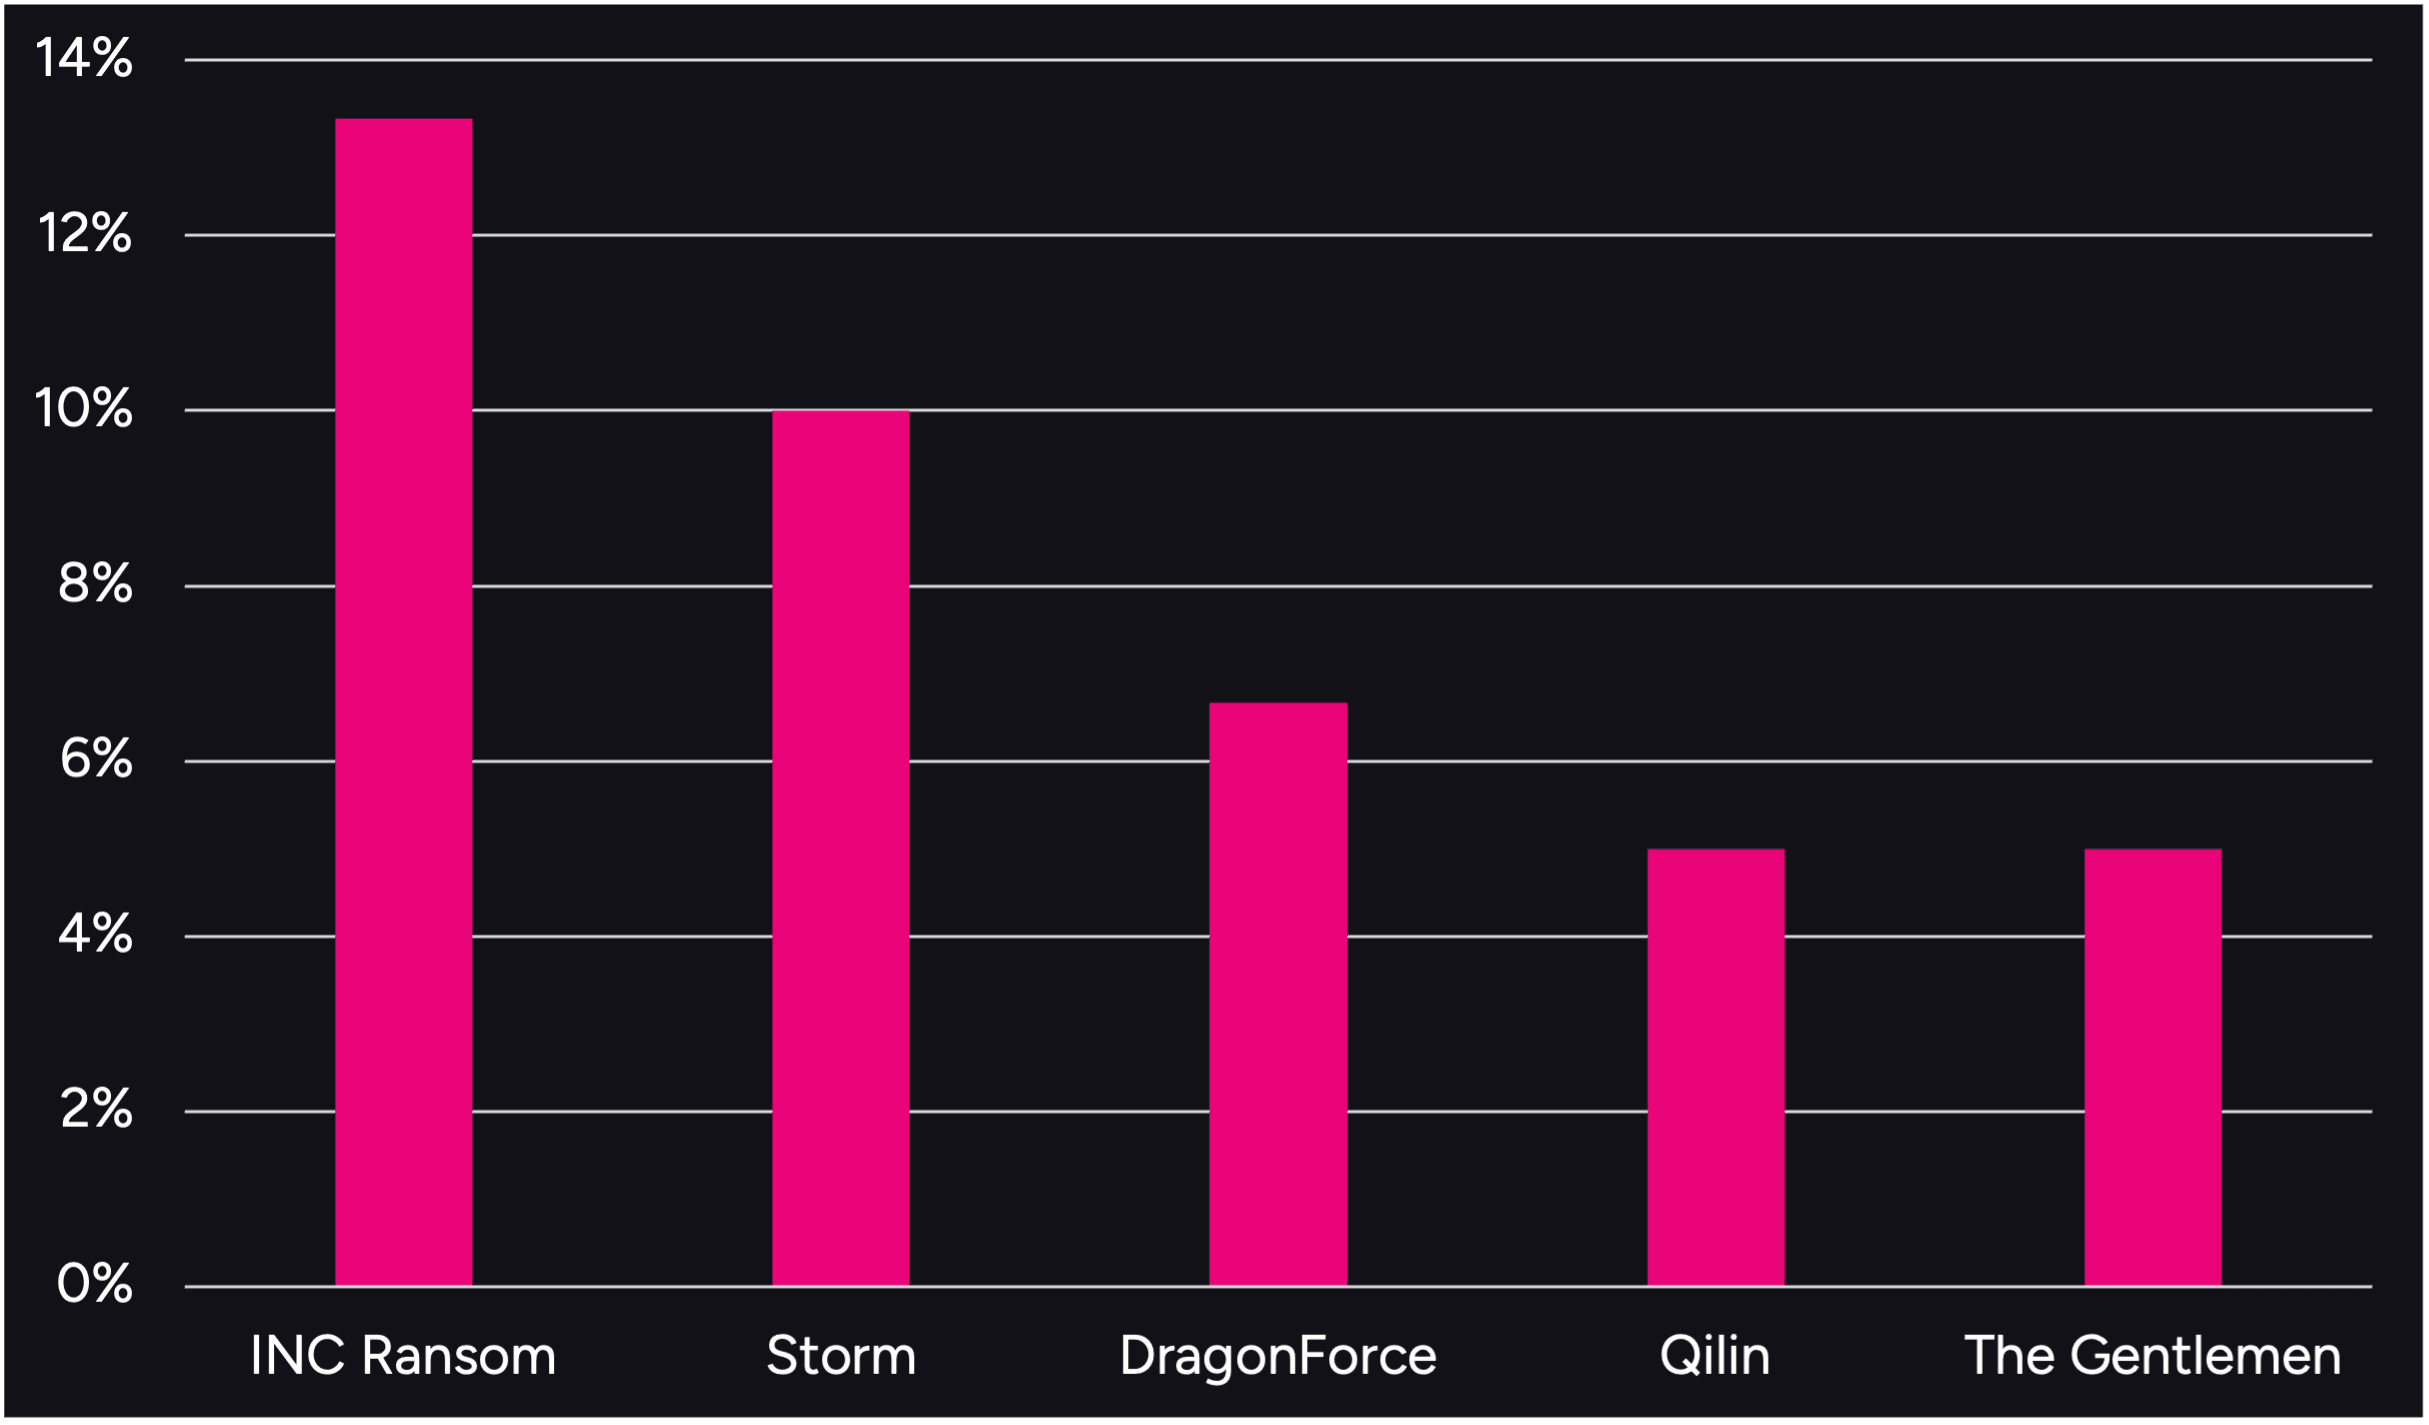
Figure 1. Activity from the top 5 threat groups in August 2026
Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
August 2026 was a significant month for the emergence of new threat actors, with Arete identifying several previously untracked ransomware groups, including Storm, Dark Project, DireWolf, Morpheus, Orova, Spirals, Wallstreet Team, and Zawoo Team. This trend underscores the ongoing evolution of the threat landscape and the low barriers to entry for new cybercriminal operations.
Arete observed a continued use of AI-enabled capabilities across the ransomware ecosystem during August. Similar to Fulcrumsec and Setra, the newly emerged Zawoo Team appears to leverage AI-assisted analysis of stolen data, publishing highly structured and detailed victim assessments on its data leak site (DLS). Additionally, both the Aurora and Storm ransomware groups have been observed utilizing AI-driven or AI-assisted chat representatives during victim communications. These developments suggest that threat actors are increasingly incorporating AI to enhance data analysis, automate victim engagement, and improve the effectiveness and scalability of extortion operations.
In August, Arete also observed that despite sustained law enforcement disruption efforts, LockBit continues to demonstrate operational resilience, likely through the expansion of its affiliate ecosystem and the evolution of its tactics. Recent activity indicates an increased reliance on data theft and exfiltration-only operations, with observed victimology suggesting a notable focus on organizations within the financial sector.
Sources
Arete Internal

Report
Arete's H1 2026 Crimeware Report
Explore intelligence and operational data from the frontlines of ransomware and extortion response as we detail the most significant trends and developments in the cyber threat landscape in the first half (H1) of 2026.

Article
WinRAR Path-Traversal Vulnerability Exploited in Ransomware Attacks
CISA has warned that CVE-2025-8088, a path-traversal vulnerability in WinRAR, is being exploited in ransomware attacks. The vulnerability allows attackers to use specially crafted archive files to place malicious executables in locations such as the Windows Startup folder, enabling code execution when the system restarts. WinRAR addressed this vulnerability in version 7.13, but exploitation has continued due to challenges in updating the software. CISA's updated KEV entry now specifically identifies the vulnerability as being used in ransomware attacks.
What’s Notable and Unique
The vulnerability was initially exploited as a zero-day by the Russia-linked RomCom group, enabling malware execution at user logon and supporting credential theft, cyberespionage, and ransomware-related activities.
CVE-2025-8088 continues to be actively exploited by both government-backed and financially motivated threat actors. Observed campaigns have been attributed to Russian- and Chinese-linked groups targeting several organizations.
Phishing campaigns leveraging weaponized RAR attachments exploited CVE-2025-8088 to silently place malicious payloads in autorun locations using directory traversal and Alternate Data Streams (ADS).
The widespread exploitation of CVE-2025-8088 highlights strong demand for effective WinRAR exploits, with multiple underground vendors previously supplying exploit capabilities to a diverse range of threat actors. One such vendor, zeroplayer, advertised a WinRAR exploit in July 2025.
Analyst Comments
Organizations should immediately upgrade WinRAR to version 7.13 or later and conduct an enterprise-wide inventory to identify unmanaged installations. Given that WinRAR lacks automatic updates, Group Policy support, and integration with common enterprise patch management platforms, manual verification and remediation may be required to ensure all vulnerable instances are addressed. Security teams should also enhance defenses against archive-based phishing attacks by blocking or scrutinizing unsolicited compressed files, monitoring for suspicious file creation in Windows Startup directories, and detecting abuse of ADS. With CISA now linking CVE-2025-8088 to ransomware activity, organizations should treat remediation as a high priority and actively monitor for indicators of WinRAR-based exploitation across their environments.
Sources
CISA Adds Three Known Exploited Vulnerabilities to Catalog
WinRAR vulnerability being exploited in ransomware attacks, CISA warns