Report
Threat Actor Spotlight: BlackSuit Ransomware
Arete Analysis
Tips
Download The Report
Executive Summary
Since May 2023, Arete’s Incident Response (IR) team has responded to multiple BlackSuit ransomware engagements against organizations in the healthcare, financial services, manufacturing, professional services, public service, entertainment, and retail sectors. This spotlight explores the ransomware behavior observed, statistics from IR engagements, and background information on the threat actor. Finally, we discuss security recommendations to better defend against this evolving cyber threat and mitigate the risk of financial and reputational losses arising from these incidents.
Incident Response Data on BlackSuit Ransomware
The information below is based on BlackSuit incidents investigated by Arete since May 2023. Our IR and teams work together to analyze key data points during every ransomware engagement and form real-time threat actor (TA) insights.
Arete has investigated dozens of engagements involving BlackSuit.
We have been extremely successful in negotiating discounted ransoms with this TA.
The highest observed ransom demand is around $18 million.
The average initial demand is around $2.5 million.
The average ransom payment facilitated is around $500,000.
Commonly observed methods of intrusions include remote desktop protocol (RDP), virtual private network (VPN), and firewall vulnerabilities.
Tools observed during the investigations include CobaltStrike, WinRAR, PUTTY, Rclone, Advanced IP Scanner, Network Scanner, Mimikatz, and GMER.
A commonly observed ransom note filename is readme.blacksuit.txt.
In some instances, backups were encrypted or deleted, while in others, backups were used for restoration.
Background
The information about the BlackSuit threat actor group in this section was shared in Arete’s 2024 Q1 Crimeware Report.
The most notable newcomer in Q1 was BlackSuit, the third most active group of Q1. Although Arete first observed BlackSuit ransomware operating in May 2023, it only accounted for less than a half percent of the total engagements in 2023. The group significantly increased its activity in Q1 2024, and there were more BlackSuit engagements in February 2024 alone than in all of 2023. BlackSuit operates as a private group without affiliates, targeting both Windows and Linux users and utilizing a double extortion method of stealing and encrypting sensitive data on a victim’s network.
BlackSuit: A Continuation of Royal Ransomware?
The BlackSuit ransomware payload has significant code overlap with Royal ransomware, and the Cybersecurity and Infrastructure Security Agency (CISA) and the FBI believe BlackSuit to likely be a rebranding or spinoff variant of Royal. While BlackSuit could be using the same developer or code with slight modifications, Arete also observed language used by BlackSuit in ransom negotiations identical to previous engagements with Royal, which lends to the assessment that the group might be a rebrand or offshoot. Regardless, BlackSuit’s emergence demonstrates that although names may change, threat actors will find ways to adapt and evolve their operations.
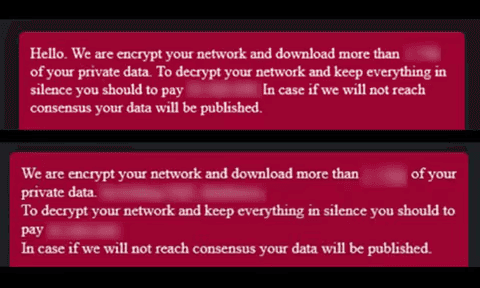
Figure 1. Language from two separate BlackSuit TOR chats (Source: Arete)
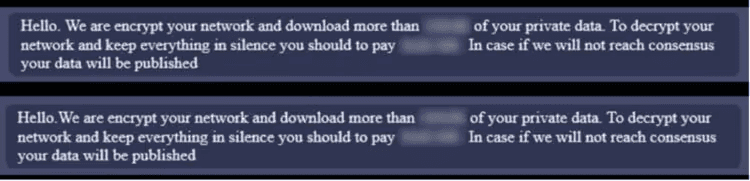
Figure 2. Identical language from two separate Royal TOR chats (Source: Arete)
Technical Analysis
Malware analysis revealed that BlackSuit ransomware:
Supports multiple command-line arguments.
Encrypts files on the system and mounted shares.
Adds the following extension to encrypted files: .blacksuit (e.g., file.docx.blacksuit).
Creates a ransom note with the following filename: readme.blacksuit.txt.
Self-identifies the group as BlackSuit in the ransom note.
References a data leak site in the ransom note that, when accessed, self-identifies the group as BlackSuit.
Kills a list of processes and services.
Maintains a list of whitelisted files and directories to make sure it will not render the system unusable, preventing recovery when running a decryptor.
Attempts to prevent system recovery by deleting the system’s volume shadow copies.
Creates the following mutex during execution: WLm87eV1oNRx6P3E4Cy9.
Execution Pattern/Arguments
BlackSuit ransomware needs command line arguments to execute and encrypt files in the system. Command line arguments supported:
Command line argument | Description |
|---|---|
-id [32-byte characters] | Ransomware ID |
-size | Invoked with drag and drop |
-ep | Number that represents the percentage of the file that will be encrypted |
-path [target_directory_path] | Used to specify a target directory to encrypt |
-localonly | Encrypt only the local system |
-networkonly | Encrypt only shared volumes/directory |
-aavm | Encrypt all files |
The ransomware will not execute in the system without the “–id” argument followed by a 32-character value that is unique in each engagement and present in the ransom note TOR URL. Portion of the data in the ransom note that contains the ID:
All your files will be decrypted, your data will be reset, your systems will stay in safe. Contact us through TOR browser using the link: http://c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion/?id=[32-characters] | ||
|---|---|---|
Execution of ransomware to encrypt files:
blacksuit.exe -id [32-characters] | ||
|---|---|---|
The ransomware developer coded the logic to allow configuration of the 32-character value in the command line during execution. This same victim-specific 32-character string value is then added to the ransom note URL used for negotiations. Due to this implementation in the ransomware code, threat researchers can execute the ransomware without knowing the 32-character string value, as any value of this type can be used to execute the malicious code. In analyzing Royal ransomware samples, Arete found a similarity in that any 32-character value can be supplied to execute the ransomware, and the value is also added to the ransom note TOR chat URL.
Example of how the ransom note content looks with a randomly supplied string (e.g., blacksuit.exe -id 7777777777777777777777777777777):
All your files will be decrypted, your data will be reset, your systems will stay in safe. Contact us through TOR browser using the link: http://c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion/?id=77777777777777777777777777777777777777 | ||
|---|---|---|
Obfuscated Files or Information: Software Packing
Most of the strings in the ransomware are encoded. The encoded strings are hardcoded and decoded at runtime. Every encoded string has its own decoding loop:
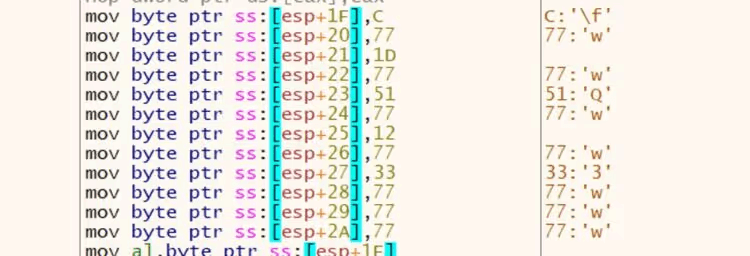
Figure 3. Encoded strings hardcoded
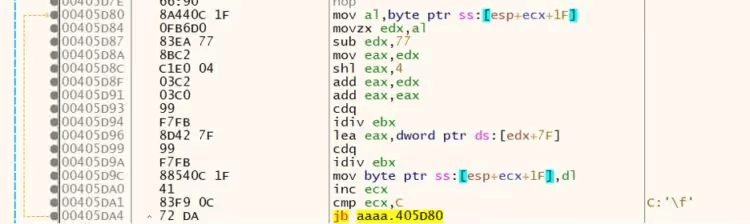
Figure 4. String decoding loop
Some relevant strings decoded in memory:
Global\\\WLm87eV1oNRx6P3E4Cy9 | -ep |
Obfuscated Files or Information: Dynamic API Resolution
To avoid static or other defensive analysis, the ransomware uses dynamic API resolution to conceal malware characteristics and functionality. The ransomware initially decrypts DLL names, then loads the APIs. Hardcoded encoded DLL names are shown below:
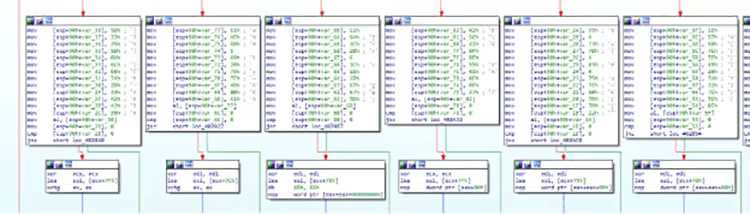
Figure 5. Encoded DLL names
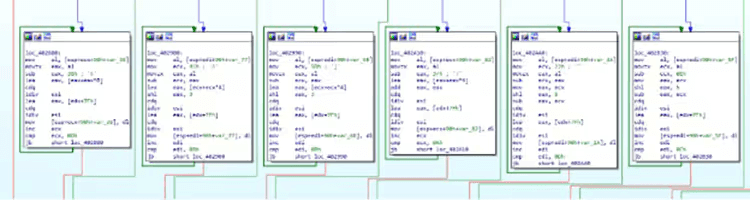
Figure 6. DLL name decoding loop
DLL names decoded at runtime:
shell32.dll | rstrtmgr.dll |
Stop Services and Processes
Before file encryption, the ransomware terminates a list of known running processes and services to encrypt as many files as possible. BlackSuit ransomware utilizes the Windows Restart Manager to terminate any process using files other than explorer.exe or a critical process.
Sequence of Windows Restart Manager APIs used by the ransomware:
RmStartSession | Starts the Restart Manager session. |
RmRegisterResources | Registers resources, in this case the targeted filename |
RmGetList | Determine which processes or services are using the registered resource (file) |
RmShutdown | Shuts down any identified process or service using the registered resource |
RmEndSession | Closes the Restart Manager session. |
The ransomware also uses Windows native CreateToolhelp32Snapshot, Process32FirstW, and Process32NextW APIs to enumerate processes in the system.
File and Directory Exclusions
The ransomware excludes system-related files and folders, ransomware-related files, and whitelisted extensions during encryption.
Excluded file extensions:
.com .ani .scr .drv .hta .rom .bin .msc .ps1 .shs .adv .msu .prf .bat .idx .mpa .cmd .msi .mod .ocx .ics .386 .sys .rtp .wpx .msp .cab .ldf .lnk .cur .nls .hlp .key .ico .exe .icns .lock .theme .diagpkg .diagcab .nomedia .diagcfg .msstyles .themepack .blacksuit .deskthemepack | ||
|---|---|---|
Excluded files and directories:
“msocache”, “intel”, “$recycle.bin”, “windows”, “windows.old”, “mozilla firefox”, “$WinREAgent”, “boot”, “google”, “perflogs”, “system volume information”, “appdata”, “tor browser”, “$windows.~ws”, “application data”, “$windows.~bt”, “mozilla”, “readme.blacksuit.txt” | ||
|---|---|---|
Inhibit System Recovery
Windows operating systems contain features that can help fix corrupted system files, including shadow copies, which are backups of files created by the Volume Shadow Copy Service (VSS). By deleting shadow copies, the ransomware can prevent victims from restoring files from backups, making it more difficult for them to recover their data without paying the ransom.
With the CreateProcessW function, the ransomware deletes volume shadow copies before file encryption by executing the following command:
cmd.exe /c vssadmin delete shadows /all /quiet | ||
|---|---|---|
Code in the ransomware showing this operation (the EAX register contains the kernel32.CreateProcessW address):
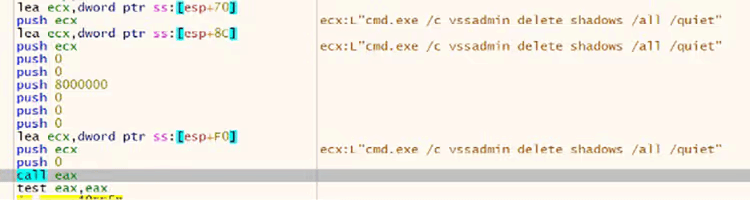
Figure 7. Create process call to delete volume shadow copies
System Network Connections Discovery
BlackSuit ransomware can enumerate network-mounted shares by scanning the network interfaces.
Data Encrypted for Impact
The ransomware initially finds available drives and loads the files one by one using the Windows API FindFirstFileW and FindNextFileW. It then uses OpenSSL AES keys to encrypt the files and adds the extension .blacksuit to the encrypted file name.
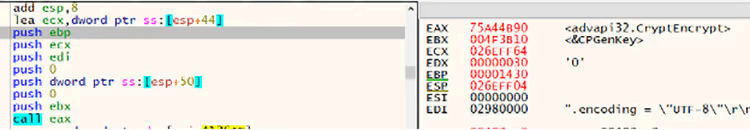
Figure 8. Windows native CryptEncrypt API call to encrypt the data
Public key:
—–BEGIN RSA PUBLIC KEY—– MIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEA+O9FGkh466oxay/9u//rycLpGqFwcUSQIy0d27cnpRqq1W4De/boeoJC/HJqkr3WaEqr2JHgjSQcMimTxy8d3NLJT7M3uTVaxXD3Bck83ns5S/WhiF5tQGHtAGetGv8gXYSq/bm6HAlWBMBaOvv4of7ov7/cTAl1pwwgnaYzws4q6C9Q5zwmcU7DFcOohyVqBu/2svUlvtfMJGzYVeUJSUF6E2NMhClxddDLr32wCuoZ567uMBLQB2e5DUTkplR1OdVeyWyxhAXJSjQ5T9LpwuUHNm89nuo25slwlUx2m5a2k6wn2husXhXj+NRN/c2F3zh2qkcgs318XY8es1r3UgIBdCYMMGKsZ0DxKJZ1fq4nU93c+aP0qFBawmYhgIZq6MBYrG23LGbJPZvcC8pkyJrT51ygthCVPtpThqlthdqzqnV+7gPaf/XRwHeLkqawPhe1omd9m7gSuFwIREUe2MW1qZ7p3Nzhf8ZF4/YN7PSN1m6Ve5HS1MgnR9cbj655Jt3lqgW6rillrP+DbdrnjYo7yz2CsxSL3vKVtzcDzsbEFPkAFDyfSrYVxMYCEUJ8jHlctrNo+UiuZTT0O9dbwoGfCSrg8w+V0h8pYaiGnVwwGGkQbLgBAvz+iOOyElbZDLEPJxZ1+ipYzADufQSh8RHh/nXpWirlzQNH7oqrA0fUCAwEAAQ== —–END RSA PUBLIC KEY—– | ||
|---|---|---|
The ransomware encrypts files, adds the .blacksuit extension at the end of the encrypted files, and adds the following bytes at the end of the file (“??” represents variable bytes):
00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 ?? 00 00 00 ?? 00 00 00 | ||
|---|---|---|
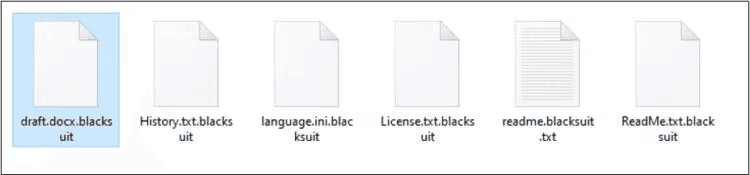
Figure 9. “.blacksuit” extension added to the encrypted files
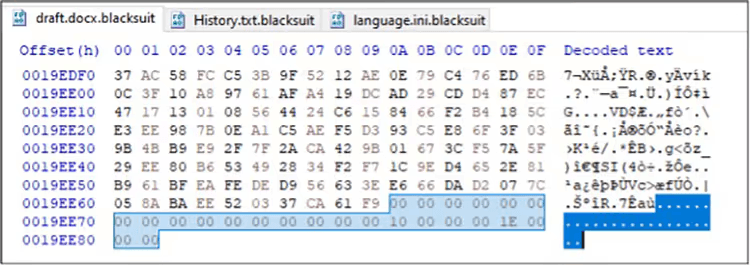
Figure 10. Padding bytes in encrypted files
Upon successful execution, the ransomware creates ransom notes with the file name readme.blacksuit.txt.
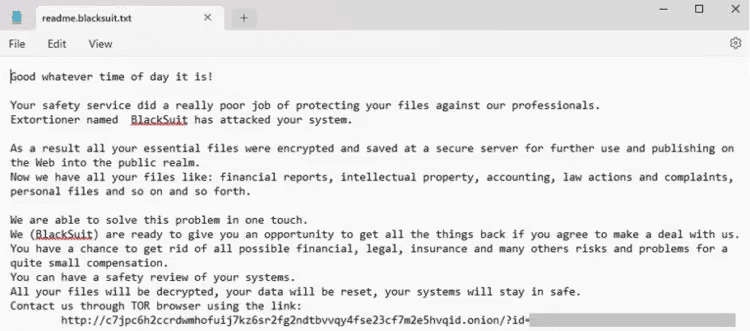
Figure 11. Screenshot of BlackSuit ransom note
Modify Registry
The ransomware did not perform any registry key modification.
Mutex
The mutex is the fundamental tool for managing shared resources between multiple threads or processes. Typically, ransomware uses a mutex to avoid reinfecting the victim system and causing multiple layers of encryption. The ransomware creates the following mutex value: “WLm87eV1oNRx6P3E4Cy9”.
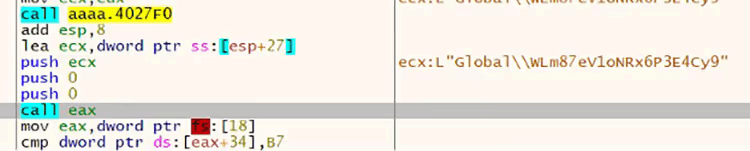
Figure 12. Screenshot of the mutex value created while debugging the ransomware
Network Activity
The ransomware did not try to communicate with a remote server other than encrypting data from mounted shares.
Indicators of Compromise
Indicator | Type | Context |
|---|---|---|
f1684fb118d4d8fc56653fcc49e12a659b64c4459ba037fa94f21783235cc6ba | SHA256 hash | BlackSuit ransomware |
C:\readme.blacksuit.txt | File path | BlackSuit ransom note |
.blacksuit | Extension | Encrypted files extension |
vssadmin delete shadows /all /quiet | Process | Volume Shadow Copy deletion |
WLm87eV1oNRx6P3E4Cy9 | Mutex | Mutex value object created by the BlackSuit ransomware |
Any 32-character string | Password | Command line argument needed to properly execute the ransomware. The ransomware developer doesn’t validate it |
c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid [.]onion | URL | TA data leak site (DLS) |
Data Leak Site
The ransom note contains a data leak site (DLS) that displayed the following page, self-identifying the group as BlackSuit:
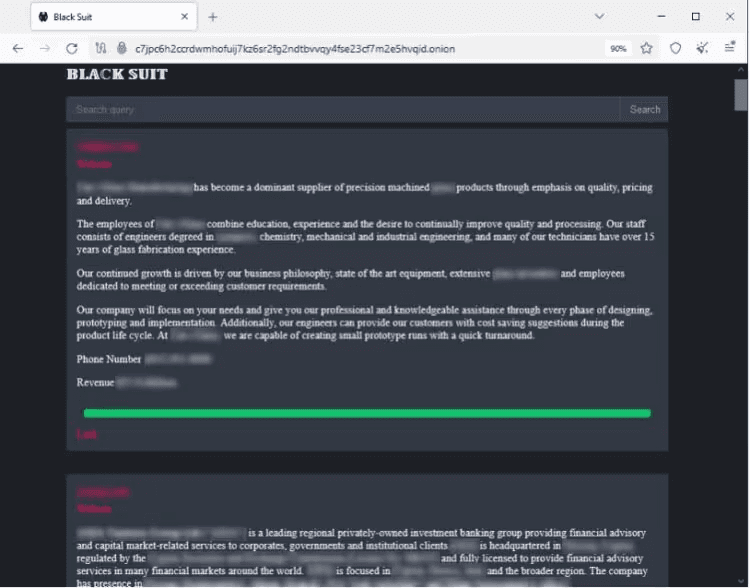
Figure 13. TOR DLS: c7jpc6h2ccrdwmhofuij7kz6sr2fg2ndtbvvqy4fse23cf7m2e5hvqid[.]onion
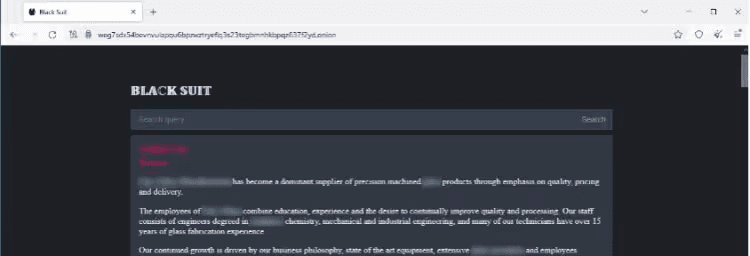
Figure 14. TOR DLS: weg7sdx54bevnvulapqu6bpzwztryeflq3s23tegbmnhkbpqz637f2yd[.]onion
Detection Mechanisms
Custom Detections and Blocking with Arete’s Arete Bloktd℠
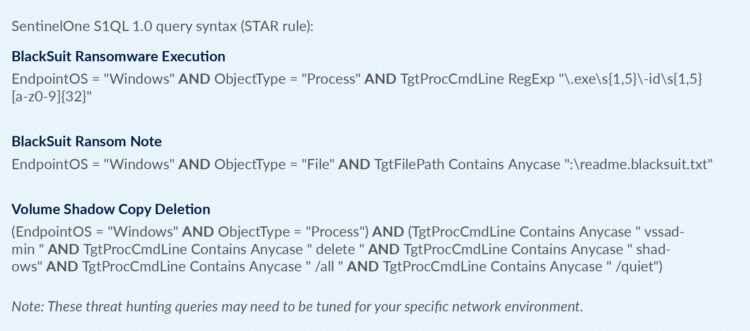
Yara
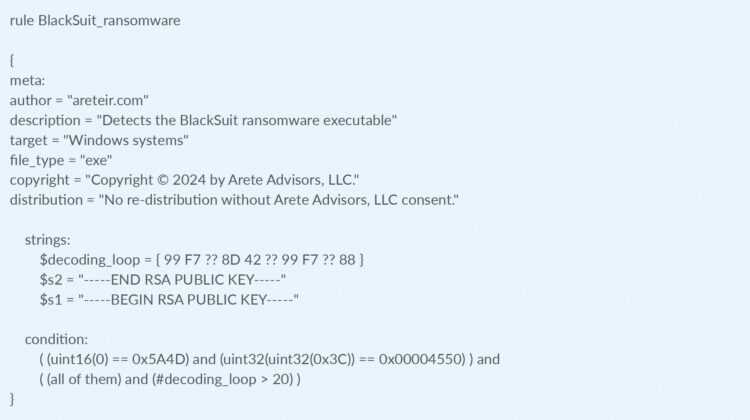
Recommended Mitigations
Utilize an endpoint detection and response (EDR) solution with the capability to halt detected processes and isolate systems on the network based on identified conditions.
Block any known attacker C2s in the firewall.
Implement multi-factor authentication on RDP and VPN to restrict access to critical network resources.
Eliminate unnecessary RDP ports exposed to the internet.
Block a high number of SMB connection attempts from one system to others in the network over a short period of time.
Perform periodic dark web monitoring to verify if data is available for sale on the black market.
Perform penetration tests.
Periodically patch systems and update tools.
Monitor connections to the network from suspicious locations.
Monitor downloads and uploads of files to file-sharing services outside standard work hours.
Monitor file uploads from domain controllers to the internet.
Monitor network scans from uncommon servers (e.g., RDP server).
Organizations can find the full list of US government recommended ransomware prevention and mitigation guidance here: https://www.cisa.gov/stopransomware/ransomware-guide.
Arete provides data-driven cybersecurity solutions to transform your response to emerging cyber threats. Learn more.
References
Back to Blog Posts

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory

Article
Ransomware Trends & Data Insights: September 2026
The Akira ransomware group re-emerged as the most active ransomware threat observed by Arete in September. Overall activity remained relatively distributed among multiple threat groups, with 29 unique groups observed throughout the month. Alongside Akira, INC Ransom and the relatively new Storm group were among the three most active threat actors observed in September. Several new threat groups also emerged during the month, including Hades Team, Shiba, and Vortex (which is suspected to be part of the cluster of threat actors affiliated with the former BlackFile group).

Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
In September 2026, the ShinyHunters threat group escalated its extortion activity by publicly targeting both the Clop ransomware group and the FBI. The group claimed to have breached and defaced Clop’s infrastructure, demanding an eight-figure ransom, while separately alleging the theft of sensitive FBI-related data and demanding the retraction of statements made in a prior public advisory. In both incidents, ShinyHunters employed similar pressure tactics, including website defacements, repeated public postings, and threats of data disclosure.
ClickFix attacks remained prevalent in September 2026, with ransomware groups including Qilin, Helix, and The Gentlemen leveraging ClickFix lures to facilitate PowerShell-based payload execution and initial access. The technique continues to evolve, combining social engineering with legitimate tools and services to enable compromise and evade detection.
September 2026 saw continued activity from the former BlackFile extortion ecosystem. BlackFile, a data theft and extortion operation active since at least October 2025, rebranded as Redact in May 2026, and since appears to have broken off into several affiliated brands, including Pink, Helix, Falcon, Cinder, and potentially Vortex. During September, some affiliates publicly disputed these associations and claimed to operate independently. However, the coordinated timing, messaging, and near-identical nature of these statements support the assessment that these groups remain part of a broader interconnected ecosystem operating under shared objectives or coordination.

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM

Article
AI Agents Used in Campaign Against PaperCut
In late August, a threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG and MF servers. PaperCut is print management software, and researchers determined that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries. The AI agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078 both security flaws affecting PaperCut software and flagged as actively exploited earlier this month. It is currently unclear if the threat actor is solely focused on access development to be handed off to other affiliated actors, or if they will directly leverage their access to achieve follow-on objectives such as data theft or ransomware deployment.
What’s Notable and Unique
Researchers observed three attack paths following the exploitation of vulnerable PaperCut servers. Threat actors would harvest credentials from LSASS memory and registry secrets to perform pass-the-hash attacks, leverage older unpatched Windows vulnerabilities (CVE-2021-42278 and CVE-2021-42287) to escalate privileges in unpatched environments, or, in some cases, directly add newly created accounts to the Domain Admins group when PaperCut was running with domain-level privileges.
Upon achieving remote code execution and credential harvesting within a self-hosted lab environment, the threat actor deployed hundreds of AI-powered agents that leveraged OpenAI Codex, DeepSeek models, and publicly available offensive security tools, including Mimikatz, SharpHound, Certipy, Rubeus, and Impacket, to automate reconnaissance, exploitation, and post-compromise activities. The attackers subsequently used a DCSync attack to obtain a database dump containing domain credentials.
Analyst Comments
The observed activity demonstrates how threat actors are increasingly leveraging AI and large language models (LLMs) to accelerate cyber operations at unprecedented speed and scale. In this campaign, the adversary progressed from exploit development to remote code execution within hours and, in some cases, achieved Domain Administrator privileges in as little as five minutes. The AI-assisted workflow enabled rapid reconnaissance, exploitation, credential theft, privilege escalation, and lateral movement, allowing the compromise of multiple organizations within seconds. This activity highlights the growing threat posed by AI-enabled adversaries capable of conducting large-scale intrusions with greater efficiency and operational velocity. Organizations affected by the PaperCut vulnerabilities are strongly advised to apply the latest security updates and implement the vendor's recommended mitigation measures to reduce the risk of compromise and unauthorized access.
Sources
Agents Gone Wild: An AI-Orchestrated Global Campaign Against PaperCut NG/MF
AI-powered attack exploited PaperCut flaws to hack 395 organizations
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances