Report
Malware Spotlight: Fog Ransomware
Arete Analysis
Tips
Cybersecurity Trends
Download The Report
Executive Summary
Since April 2024, Arete’s Incident Response (IR) team has responded to multiple engagements attributed to the Fog ransomware group. Engagements attributed to this group have been trending up since mid-June and through July 2024, accounting for nearly 20% of Arete’s ransomware and extortion engagements in July. The Fog ransomware group is especially noteworthy as it is one of the few threat actors specifically targeting one industry: education. Since April, Arete has observed that 70% of Fog victims have been education organizations. This spotlight explores the ransomware group’s observed behavior, background information on the threat actor, and statistics from Incident Response engagements, along with a technical analysis of Fog’s ransomware executable. Finally, we discuss security recommendations to better defend against this evolving cyber threat and mitigate the risk of financial and reputation losses.
Incident Response Data on the Fog Ransomware Group
The information below is based on Fog ransomware incidents investigated by Arete since April 2024. Our IR, Threat Intelligence, and Data Analytics teams work together to analyze key data points during every ransomware engagement and form real-time threat actor (TA) insights.
The median initial demand is $220,000.
The median ransom payment facilitated is $100,000.
36% of engagements involved data exfiltration, often using tools like MEGAsync and Filezilla.
Common initial access vectors include brute force attacks against remote desktop protocol (RDP) and compromised virtual private network (VPN) credentials.
Tools observed during investigations include CobaltStrike, Mimikatz, ngrok, WinRAR, AnyDesk, Advanced Port Scanner, and GMER, among others. The group demonstrates distinct skill in evading common anti-malware defenses.
The ransom note file name is commonly “readme.txt” and includes a link to a TOR site used for negotiations.
The group operates a data leak site (DLS) self-proclaimed as “The Fog Blog.”
Background
Fog ransomware was a prominent newcomer in the second quarter (Q2) of 2024 and demonstrated a noticeable trend of attacking entities in the education sector. Arete engagements involving Fog ransomware more than doubled during July 2024 compared to previous months.
Technical Analysis
Malware analysis revealed that Fog ransomware:
Supports multiple command-line arguments.
Encrypts files on the system and mounted shares.
Adds the following extensions to encrypted files: .fog, .ffog, or .flocked (e.g., file.docx.flocked).
Creates a ransom note with the following filename: readme.txt.
Self-identifies the group as Fog in the ransom note.
References a data leak site in the ransom note that, when accessed, self-identifies the group as Fog.
Kills a list of processes and services.
Maintains a list of whitelisted files and directories to make sure it will not render the system unusable, preventing recovery when running a decryptor.
Attempts to prevent system recovery by deleting the system’s volume shadow copies.
Creates a mutex during execution.
Creates a log file named DbgLog.sys.Execution Pattern/Arguments
Fog ransomware needs command line arguments to execute and encrypt files in the system. Command line arguments supported:
Command line arguments | Description |
|---|---|
-id | Key to decrypt ransomware configuration. |
-nomutex | Skip mutex check. |
-target | Specific location to encrypt files. |
-console | Creates a new console window for output. |
-size | File size threshold to encrypt. |
-log | Log the ransomware activity. |
-procoff | Presently unknown. |
-uncoff | Presently unknown. |
The ransomware will not execute in the system without the “-id” argument followed by a 6-character value that is unique in each engagement.
Execution of the ransomware to encrypt files:
Fog.exe -id [6-characters] Example: | ||
|---|---|---|
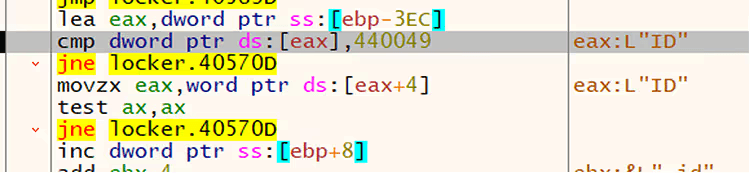
Figure 1. Code in the ransomware to check command line argument “-ID”
The ransomware uses the “-id” argument followed by a 6-character value to decrypt a JSON-based ransomware configuration information at runtime. Decrypted JSON field name and descriptions:
Name | Description |
|---|---|
RSAPubKey | Public key used in the file encryption process. |
LockedExt | Extension added to encrypted files. |
NoteFileName | Ransom note name. |
PathStopList | Excludes listed directories. |
FileMaskStopList | Excludes listed file extensions. |
ShutdownProcesses | Terminates list of processes. |
ShutdownServices | Terminates list of services. |
Stop Services and Processes
Before file encryption, the ransomware terminates a pre-determined list of processes and services to encrypt as many files as possible.
Process names:
“notepad.exe”, “calc.exe”, “*sql*” | ||
|---|---|---|
Service names:
“Dhcp”, “Dnscache”, “*sql*” | ||
|---|---|---|
Code in the ransomware showing this operation:
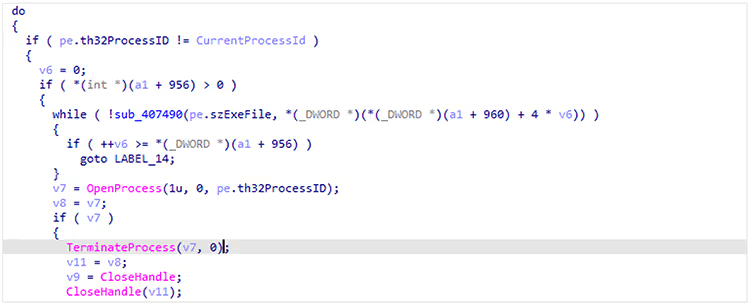
Figure 2. Process termination decompiled code
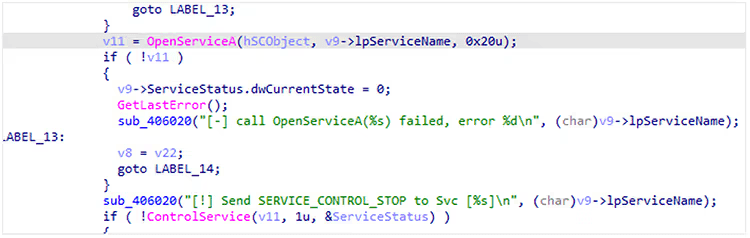
Figure 3. Service termination decompiled code
File and Directory Exclusions
The ransomware excludes system-related files and folders, ransomware-related files, and whitelisted extensions during encryption.
Excluded file extensions:
“*.exe”, “*.dll”, “*.lnk”, “*.sys” | ||
|---|---|---|
Excluded directories:
“tmp”, “winnt”, “Application Data”, “AppData”, “temp”, “thumb”, “$Recycle.Bin”, “System Volume Information”, “Windows”, “Boot” | ||
|---|---|---|
Inhibit System Recovery
Windows operating systems contain features that can help fix corrupted system files, including shadow copies, which are backups of files created by the Volume Shadow Copy Service (VSS). By deleting shadow copies, the ransomware can prevent victims from restoring files from backups, making it more difficult for them to recover their data without paying the ransom.
The ransomware deletes volume shadow copies before file encryption by starting the following process:
cmd.exe /c vssadmin delete shadows /all /quiet | ||
|---|---|---|
System Network Connections Discovery
Fog ransomware can enumerate network-mounted shares by scanning the network interfaces.
Data Encrypted for Impact
The ransomware initially finds available drives and then loads the files one by one using the Windows API FindFirstFileW and FindNextFileW. The ransomware generates random AES keys to encrypt the files, and after encrypting them, the keys are encrypted using a public RSA key. The resulting key is again encrypted and placed at the end of the file.
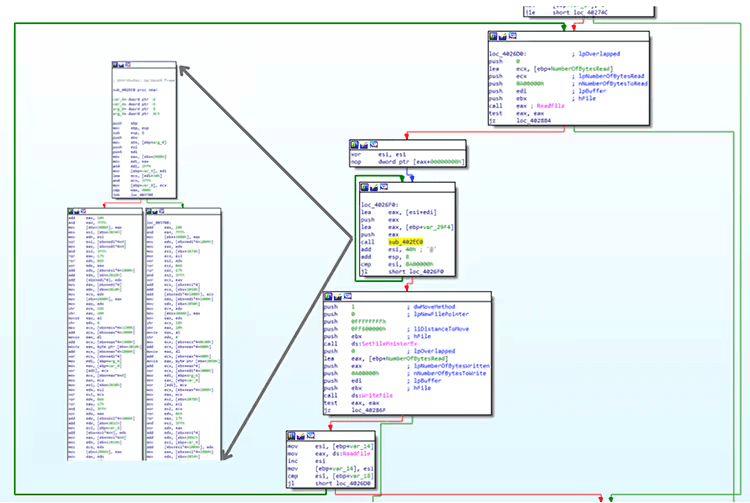
Figure 4. Data encryption code
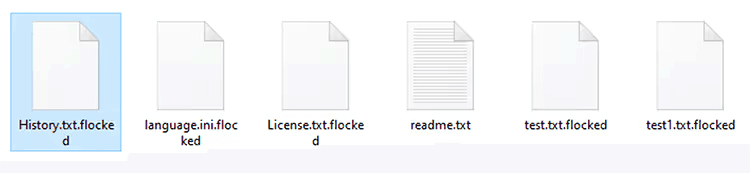
Figure 5. Extension added to the encrypted files
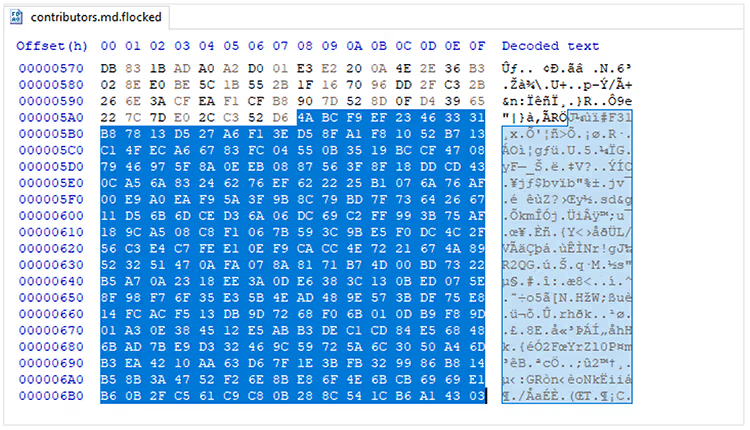
Figure 6. Encrypted AES key appended to encrypted file.
Fog ransomware extensions observed:
“.FOG”, “.FLOCKED”, “.FFOG” | ||
|---|---|---|
During execution, the ransomware creates a file named DbgLog.sys in the same directory and logs the ransomware activity. If the “-log” argument is used during ransomware execution, the ransomware creates and encrypts a lock_log.txt file under the C:\ProgramData directory. Encrypting the lock_log.txt file created might be an oversight in the ransomware code possibly indicating that the ransomware is still under development.
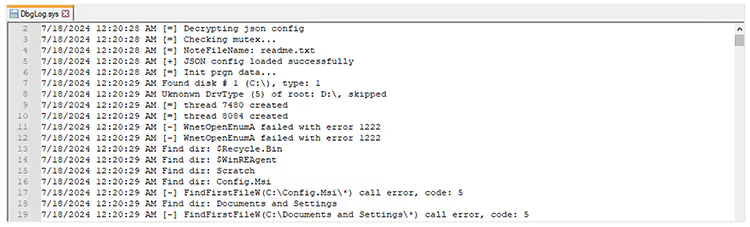
Figure 7. Log file created by the ransomware.
Upon successful execution, the ransomware creates ransom notes with the file name readme.txt.
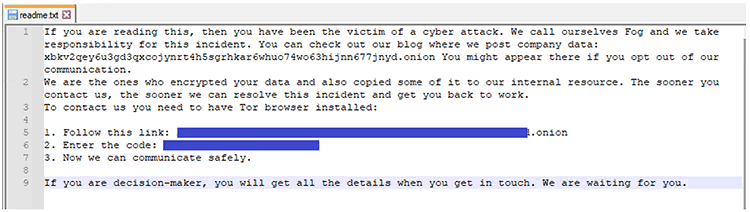
Figure 8. Fog ransom note
Ransom note content:
If you are reading this, then you have been the victim of a cyber attack. We call ourselves Fog and we take responsibility for this incident. You can check out our blog where we post company data: xbkv2qey6u3g3dqxcoyjnrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion You might appear there if you opt out of our communication. We are the ones who encrypted your data and also copied some of it to our internal resource. The sooner you contact us, the sooner we can resolve this incident and get you back to work. To contact us you need to have Tor browser installed:
| ||
|---|---|---|
Modify Registry
The ransomware did not perform any registry key modification.
Mutex
The mutex is the fundamental tool for managing shared resources between multiple threads or processes. Typically, ransomware uses a mutex to avoid reinfecting the victim system and causing multiple layers of encryption. The ransomware creates the following mutex value: XDLJgan1TkNkWfrQ78xVrust07YDq45X.
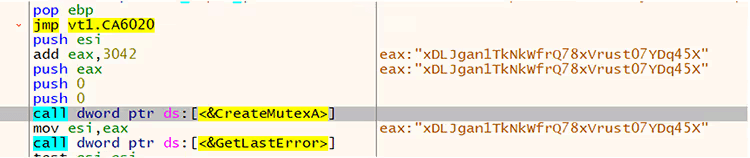
Figure 9. Mutex value created while debugging the ransomware
Network Activity
The ransomware did not try to communicate with a remote server other than encrypting data from mounted shares.
Indicators of Compromise
Indicator | Type | Context |
|---|---|---|
B6360765c786ceee0eb28bee64709172b4e2e066449968e011390be1afd8f36c515edfedadb458be0f569fc2bedb6c4139782516d6faf464b4881739e312e9fabbE67260804526323484f564eebeb6c99ed021b960b899ff788aed85bb7a9d75c3e44c342198e0ad8dd8c0f7bda19d4deb33f0d8355e3e78827505c3b858c82d54 | SHA256 hash | Fog ransomware |
C:\readme.txt | File path | Fog ransom note |
.fog, .flocked, .ffog | Extension | Encrypted file extensions |
vssadmin delete shadows /all /quiet | Process | Volume Shadow Copy deletion |
XDLJgan1TkNkWfrQ78xVrust07YDq45X | Mutex | Mutex value objects created by the Fog ransomware |
xbkv2qey6u3g3dqxcoyjnrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion | URL | TA data leak site (DLS) |
Data Leak Site
The ransom note contains a data leak site (DLS) that, when accessed, displayed the following page, self-identifying the group as Fog:
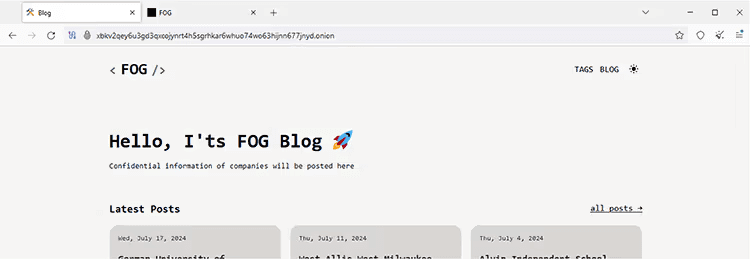
Figure 10. TOR DLS: xbkv2qey6u3gd3qxcojynrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion
Detection Mechanisms
Custom Detections and Blocking with Arete Bloktd℠
SentinelOne S1QL 1.0 query syntax (STAR rule):
Fog Ransomware
Akira Ransomware
Note: These threat hunting queries may need to be tuned for your specific network environment.
Yara
Recommended Mitigations
Utilize an endpoint detection and response (EDR) solution with the capability to halt detected processes and isolate systems on the network based on identified conditions.
Block any known attacker C2s in the firewall.
Implement multi-factor authentication on RDP and VPN to restrict access to critical network resources.
Eliminate unnecessary RDP ports exposed to the internet.
Block a high number of SMB connection attempts from one system to others in the network over a short period of time.
Perform periodic dark web monitoring to verify if data is available for sale on the black market.
Perform penetration tests.
Periodically patch systems and update tools.
Monitor connections to the network from suspicious locations.
Monitor downloads and uploads of files to file-sharing services outside standard work hours.
Monitor file uploads from domain controllers to the internet.
Monitor network scans from uncommon servers (e.g., RDP server).
Organizations can find the full list of US government-recommended ransomware prevention and mitigation guidance here: https://www.cisa.gov/stopransomware/ransomware-guide.
Arete provides data-driven cybersecurity solutions to transform your response to emerging cyber threats. Learn more.
References
At Arete, we envision a world without cyber extortion, where people, businesses, and governments can thrive. We are taking all that we know from over 8,000 engagements to inform our solutions and strengthen powerful tools to better prevent, detect, and respond to the cyber extortion threats of tomorrow. Our elite team of experts provides unparalleled capabilities to address the entire cyber threat lifecycle, from incident response and restoration to advisory and managed security services. To learn more about our solutions, visit www.areteir.com.
Back to Blog Posts

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory

Article
Ransomware Trends & Data Insights: September 2026
The Akira ransomware group re-emerged as the most active ransomware threat observed by Arete in September. Overall activity remained relatively distributed among multiple threat groups, with 29 unique groups observed throughout the month. Alongside Akira, INC Ransom and the relatively new Storm group were among the three most active threat actors observed in September. Several new threat groups also emerged during the month, including Hades Team, Shiba, and Vortex (which is suspected to be part of the cluster of threat actors affiliated with the former BlackFile group).

Throughout the month, analysts at Arete identified several trends behind the threat actors perpetrating cybercrime activities:
In September 2026, the ShinyHunters threat group escalated its extortion activity by publicly targeting both the Clop ransomware group and the FBI. The group claimed to have breached and defaced Clop’s infrastructure, demanding an eight-figure ransom, while separately alleging the theft of sensitive FBI-related data and demanding the retraction of statements made in a prior public advisory. In both incidents, ShinyHunters employed similar pressure tactics, including website defacements, repeated public postings, and threats of data disclosure.
ClickFix attacks remained prevalent in September 2026, with ransomware groups including Qilin, Helix, and The Gentlemen leveraging ClickFix lures to facilitate PowerShell-based payload execution and initial access. The technique continues to evolve, combining social engineering with legitimate tools and services to enable compromise and evade detection.
September 2026 saw continued activity from the former BlackFile extortion ecosystem. BlackFile, a data theft and extortion operation active since at least October 2025, rebranded as Redact in May 2026, and since appears to have broken off into several affiliated brands, including Pink, Helix, Falcon, Cinder, and potentially Vortex. During September, some affiliates publicly disputed these associations and claimed to operate independently. However, the coordinated timing, messaging, and near-identical nature of these statements support the assessment that these groups remain part of a broader interconnected ecosystem operating under shared objectives or coordination.

Article
Attack Patterns in Settra Incidents
Recent Settra ransomware incidents demonstrate a consistent operational pattern involving compromised credentials, VPN access, and the deployment of ransomware executables tailored to victim environments. Researchers have observed Settra naming ransomware executables after the targeted organization's domain while following similar attack sequences across multiple intrusions. Arete has also identified overlapping tactics, techniques, and tools in Settra engagements observed from June to August, including the use of MeshAgent for remote access and Bring Your Own Vulnerable Driver (BYOVD) techniques to weaken endpoint security controls.
What’s Notable and Unique
Settra operators have been observed naming ransomware executables after the victim organization's domain, creating a direct association between the payload and the targeted environment.
Initial access vectors have included targeting exposed VPN infrastructure and the use of compromised credentials, reducing the need for traditional exploitation of vulnerabilities.
Arete observed MeshAgent in multiple Settra engagements, which provides threat actors with a mechanism for remote access and continued activity within compromised environments.
Settra engagements have also included Bring Your Own Vulnerable Driver (BYOVD) activity, which can be used to bypass or impair security controls by abusing legitimate but vulnerable drivers.
Analyst Comments
Recent Settra activity demonstrates how ransomware operators can combine credential-based access, remote management tooling, and security control evasion techniques to establish and maintain access before ransomware deployment. The repeated use of similar tools and operational patterns across incidents provides useful detection opportunities for defenders. Organizations should closely monitor VPN authentication activity, unusual use of compromised credentials, unexpected MeshAgent deployment, ransomware executables with victim-specific naming conventions, and suspicious driver activity associated with attempts to disable or bypass endpoint security controls.
Arete’s MDR practice detects Settra’s full attack chain, with special attention to the staging of BYOVD activity for defense evasion. However, for us to detect it, SentinelOne needs to be fully deployed across an environment. To support organizations with full deployment, Arete offers SentinelOne Deployment Assistance. This service is designed to ensure that SentinelOne is deployed across all eligible endpoints, eliminating coverage gaps that could otherwise expose the organization to ransomware, malware, credential theft, and other advanced threats. Through endpoint discovery, inventory reconciliation, and deployment assistance, Arete helps organizations achieve comprehensive protection and maximize the effectiveness of their SentinelOne investment. Contact clientcares@areteir.com to learn more.
Sources
Ready, Settra, Go: New Settra Ransomware Variant Deploys MeshAgent RMM

Article
AI Agents Used in Campaign Against PaperCut
In late August, a threat actor used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG and MF servers. PaperCut is print management software, and researchers determined that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries. The AI agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078 both security flaws affecting PaperCut software and flagged as actively exploited earlier this month. It is currently unclear if the threat actor is solely focused on access development to be handed off to other affiliated actors, or if they will directly leverage their access to achieve follow-on objectives such as data theft or ransomware deployment.
What’s Notable and Unique
Researchers observed three attack paths following the exploitation of vulnerable PaperCut servers. Threat actors would harvest credentials from LSASS memory and registry secrets to perform pass-the-hash attacks, leverage older unpatched Windows vulnerabilities (CVE-2021-42278 and CVE-2021-42287) to escalate privileges in unpatched environments, or, in some cases, directly add newly created accounts to the Domain Admins group when PaperCut was running with domain-level privileges.
Upon achieving remote code execution and credential harvesting within a self-hosted lab environment, the threat actor deployed hundreds of AI-powered agents that leveraged OpenAI Codex, DeepSeek models, and publicly available offensive security tools, including Mimikatz, SharpHound, Certipy, Rubeus, and Impacket, to automate reconnaissance, exploitation, and post-compromise activities. The attackers subsequently used a DCSync attack to obtain a database dump containing domain credentials.
Analyst Comments
The observed activity demonstrates how threat actors are increasingly leveraging AI and large language models (LLMs) to accelerate cyber operations at unprecedented speed and scale. In this campaign, the adversary progressed from exploit development to remote code execution within hours and, in some cases, achieved Domain Administrator privileges in as little as five minutes. The AI-assisted workflow enabled rapid reconnaissance, exploitation, credential theft, privilege escalation, and lateral movement, allowing the compromise of multiple organizations within seconds. This activity highlights the growing threat posed by AI-enabled adversaries capable of conducting large-scale intrusions with greater efficiency and operational velocity. Organizations affected by the PaperCut vulnerabilities are strongly advised to apply the latest security updates and implement the vendor's recommended mitigation measures to reduce the risk of compromise and unauthorized access.
Sources
Agents Gone Wild: An AI-Orchestrated Global Campaign Against PaperCut NG/MF
AI-powered attack exploited PaperCut flaws to hack 395 organizations
PaperCut Attacker Uses Hundreds of AI Agents to Compromise 440+ Instances