Report
Malware Spotlight: Fog Ransomware
Arete Analysis
Tips
Cybersecurity Trends
Download The Report
Executive Summary
Since April 2024, Arete’s Incident Response (IR) team has responded to multiple engagements attributed to the Fog ransomware group. Engagements attributed to this group have been trending up since mid-June and through July 2024, accounting for nearly 20% of Arete’s ransomware and extortion engagements in July. The Fog ransomware group is especially noteworthy as it is one of the few threat actors specifically targeting one industry: education. Since April, Arete has observed that 70% of Fog victims have been education organizations. This spotlight explores the ransomware group’s observed behavior, background information on the threat actor, and statistics from Incident Response engagements, along with a technical analysis of Fog’s ransomware executable. Finally, we discuss security recommendations to better defend against this evolving cyber threat and mitigate the risk of financial and reputation losses.
Incident Response Data on the Fog Ransomware Group
The information below is based on Fog ransomware incidents investigated by Arete since April 2024. Our IR, Threat Intelligence, and Data Analytics teams work together to analyze key data points during every ransomware engagement and form real-time threat actor (TA) insights.
The median initial demand is $220,000.
The median ransom payment facilitated is $100,000.
36% of engagements involved data exfiltration, often using tools like MEGAsync and Filezilla.
Common initial access vectors include brute force attacks against remote desktop protocol (RDP) and compromised virtual private network (VPN) credentials.
Tools observed during investigations include CobaltStrike, Mimikatz, ngrok, WinRAR, AnyDesk, Advanced Port Scanner, and GMER, among others. The group demonstrates distinct skill in evading common anti-malware defenses.
The ransom note file name is commonly “readme.txt” and includes a link to a TOR site used for negotiations.
The group operates a data leak site (DLS) self-proclaimed as “The Fog Blog.”
Background
Fog ransomware was a prominent newcomer in the second quarter (Q2) of 2024 and demonstrated a noticeable trend of attacking entities in the education sector. Arete engagements involving Fog ransomware more than doubled during July 2024 compared to previous months.
Technical Analysis
Malware analysis revealed that Fog ransomware:
Supports multiple command-line arguments.
Encrypts files on the system and mounted shares.
Adds the following extensions to encrypted files: .fog, .ffog, or .flocked (e.g., file.docx.flocked).
Creates a ransom note with the following filename: readme.txt.
Self-identifies the group as Fog in the ransom note.
References a data leak site in the ransom note that, when accessed, self-identifies the group as Fog.
Kills a list of processes and services.
Maintains a list of whitelisted files and directories to make sure it will not render the system unusable, preventing recovery when running a decryptor.
Attempts to prevent system recovery by deleting the system’s volume shadow copies.
Creates a mutex during execution.
Creates a log file named DbgLog.sys.Execution Pattern/Arguments
Fog ransomware needs command line arguments to execute and encrypt files in the system. Command line arguments supported:
Command line arguments | Description |
|---|---|
-id | Key to decrypt ransomware configuration. |
-nomutex | Skip mutex check. |
-target | Specific location to encrypt files. |
-console | Creates a new console window for output. |
-size | File size threshold to encrypt. |
-log | Log the ransomware activity. |
-procoff | Presently unknown. |
-uncoff | Presently unknown. |
The ransomware will not execute in the system without the “-id” argument followed by a 6-character value that is unique in each engagement.
Execution of the ransomware to encrypt files:
Fog.exe -id [6-characters] Example: | ||
|---|---|---|
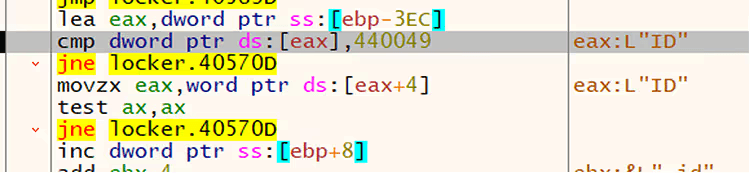
Figure 1. Code in the ransomware to check command line argument “-ID”
The ransomware uses the “-id” argument followed by a 6-character value to decrypt a JSON-based ransomware configuration information at runtime. Decrypted JSON field name and descriptions:
Name | Description |
|---|---|
RSAPubKey | Public key used in the file encryption process. |
LockedExt | Extension added to encrypted files. |
NoteFileName | Ransom note name. |
PathStopList | Excludes listed directories. |
FileMaskStopList | Excludes listed file extensions. |
ShutdownProcesses | Terminates list of processes. |
ShutdownServices | Terminates list of services. |
Stop Services and Processes
Before file encryption, the ransomware terminates a pre-determined list of processes and services to encrypt as many files as possible.
Process names:
“notepad.exe”, “calc.exe”, “*sql*” | ||
|---|---|---|
Service names:
“Dhcp”, “Dnscache”, “*sql*” | ||
|---|---|---|
Code in the ransomware showing this operation:
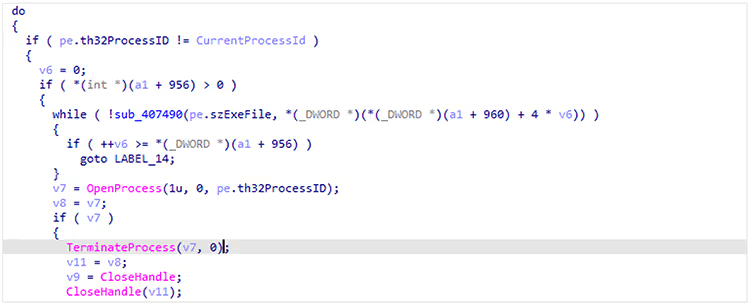
Figure 2. Process termination decompiled code
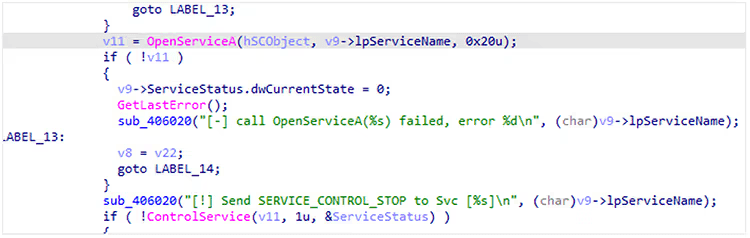
Figure 3. Service termination decompiled code
File and Directory Exclusions
The ransomware excludes system-related files and folders, ransomware-related files, and whitelisted extensions during encryption.
Excluded file extensions:
“*.exe”, “*.dll”, “*.lnk”, “*.sys” | ||
|---|---|---|
Excluded directories:
“tmp”, “winnt”, “Application Data”, “AppData”, “temp”, “thumb”, “$Recycle.Bin”, “System Volume Information”, “Windows”, “Boot” | ||
|---|---|---|
Inhibit System Recovery
Windows operating systems contain features that can help fix corrupted system files, including shadow copies, which are backups of files created by the Volume Shadow Copy Service (VSS). By deleting shadow copies, the ransomware can prevent victims from restoring files from backups, making it more difficult for them to recover their data without paying the ransom.
The ransomware deletes volume shadow copies before file encryption by starting the following process:
cmd.exe /c vssadmin delete shadows /all /quiet | ||
|---|---|---|
System Network Connections Discovery
Fog ransomware can enumerate network-mounted shares by scanning the network interfaces.
Data Encrypted for Impact
The ransomware initially finds available drives and then loads the files one by one using the Windows API FindFirstFileW and FindNextFileW. The ransomware generates random AES keys to encrypt the files, and after encrypting them, the keys are encrypted using a public RSA key. The resulting key is again encrypted and placed at the end of the file.
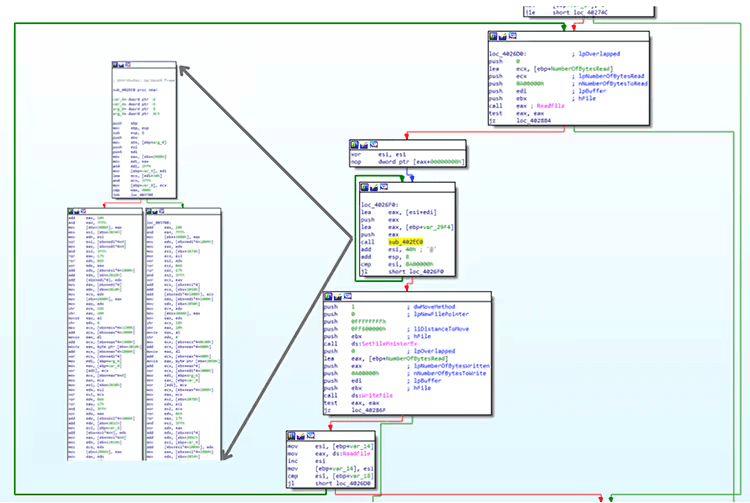
Figure 4. Data encryption code
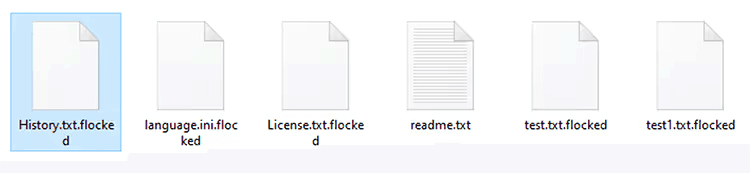
Figure 5. Extension added to the encrypted files
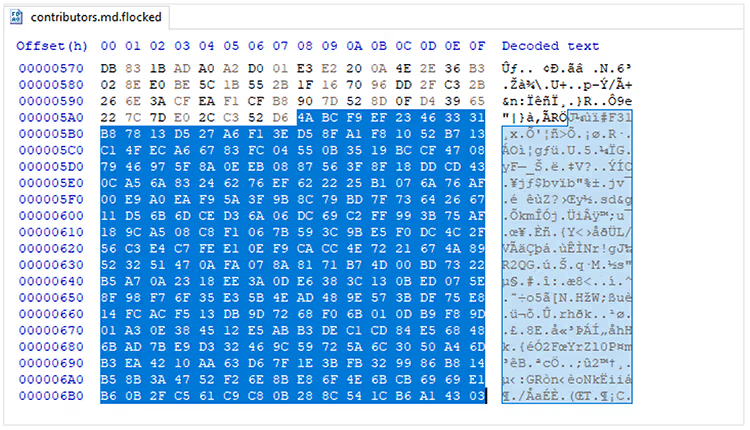
Figure 6. Encrypted AES key appended to encrypted file.
Fog ransomware extensions observed:
“.FOG”, “.FLOCKED”, “.FFOG” | ||
|---|---|---|
During execution, the ransomware creates a file named DbgLog.sys in the same directory and logs the ransomware activity. If the “-log” argument is used during ransomware execution, the ransomware creates and encrypts a lock_log.txt file under the C:\ProgramData directory. Encrypting the lock_log.txt file created might be an oversight in the ransomware code possibly indicating that the ransomware is still under development.
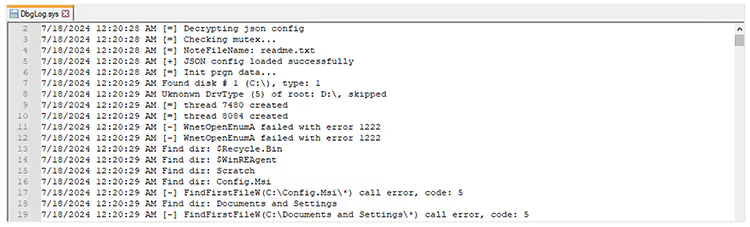
Figure 7. Log file created by the ransomware.
Upon successful execution, the ransomware creates ransom notes with the file name readme.txt.
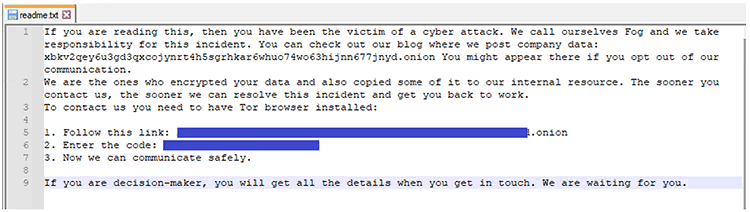
Figure 8. Fog ransom note
Ransom note content:
If you are reading this, then you have been the victim of a cyber attack. We call ourselves Fog and we take responsibility for this incident. You can check out our blog where we post company data: xbkv2qey6u3g3dqxcoyjnrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion You might appear there if you opt out of our communication. We are the ones who encrypted your data and also copied some of it to our internal resource. The sooner you contact us, the sooner we can resolve this incident and get you back to work. To contact us you need to have Tor browser installed:
| ||
|---|---|---|
Modify Registry
The ransomware did not perform any registry key modification.
Mutex
The mutex is the fundamental tool for managing shared resources between multiple threads or processes. Typically, ransomware uses a mutex to avoid reinfecting the victim system and causing multiple layers of encryption. The ransomware creates the following mutex value: XDLJgan1TkNkWfrQ78xVrust07YDq45X.
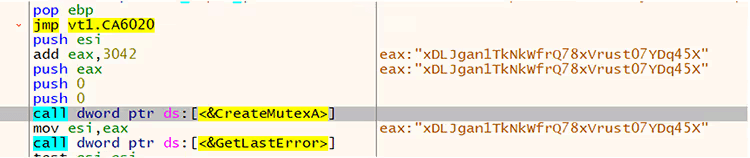
Figure 9. Mutex value created while debugging the ransomware
Network Activity
The ransomware did not try to communicate with a remote server other than encrypting data from mounted shares.
Indicators of Compromise
Indicator | Type | Context |
|---|---|---|
B6360765c786ceee0eb28bee64709172b4e2e066449968e011390be1afd8f36c515edfedadb458be0f569fc2bedb6c4139782516d6faf464b4881739e312e9fabbE67260804526323484f564eebeb6c99ed021b960b899ff788aed85bb7a9d75c3e44c342198e0ad8dd8c0f7bda19d4deb33f0d8355e3e78827505c3b858c82d54 | SHA256 hash | Fog ransomware |
C:\readme.txt | File path | Fog ransom note |
.fog, .flocked, .ffog | Extension | Encrypted file extensions |
vssadmin delete shadows /all /quiet | Process | Volume Shadow Copy deletion |
XDLJgan1TkNkWfrQ78xVrust07YDq45X | Mutex | Mutex value objects created by the Fog ransomware |
xbkv2qey6u3g3dqxcoyjnrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion | URL | TA data leak site (DLS) |
Data Leak Site
The ransom note contains a data leak site (DLS) that, when accessed, displayed the following page, self-identifying the group as Fog:
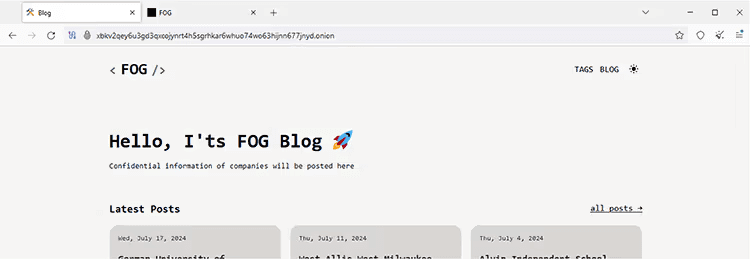
Figure 10. TOR DLS: xbkv2qey6u3gd3qxcojynrt4h5sgrhkar6whuo74wo63hijnn677jnyd[.]onion
Detection Mechanisms
Custom Detections and Blocking with Arete Bloktd℠
SentinelOne S1QL 1.0 query syntax (STAR rule):
Fog Ransomware
Akira Ransomware
Note: These threat hunting queries may need to be tuned for your specific network environment.
Yara
Recommended Mitigations
Utilize an endpoint detection and response (EDR) solution with the capability to halt detected processes and isolate systems on the network based on identified conditions.
Block any known attacker C2s in the firewall.
Implement multi-factor authentication on RDP and VPN to restrict access to critical network resources.
Eliminate unnecessary RDP ports exposed to the internet.
Block a high number of SMB connection attempts from one system to others in the network over a short period of time.
Perform periodic dark web monitoring to verify if data is available for sale on the black market.
Perform penetration tests.
Periodically patch systems and update tools.
Monitor connections to the network from suspicious locations.
Monitor downloads and uploads of files to file-sharing services outside standard work hours.
Monitor file uploads from domain controllers to the internet.
Monitor network scans from uncommon servers (e.g., RDP server).
Organizations can find the full list of US government-recommended ransomware prevention and mitigation guidance here: https://www.cisa.gov/stopransomware/ransomware-guide.
Arete provides data-driven cybersecurity solutions to transform your response to emerging cyber threats. Learn more.
References
At Arete, we envision a world without cyber extortion, where people, businesses, and governments can thrive. We are taking all that we know from over 8,000 engagements to inform our solutions and strengthen powerful tools to better prevent, detect, and respond to the cyber extortion threats of tomorrow. Our elite team of experts provides unparalleled capabilities to address the entire cyber threat lifecycle, from incident response and restoration to advisory and managed security services. To learn more about our solutions, visit www.areteir.com.
Back to Blog Posts

Article
LiteLLM Supply-Chain Compromise
A software supply-chain attack compromised the release pipeline of LiteLLM, a widely used open-source Python SDK and AI gateway. Attackers leveraged the compromised pipeline on October 21st to publish a malicious LiteLLM version through PyPI and associated Docker registries. The affected release, LiteLLM 1.107.0, contained malware designed to steal credentials, sensitive configuration data, private keys, browser information, and other secrets from compromised systems.
What’s Notable and Unique
The incident is particularly significant because LiteLLM provides a common API for applications to interact with AI models from multiple providers. It is reported that the project had approximately 61,800 GitHub stars and 92 million monthly PyPI downloads.
Rather than modifying the core LiteLLM application source code, the threat actors reportedly tampered with the installation package itself. The malware was designed for broad credential and information theft and encrypted the collected data before uploading it to the attacker's endpoint.
The compromise went beyond one-time credential theft. A malicious Python component launched a detached loader that checked a GitHub-hosted pointer every hour and could download Python code from an external server for execution on the compromised machine. This provided threat actors with a mechanism for subsequent remote code execution.
Analyst Comments
Although the malicious packages were subsequently removed, simply uninstalling or deleting the affected LiteLLM package may not be sufficient, because malicious Python startup files or the detached loader could remain on the host. All exposed information should be rotated immediately, and infected systems should be isolated and rebuilt from clean backups. The most recent clean release prior to the attack, LiteLLM 1.106.2, is currently the suggested recovery version.
Sources
LiteLLM release pipeline hacked to distribute info-stealer malware
LiteLLM 1.107.0 Compromised: Python Startup Hooks Steal Cloud, AI, and Proxy Credentials
The Collector Reaches Beyond Provider API Keys

Article
French Supermarket Cyberattack Highlights Risks in Exposed Refrigeration Controllers
Hundreds of French supermarkets were reportedly affected by a cyberattack in which threat actors compromised internet-connected refrigeration controllers and manipulated temperature and defrost settings, which caused refrigeration units to overheat, resulting in widespread food spoilage and significant financial loss. Impacted refrigeration systems were associated with Danfoss, Copeland, and Dixell, and demonstrated how vulnerabilities in industrial control systems (ICS) can disrupt physical operations without relying on conventional data theft or encryption. The attack also raised concerns about the wider exposure of similar devices, as thousands of refrigeration management interfaces remain accessible from the public internet. The incident highlights the growing risk posed by insecure operational technology (OT), particularly where legacy equipment and remote-management interfaces lack adequate security controls.
What’s Notable and Unique
Researchers identified approximately 2,765 internet-accessible Danfoss AK-SM 800A interfaces during assessment. This figure reflects the scope of that research and should not be interpreted as a current count of exposed devices. Publicly accessible management interfaces increase the opportunity for unauthorized access to industrial equipment.
Research also identified several security flaws in the Danfoss AK-SM 800A platform, including an authentication bypass command injection that could enable remote code execution and a weakness involving web-server configuration changes. Danfoss addressed these findings through firmware updates.
Authorities reported compromised Danfoss AK-SM and AK-SC systems, alongside Copeland XWEB and Dixell XWEB monitoring platforms.
Analyst Comments
The incident demonstrates the business consequences of insufficiently secured industrial infrastructure and reinforces the need to integrate OT security into enterprise risk management. Organizations operating connected facility systems should establish clear ownership of industrial assets, enforce secure remote-access policies, and prioritize remediation based on exposure and operational criticality. The findings also highlight the importance of coordinating security teams with facilities and engineering personnel to ensure that protective measures do not compromise essential operations. A risk-based approach to OT security can help organizations reduce exposure while maintaining the availability and reliability of critical equipment.
Sources
France Supermarket Hacks Expose Risks of Internet-Facing Refrigeration Systems
Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers

Article
FortiBleed Campaign Remains Active
The FBI and Secret Service recently warned that the FortiBleed credential-harvesting campaign remains an active threat targeting internet-facing Fortinet FortiGate firewalls and secure socket layer (SSL) virtual private network (VPN) gateways. The agencies report that attackers continue to scan internet-exposed Fortinet firewalls using previously obtained credentials. This has reinforced assessments made by other security researchers, who have stated that “FortiBleed should be treated as an active access operation, not as a one-time credential leak.”
What’s Notable and Unique
FortiBleed, active since February 2026, begins with widespread reconnaissance to identify internet-facing FortiGate firewalls and SSL-VPN services. Once potential targets are identified, operators attempt to gain initial access through credential stuffing, password spraying, and dictionary attacks using previously compromised credentials.
Following successful access, the attackers deploy the Go-based FortigateSniffer tool on compromised appliances. The tool leverages native FortiOS diagnostic functionality to passively intercept authentication traffic across 24 protocols, enabling the collection of cleartext credentials and password hashes passing through the device.
Successfully recovered credentials are reused to expand access, including Active Directory enumeration, Kerberos validation, SMB authentication, and network share discovery, enabling threat actors to move deeper into the victim environment.
Reporting indicates that initial access brokers (IABs) leveraging the FortiBleed attack chain have facilitated access for downstream ransomware operations, including the INC Ransom/Lynx and Payload ransomware groups. This aligns with Arete’s observations of ransomware groups, including INC, Qilin, and DragonForce, targeting Fortinet FortiGate and VPN infrastructure as an initial access vector.
Remediation
Organizations should restrict internet-facing FortiGate management interfaces, rotate administrative and VPN credentials, review local and privileged accounts, and enforce MFA for remote access. If a potential compromise is detected, organizations should isolate affected systems, conduct threat hunting to determine the scope and identify compromised accounts and devices, and preserve relevant logs and artifacts. Organizations should also report the incident to appropriate authorities and implement targeted eviction measures based on identified threat actor activity.
Analyst Comments
FortiBleed represents an ongoing access-enablement threat, rather than a one-time credential exposure. The campaign’s ability to harvest, validate, and reuse credentials can provide sustained access to victim environments and create opportunities for downstream ransomware activity. Organizations with suspected FortiGate exposure should treat the activity as a potential active compromise and investigate for persistent access, compromised accounts, and lateral movement.
Sources
FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts
FBI Warns FortiBleed Remains Active After Amassing 86,644 Fortinet Device Credentials

Article
Threat Actors Exploiting Critical FortiMail Zero-Day Vulnerability
Fortinet has disclosed a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that is currently being exploited as a zero-day in the wild. The flaw, which carries a Critical CVSS score of 9.8, affects the FortiMail management interface and can allow unauthenticated attackers to write arbitrary files to affected systems, potentially leading to unauthorized code execution and full system compromise. Fortinet has confirmed active exploitation and urged customers to implement mitigations immediately while awaiting security updates.
What’s Notable and Unique
The vulnerability stems from improper restriction of file paths combined with improper neutralization of NULL byte characters. An unauthenticated attacker can exploit the flaw via specially crafted HTTP or HTTPS requests to write arbitrary files on the underlying operating system.
Organizations running FortiMail 7.2 can remediate the vulnerability by upgrading to 7.4 or newer. For customers using affected FortiMail 7.4, 7.6, and 8.0 versions, fixes have not yet been released. However, Fortinet has confirmed that the issue will be addressed in the upcoming 7.4.9, 7.6.7, and 8.0.2 releases.
Until the patched versions become available, Fortinet recommends mitigating risk by disabling the Identity-Based Encryption (IBE) feature. As an additional safeguard, administrators should restrict access to the FortiMail management interface, either by removing internet exposure altogether or limiting access to trusted internal networks only. The advisory also includes log entries that administrators can use to identify potentially compromised appliances.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286 to its Known Exploited Vulnerabilities (KEV) catalog and directed federal agencies to perform forensic triage and mitigation by October 4th.
Analyst Comments
Impacted organizations should review their FortiMail instances to ensure there are no unauthorized logins, examine device settings, evaluate all configurations as potentially compromised, and carry out the necessary recovery procedures. Defenders should immediately implement Fortinet's recommended mitigations, review systems for IOC matches, and prepare to deploy the forthcoming security updates as soon as they become available. It is strongly advised that all enterprises assess their setups to reduce risk, as protecting publicly accessible management interfaces is a fundamental security best practice.
Sources
Improper limitation of a pathname to a restricted directory